 Abc11
Army Summit Addresses Cybersecurity for Critical Infrastructure
Article Content

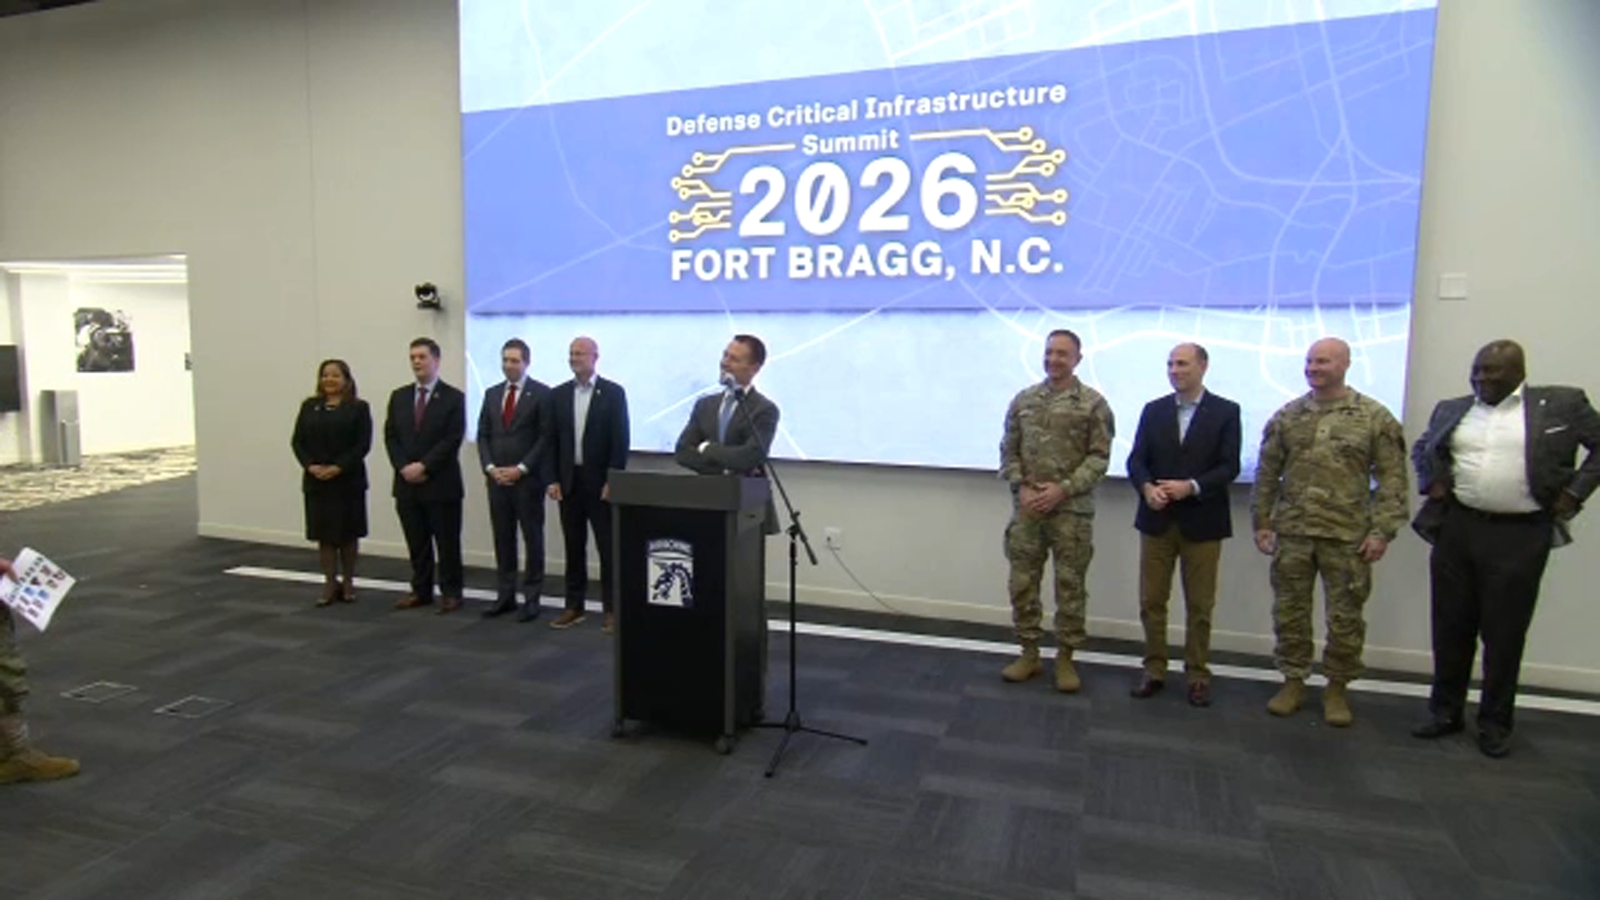
- •The Army's first Defense Critical Infrastructure Summit was held on May 14, 2026.
- •Key threats identified include cybersecurity vulnerabilities, terror threats, and drone attacks.
- •The summit emphasized the importance of partnerships with local utilities for national security.
On May 14, 2026, the U.S. Army held its first Defense Critical Infrastructure Summit at Fort Bragg, focusing on enhancing cybersecurity through collaboration with local and federal partners. The summit included representatives from 14 agencies, including Duke Energy and Fayetteville Technical Community College. Key discussions revolved around protecting critical infrastructure, particularly utilities essential for military operations, from cyber threats and physical attacks. Army leaders identified three primary threats: cybersecurity vulnerabilities, terror threats, and drone attacks. The summit aimed to create a playbook of best practices and strategies to ensure readiness against these threats. The Army's reliance on external utilities for its 288 installations makes these partnerships crucial for maintaining operational capability in times of crisis. Leaders expressed the need for integrated strategies to bolster defenses against increasingly sophisticated cyber threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (13)
Continue Reading
 Hacktivism Transforms into Asymmetric Warfare Tactics Modern hacktivism has evolved into a structured component of global hybrid warfare, blending digital disruptions with real-world impacts. Flashpoint's research highlights significant hacktivist activities linked to the Russia-Ukraine war and the Iran conflict, utilizing crowdsourced infrastructure to target critical…
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…