 Amp.Dw
Australia Forces Chinese Firms to Divest from Rare Earths Miner Amid Security Concerns
Article Content

- •Australia orders six firms, mostly Chinese, to divest from Northern Minerals within 14 days.
- •The divestment affects 17.5% of the company's shares, valued at around $40 million.
- •The government aims to limit Chinese control over critical minerals essential for technology.
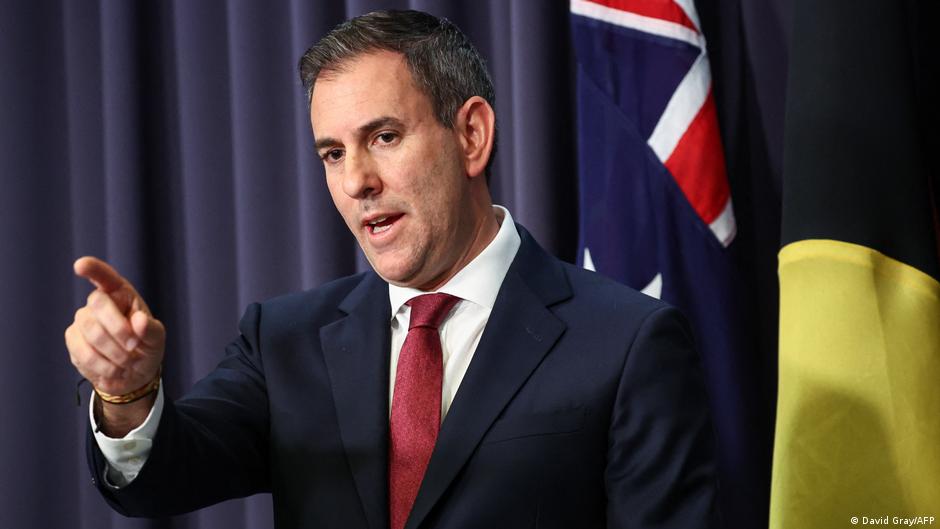
The Australian government has mandated six companies, primarily based in China and Hong Kong, to sell their stakes in Northern Minerals due to fears of foreign interference. Treasurer Jim Chalmers announced that these companies must divest their shares within 14 days, affecting 17.5% of the mining company's shares valued at approximately $40 million. The decision is part of Australia's strategy to reduce China's influence over critical minerals, particularly dysprosium and terbium, essential for technologies like electric vehicles and wind turbines. Previous attempts by Chinese investors to gain control of Northern Minerals have raised alarms, leading to prior divestment orders. The federal government emphasizes compliance with its foreign investment framework to protect national interests. This move follows earlier actions in 2024 when five investors were forced to sell their shares due to similar concerns.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Northern Minerals in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…