 Ia.Acs.Au
Bluetooth Vulnerability Exposes Australian Police Locations
Article Content

- •Axon's tasers and body cameras expose police locations due to Bluetooth security flaws.
- •A hacker demonstrated the ability to track officers using a simple Android app.
- •Police agencies have been informed of the risk but have not taken adequate action.
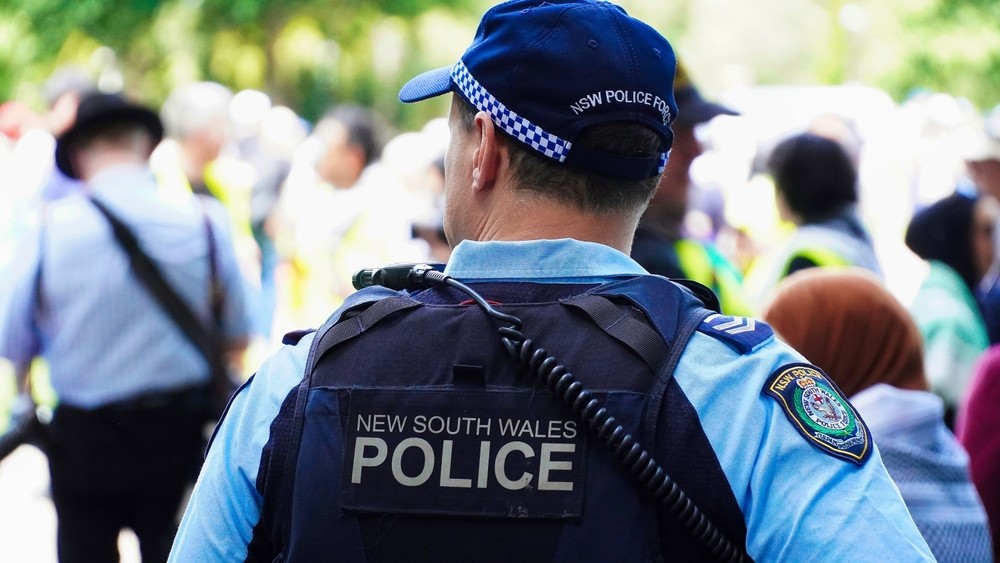
A security flaw in Bluetooth-enabled tasers and body-worn cameras from Axon allows hackers to track Australian police officers' real-time locations using publicly available apps. A hacker demonstrated this vulnerability by detecting multiple devices in a short period, revealing their latitude, longitude, model, and serial numbers. Despite notifying police and national security agencies about the risk in 2024, the hacker received no response, and police agencies have downplayed the threat. The flaw arises from the lack of MAC address randomization, which is standard in many mobile devices. The hacker claims the vulnerability could facilitate pre-planned attacks on police officers. Victoria Police stated they have not experienced unauthorized tracking incidents, but the lack of action raises concerns about officer safety. The issue highlights a significant gap in operational security for law enforcement agencies across Australia.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Axon Enterprise in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Coordinated Attack On October 29, 2026, Binance suffered a large cyberattack attributed to North Korean hackers known as TraderTraitor, resulting in the theft of approximately $6.3 billion in cryptocurrency. The attackers gained initial access through social engineering tactics, including a fake job offer that led to malware…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…