 Theregister
Checkmarx Jenkins Plugin Compromised by TeamPCP Malware Attack
Article Content

- •A malicious Jenkins plugin version was uploaded to the Jenkins Marketplace on May 9, 2026.
- •The compromised plugin can access sensitive data across multiple projects in Jenkins CI pipelines.
- •Users must verify their plugin version and rotate secrets to mitigate risks from the backdoored plugin.
Checkmarx reported a malicious version of its Jenkins AST plugin was uploaded to the Jenkins Marketplace on May 9, 2026. This backdoored plugin, which affects security scans in Jenkins CI pipelines, poses a significant risk as it can compromise multiple projects by exploiting trusted infrastructure. Users are advised to verify they are using the correct version (2.0.13-829.vc72453fa_1c16) released on December 17, 2025. The attack is attributed to TeamPCP, which has previously targeted Checkmarx's tools, including its GitHub Actions plugin and KICS static analysis tool. The malware, dubbed Shail-Hulud, has a CVSS score of 9.4, indicating a critical vulnerability. This incident marks the third compromise of Checkmarx's packages in recent months, raising concerns about the company's security practices. Checkmarx is actively working to remove the malicious plugin and has urged users to rotate their secrets immediately.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (15)
Following this threat?
Track TeamPCP, Shai-hulud and Checkmarx in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
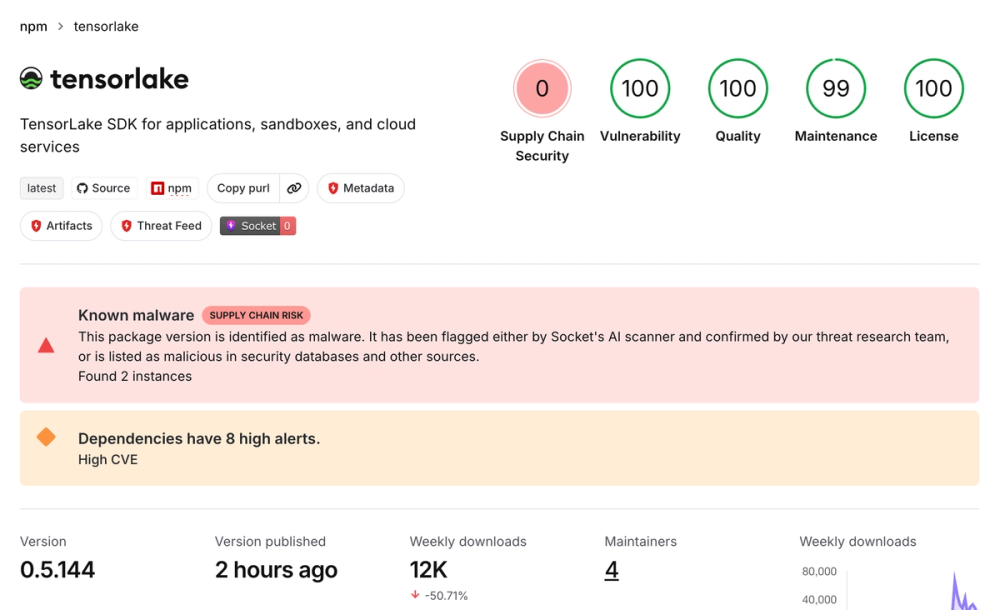 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…