 Atlanticcouncil
China's EV Exports Surge Amid Oil Crisis and Cybersecurity Concerns
Article Content

- •Chinese EV exports surged 78% in Q1 2026 amid rising oil prices.
- •Countries face cybersecurity risks from importing Chinese connected vehicles.
- •US lawmakers warn against lowering barriers for Chinese automobiles due to national security.
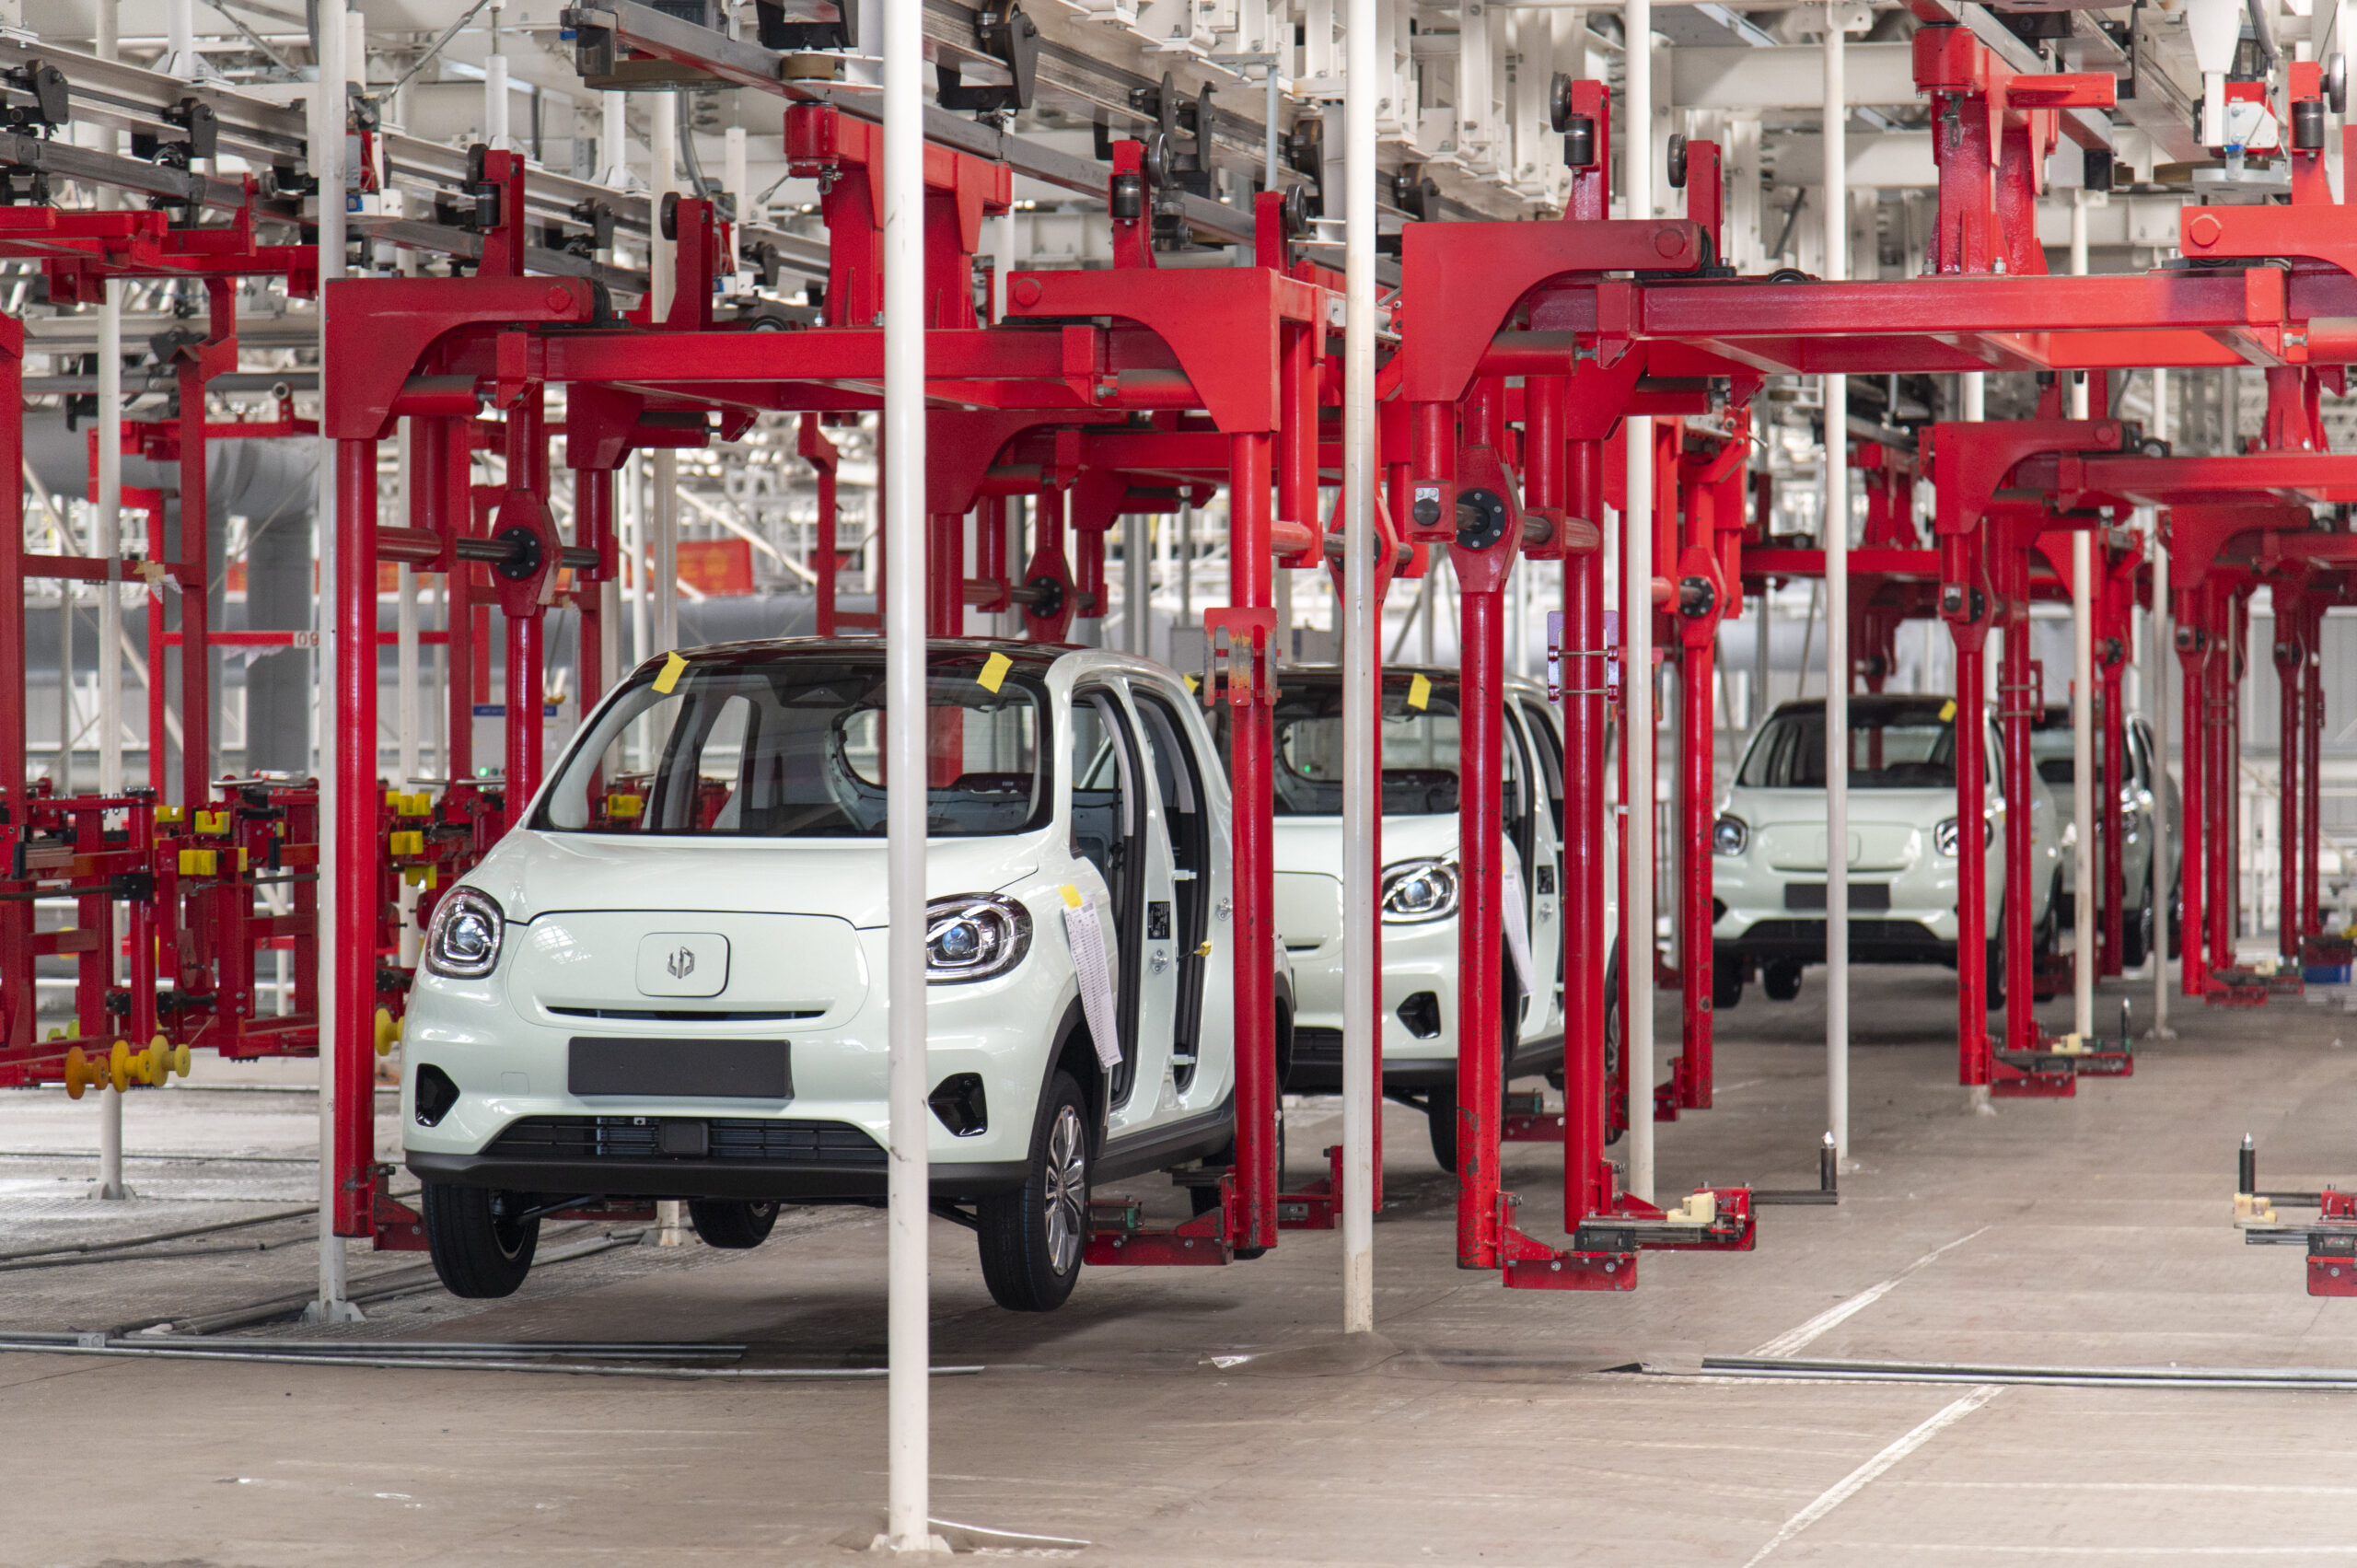
China's electric vehicle (EV) exports have surged significantly, with a 78% increase in the first quarter of 2026 compared to the previous year. This growth is driven by rising oil prices due to the ongoing war in Iran, prompting countries to consider importing Chinese EVs despite potential cybersecurity risks. Chinese automakers are expanding their global footprint, with investments in manufacturing facilities abroad and plans to enter markets like the US and Canada. However, concerns arise over the cybersecurity vulnerabilities of connected vehicles, which could be exploited by Chinese state actors. Countries face a dilemma between economic relief from high oil prices and the risks associated with dependence on Chinese technology. The situation is compounded by warnings from US lawmakers against lowering barriers for Chinese automobiles, citing national security implications. As the global demand for EVs grows, the balance between economic needs and cybersecurity risks remains precarious.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…