 Npr
Congress Investigates Polymarket for Insider Trading on Iran Ceasefire Bets
Article Content

- •Over 50 new accounts on Polymarket placed bets on a U.S.-Iran ceasefire before its announcement.
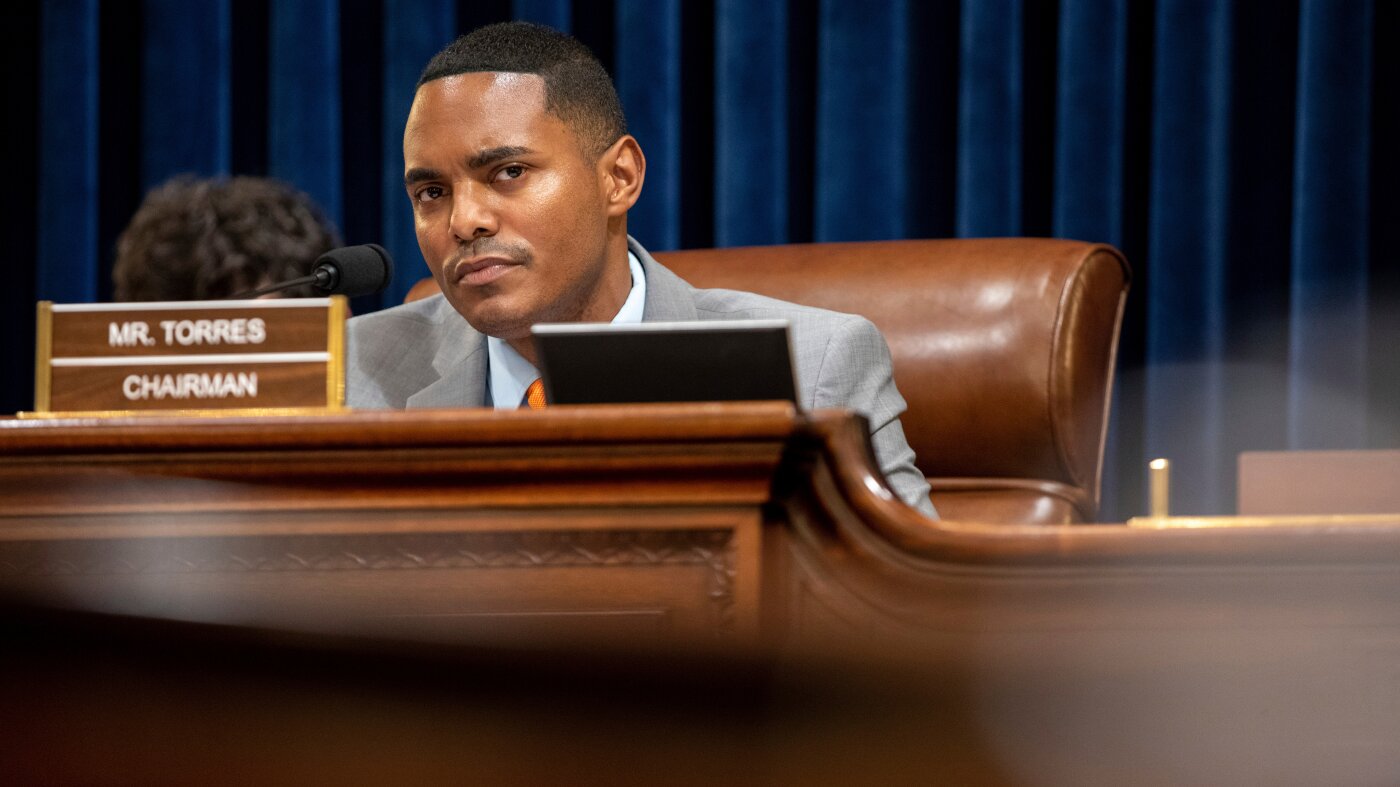
- •Rep. Ritchie Torres has called for an investigation into potential insider trading practices.
- •Previous incidents of suspicious betting on geopolitical events have raised concerns about market integrity.
U.S. lawmakers are calling for investigations into Polymarket after multiple new accounts placed significant bets on a U.S.-Iran ceasefire just before it was announced by President Trump on April 9, 2026. At least 50 new accounts made these bets, raising suspicions of insider trading. This follows a pattern of similar bets tied to other geopolitical events, including a $400,000 profit from a bet on Venezuelan leader Nicolas Maduro's capture. Representative Ritchie Torres has demanded that the Commodity Futures Trading Commission investigate these trades, highlighting the improbability of such accurate predictions without insider knowledge. The situation has prompted concerns about the integrity of prediction markets and their susceptibility to exploitation by individuals with access to confidential information. Blumenthal has previously introduced legislation aimed at regulating prediction markets to prevent such abuses. The current status remains under investigation as lawmakers seek accountability from Polymarket.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…