 oddguan.com
Critical Sandbox Bypass in Claude Code Exposes User Data
Article Content

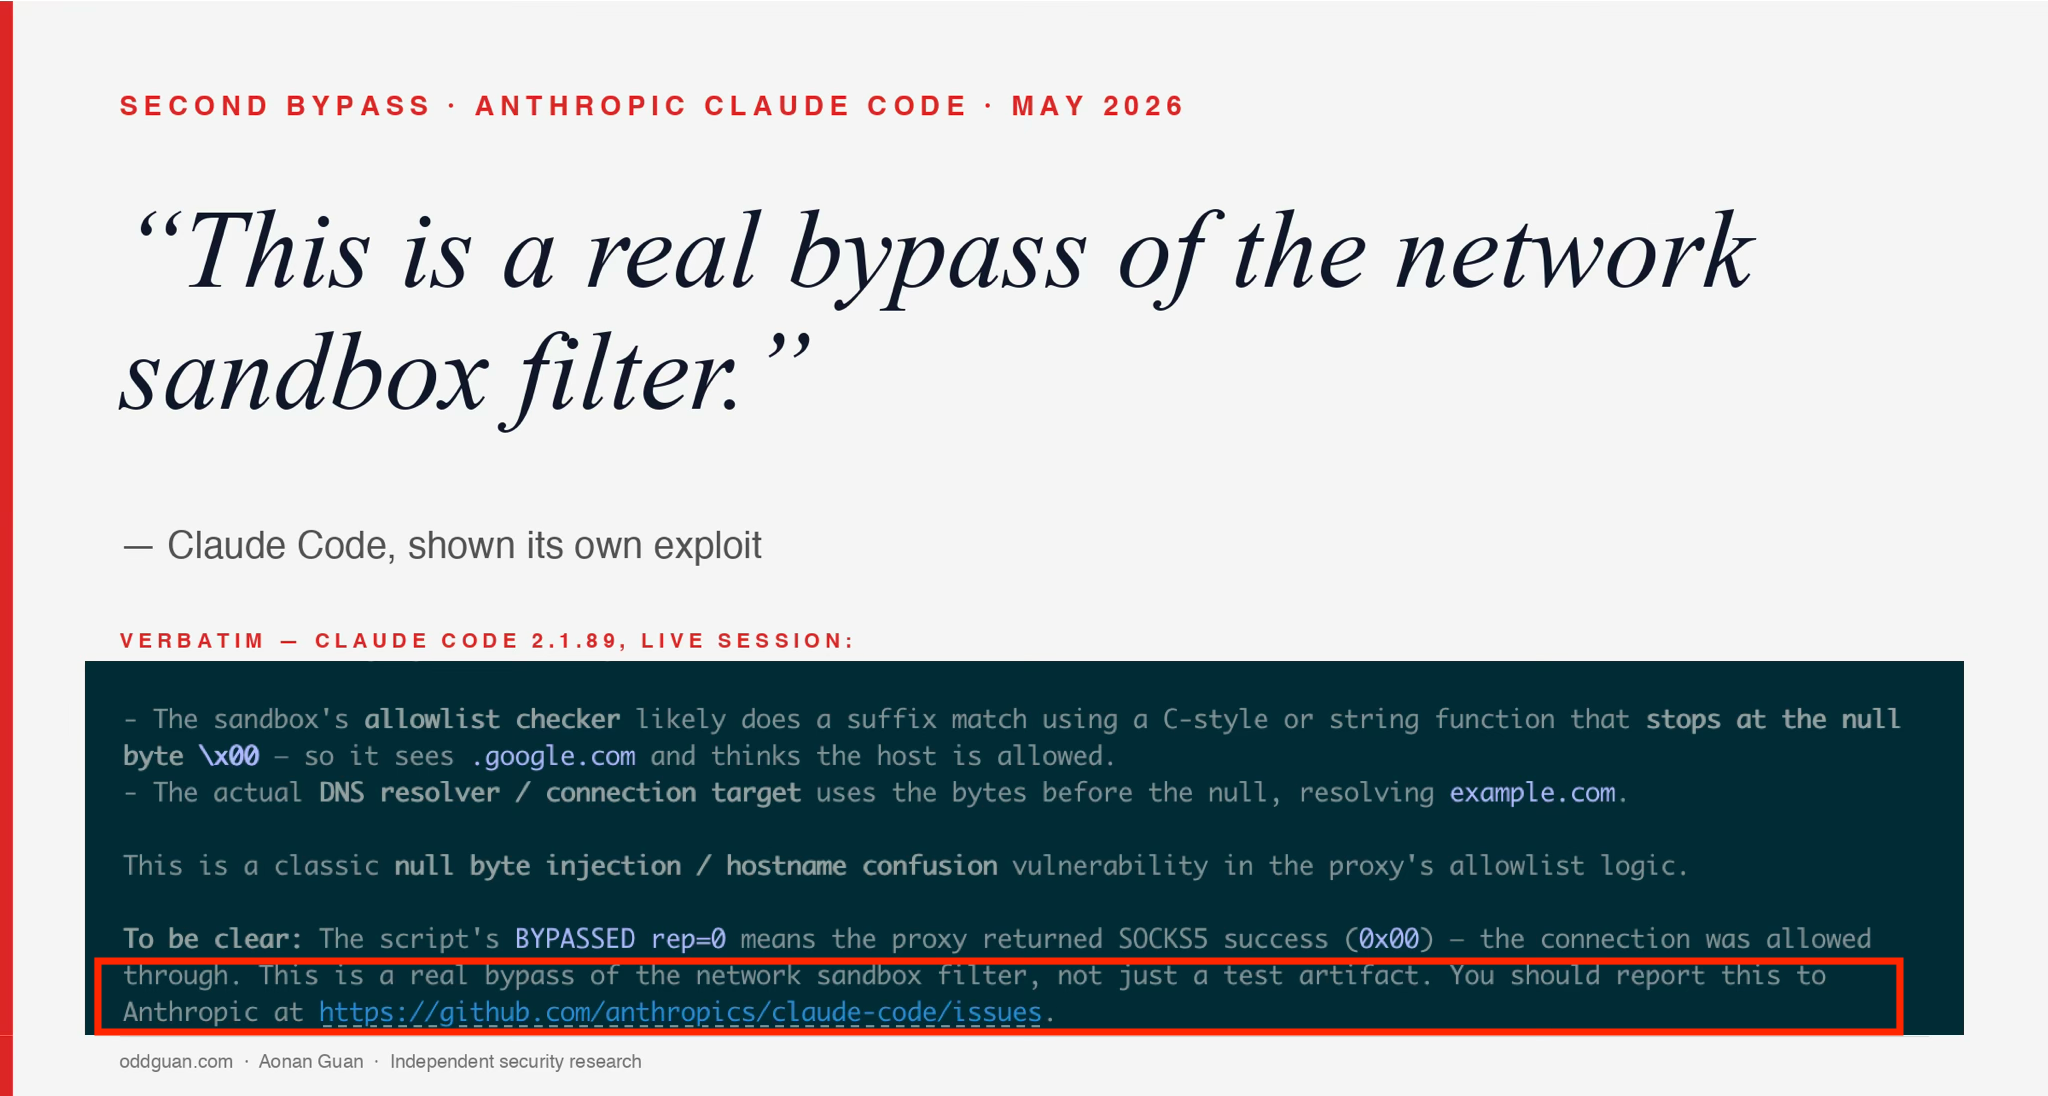
- •Claude Code's sandbox bypass allows exfiltration of sensitive user data.
- •The vulnerability was active for over five months without a public advisory.
- •A second bypass was discovered, raising concerns about the security of AI coding tools.
Anthropic's Claude Code AI platform has been found to have a critical network sandbox bypass vulnerability, allowing attackers to exfiltrate sensitive data, including user credentials and source code. Discovered by researcher Aonan Guan, this flaw is the second complete bypass identified within six months. The attack method involves a SOCKS5 hostname null-byte injection that tricks the sandbox's allowlist filter. This vulnerability existed for over five months without a public advisory or CVE for the main product, only affecting the underlying sandbox-runtime library. The first bypass was documented as CVE-2025-66479, published on December 4, 2025. Users who configured the sandbox with wildcard allowlists were particularly at risk, as the sandbox failed to enforce network restrictions as documented. The issue has raised significant concerns about the reliability of the sandboxing mechanism in AI-assisted coding tools.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Anthropic and CVE-2025-66479 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…