 Cybersecuritynews
CrystalX RAT: New Malware Combines Data Theft and Prankware Features
Article Content

- •CrystalX RAT combines data theft and prankware features, making it a unique threat.
- •The malware is marketed as a MaaS, allowing less skilled attackers to access its capabilities.
- •Initial infection vector is unknown, but it is rapidly evolving with new versions detected.
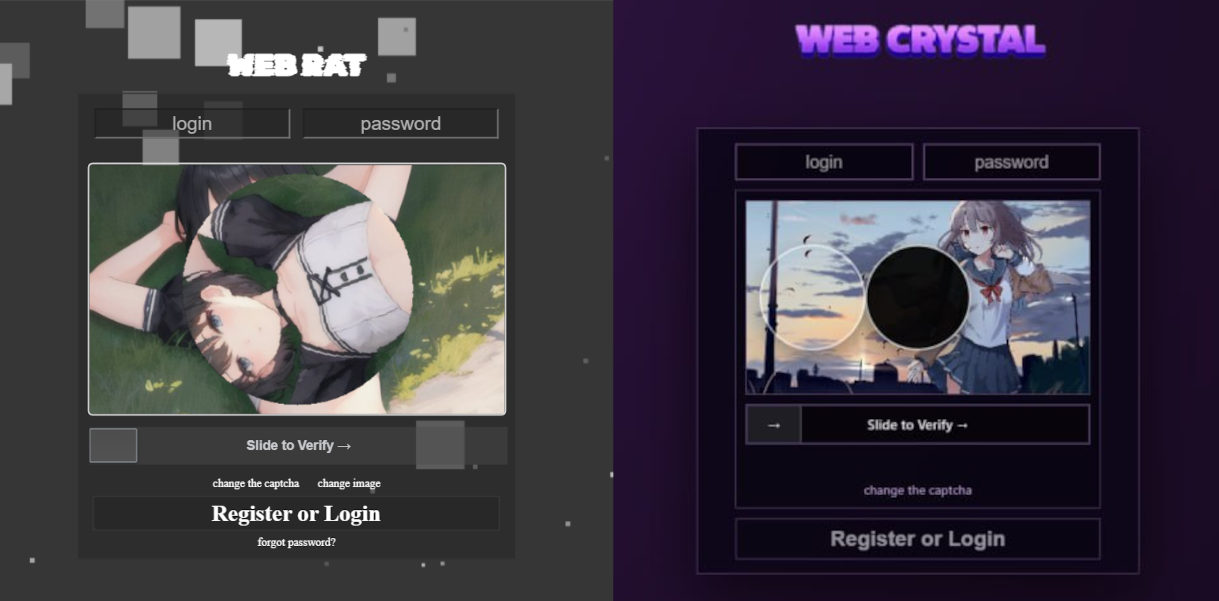
In March 2026, cybersecurity researchers discovered CrystalX RAT, a new malware-as-a-service (MaaS) being promoted in private Telegram channels. This malware offers a wide range of capabilities, including remote access, data theft, keylogging, and unique prankware features designed to disrupt and mock victims. CrystalX RAT can steal credentials from platforms like Steam, Discord, and Telegram, and manipulate clipboard contents to facilitate cryptocurrency theft. The malware was first identified in January 2026 as WebCrystal RAT before being rebranded. It operates on a subscription model with three tiers, making it accessible to less skilled cybercriminals. The malware connects to its command-and-control server via WebSocket and has been noted for its user-friendly interface. As of the latest reports, the initial infection vector remains unknown, but the malware is actively evolving, with new versions being detected. Victims are primarily located in Russia, and the threat is expected to grow.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (10)
Following this threat?
Track CrystalX in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…