 Whichcar.Au
Cybersecurity Risks in Connected Vehicles: A Growing Concern
Article Content

- •Connected vehicles are increasingly vulnerable to cyber attacks.
- •A ransomware attack on Jaguar Land Rover disrupted production and services.
- •Regulations are in place to enhance cybersecurity in new vehicles.
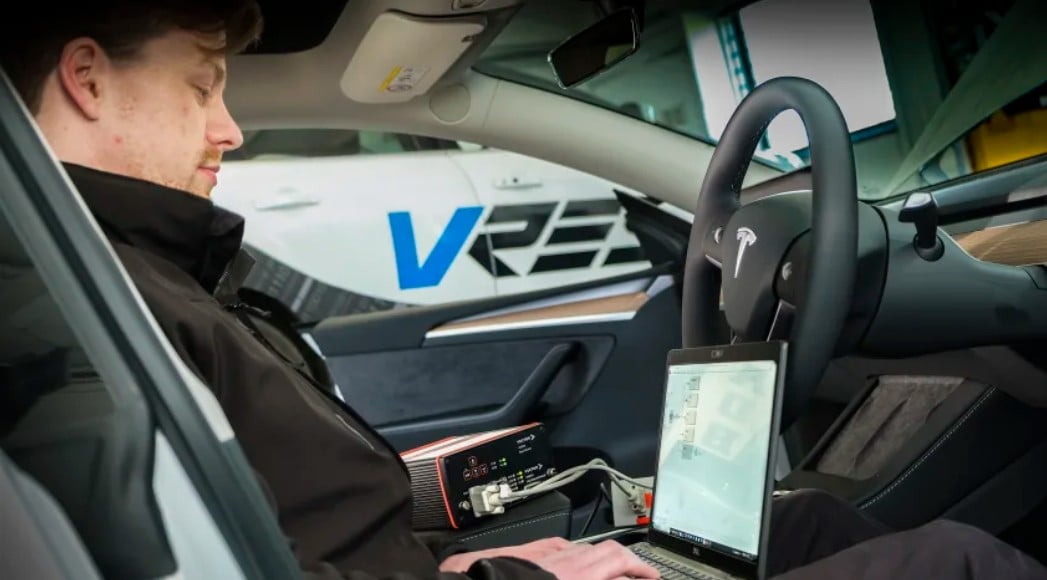
As vehicles become increasingly connected, the risk of cyber attacks on automotive systems rises. Experts warn that cars, now functioning like internet devices, could be targeted by cyber criminals. A ransomware attack on Jaguar Land Rover highlighted the potential for disruption within the automotive ecosystem, affecting production and delivery. While direct hacks on vehicles remain rare, vulnerabilities in electronic systems pose significant safety risks. Regulations, such as the United Nations Regulation No. 155, have been implemented to enhance cybersecurity standards in new vehicles. Hyundai's advanced technology facility in Frankfurt is actively working on strengthening defenses against potential threats. Data theft from infotainment systems is also a growing concern, with personal information at risk. The automotive industry must remain vigilant as the threat landscape continues to evolve.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Jaguar Land Rover in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…