 Bleepingcomputer
Enterprises Struggle with Stolen Credential Threats in 2026
Article Content

- •85% of organizations consider stolen credentials a high security risk.
- •Only 32% of enterprises use dedicated credential monitoring solutions.
- •Breaches involving compromised credentials can cost up to $4.88 million.
In 2026, stolen credentials are identified as a critical cybersecurity risk, with 85% of organizations ranking them as a high priority. Despite this, many enterprises rely on inadequate checkbox solutions and generic tools, believing that measures like MFA and zero-trust frameworks provide sufficient protection. However, these approaches fail to safeguard against attacks when employees access critical SaaS services from unmanaged devices. The IBM Cost of a Data Breach Report indicates that breaches involving compromised credentials cost between $4.81-4.88 million. Lunar's monitoring revealed 4.17 billion compromised credentials in 2025, highlighting the scale of the issue. Only 32% of surveyed enterprises utilize dedicated credential monitoring solutions, while 17% lack any tooling. The lack of forensic detail in existing solutions leaves organizations vulnerable to infostealer threats. A shift in enterprise mindset is necessary to develop a comprehensive defense strategy against these evolving threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Acreed in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Mass Credential Exposures Across Major Corporations Lunar Cyber reported 747,485 credential exposure events linked to ten large organizations, primarily in technology, finance, and retail. The analysis revealed that infostealer malware and breach databases were responsible for these exposures, with Apple showing over 46 million total events, but only 209,767 tied to…
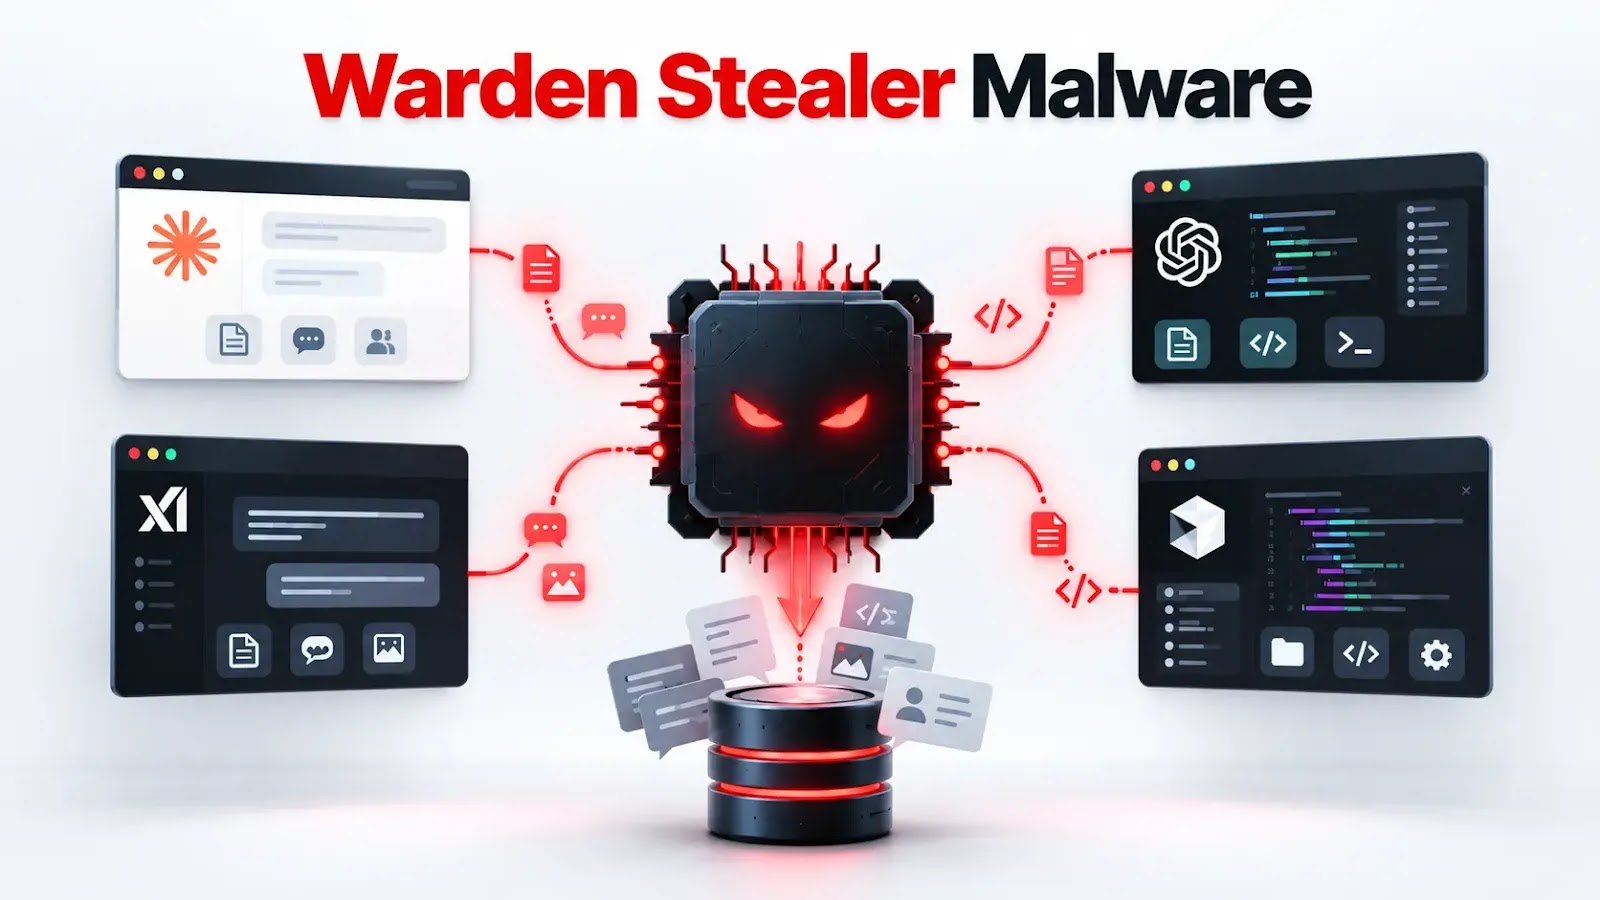 Warden Stealer Malware Targets AI Agents for Data Theft Warden Stealer, a sophisticated malware-as-a-service, is actively targeting AI agents like Claude, Codex, Grok, and Cursor to steal sensitive developer data. This Rust-based infostealer collects configuration files, tokens, and conversation histories, posing a significant threat to organizations using AI tools. The…