 Channelnewsasia
EU Firms Shift Strategies Amid China's Rare Earths Export Controls
Article Content

- •EU firms are rethinking operations in China due to export controls on rare earths.
- •The licensing process for rare earth exports is slow and lacks transparency.
- •The EU is stopping funding for projects using Chinese inverters to support local manufacturers.
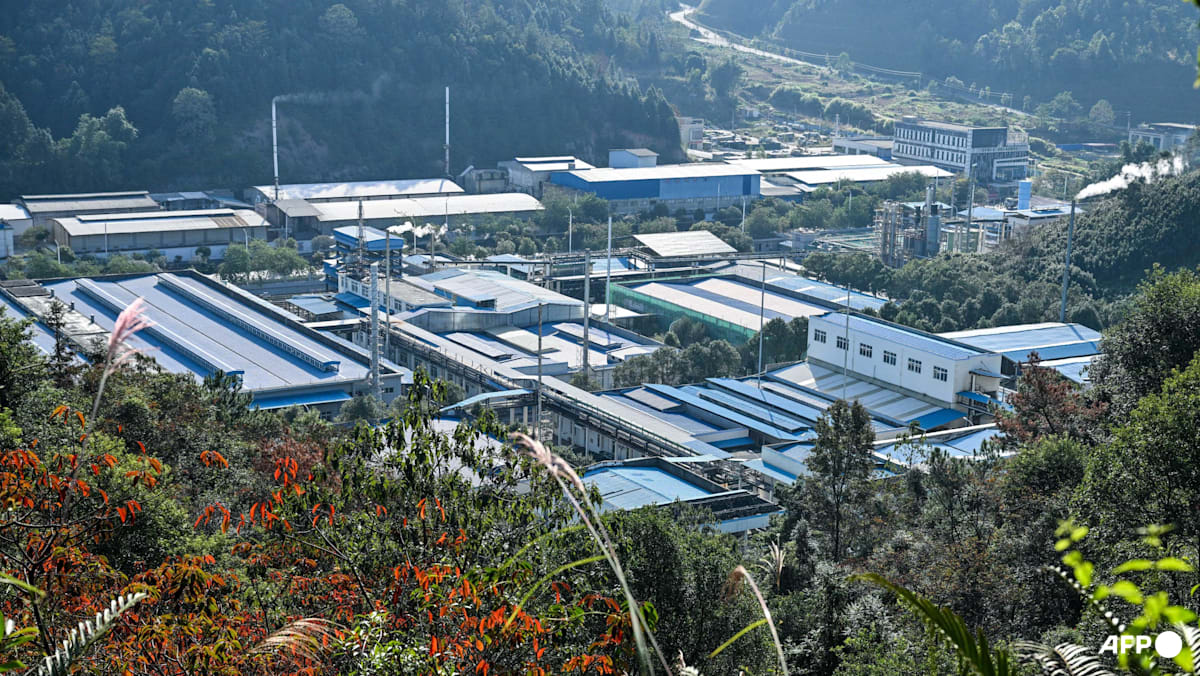
European firms are reevaluating their operations in China due to stringent export controls on rare earths, which are crucial for various industries including defense and consumer electronics. The European Union Chamber of Commerce in China reported that the licensing process for exporting these materials is slow and lacks transparency, posing a long-term business risk. This shift in mindset comes after many companies faced unexpected disruptions during the China-US trade war. Concurrently, the EU is halting funding for clean technology projects that involve Chinese-made inverters, reflecting a broader strategy to support local manufacturers and mitigate security risks associated with Chinese technology. This change in funding policy was quietly approved by European Commission President Ursula von der Leyen and aims to curb reliance on Chinese products. The overall impact includes a potential economic shift as European firms seek alternative suppliers and strategies to ensure operational continuity.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…