 www.atlanticcouncil.org
Europe's Push for Digital Sovereignty Amid US Dependency Concerns
Article Content

- •European leaders are prioritizing digital sovereignty to reduce reliance on US technology.
- •Concerns about US legal actions have intensified skepticism towards US cloud services.
- •Major tech firms are launching initiatives to reassure European clients, but doubts persist.
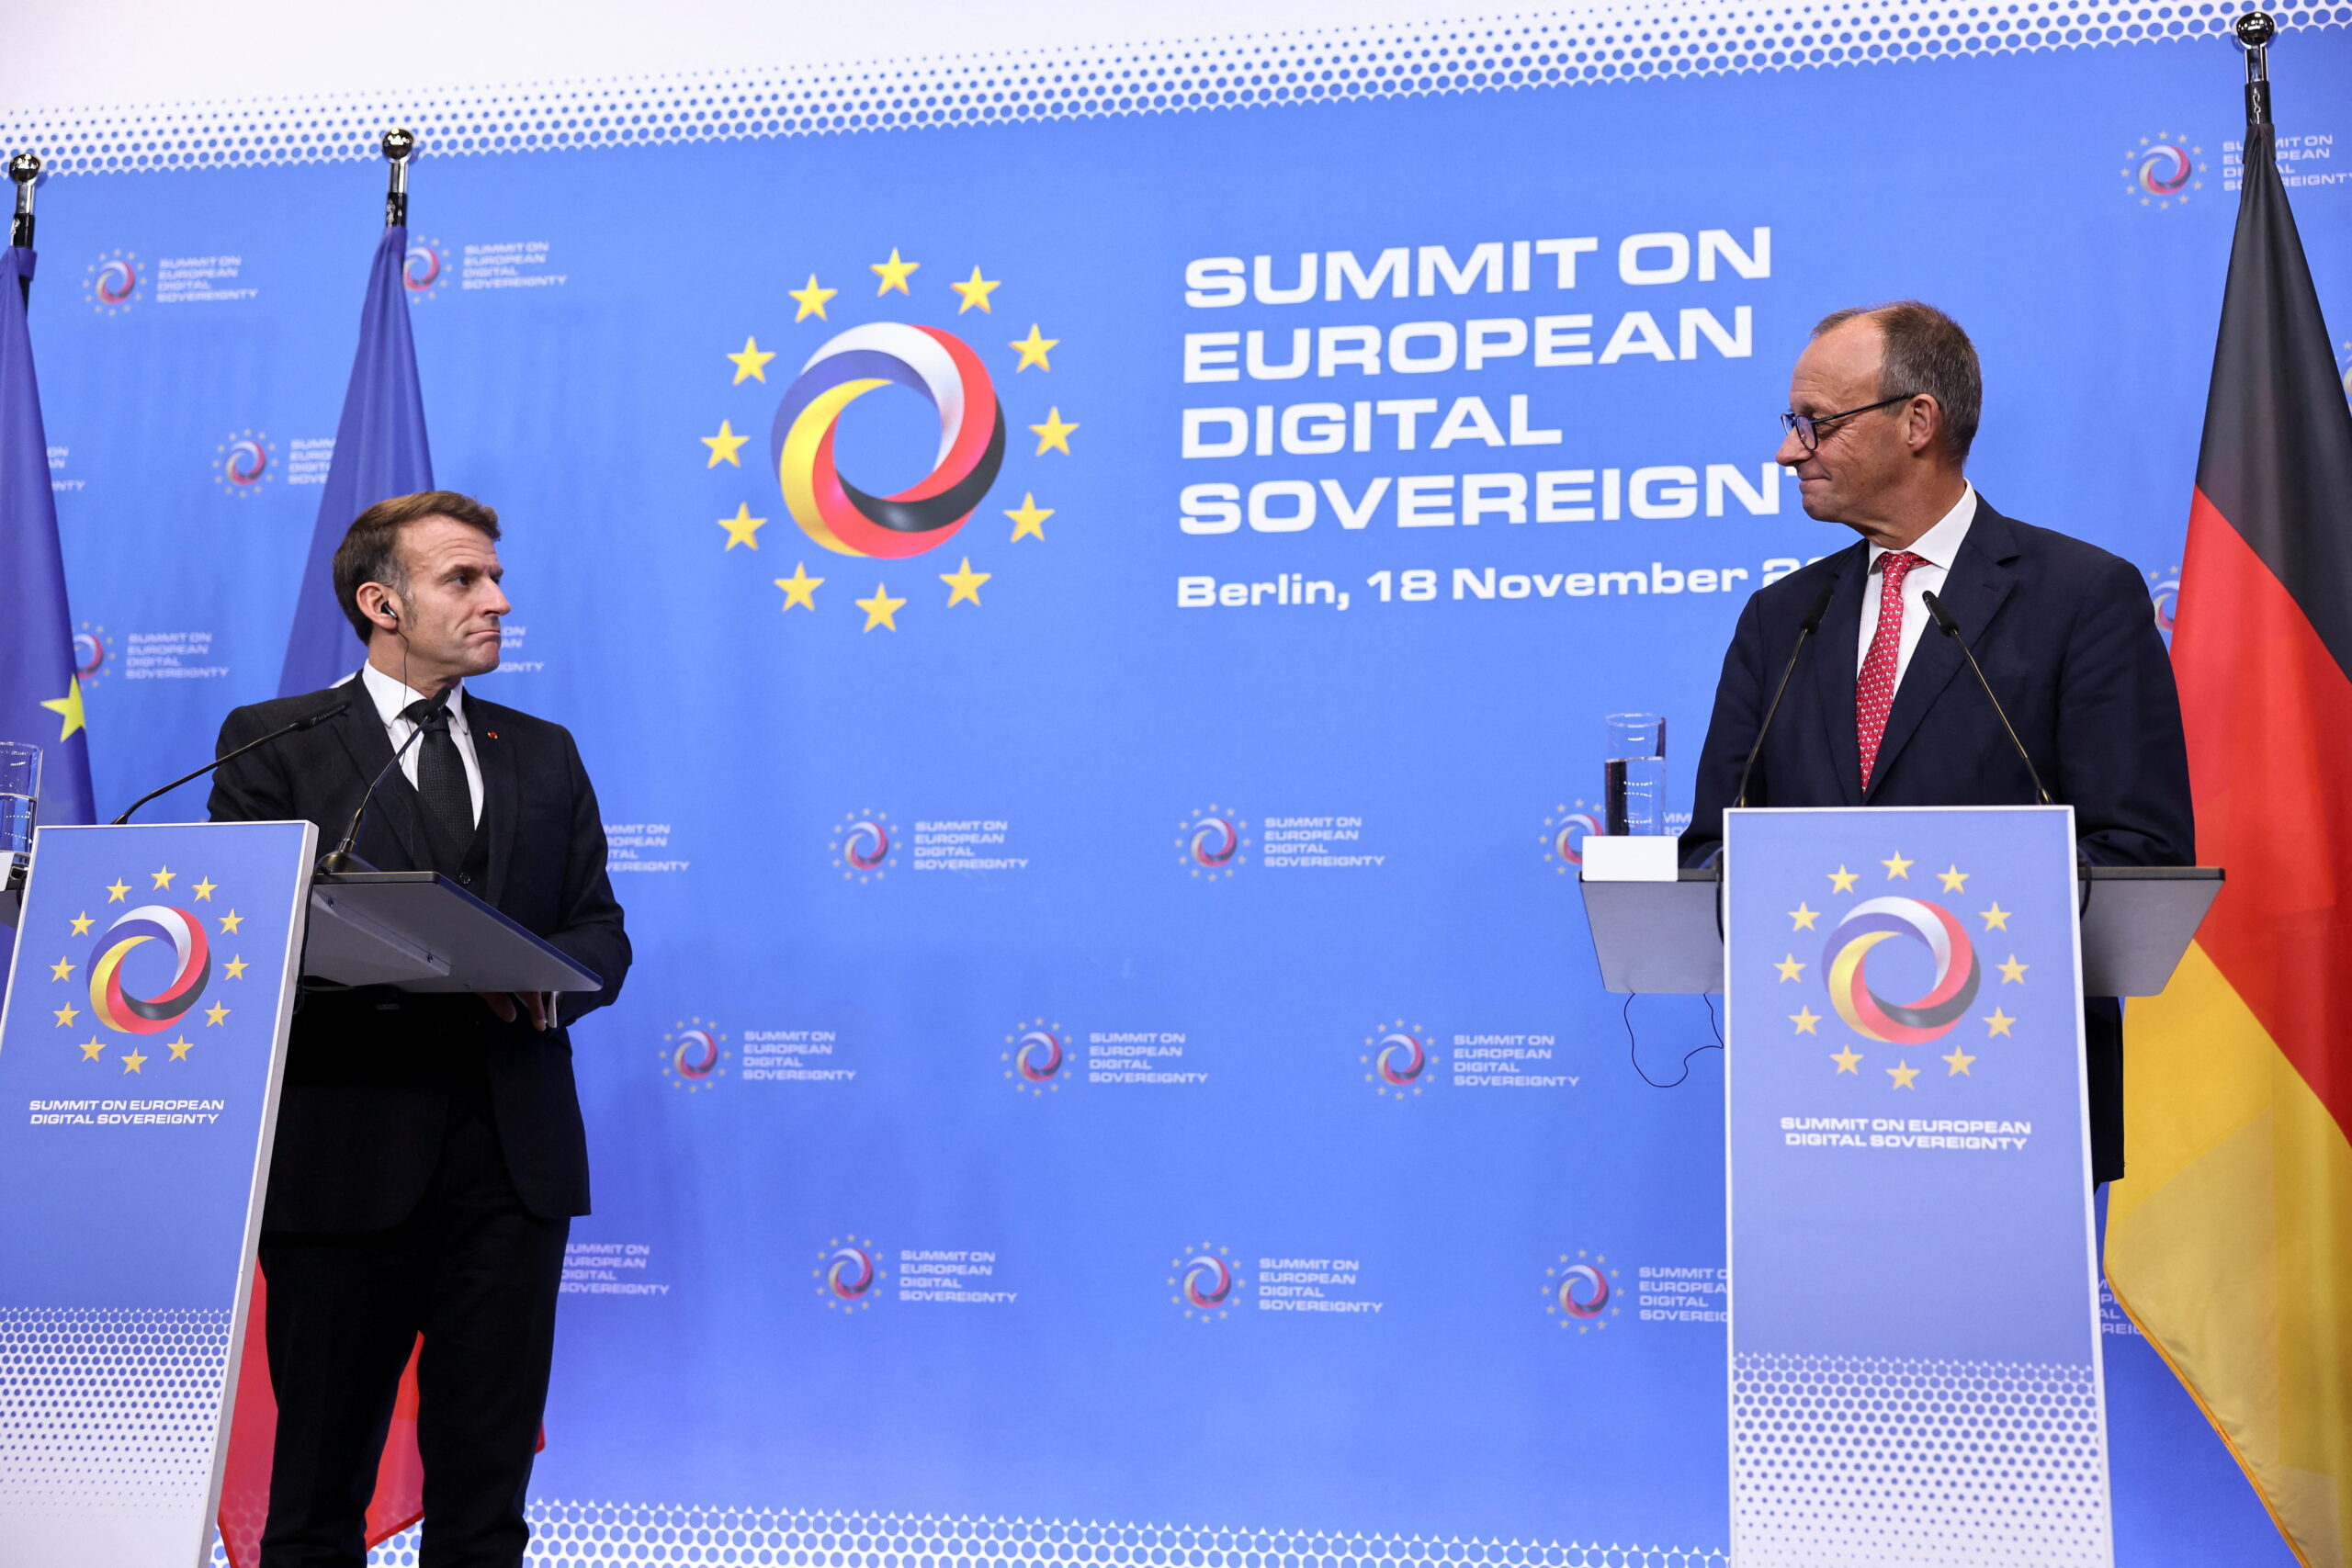
In 2026, European leaders are increasingly advocating for digital sovereignty, emphasizing the need to reduce reliance on US technology. This shift follows significant events, including sanctions imposed by the Trump administration on international entities, which highlighted vulnerabilities in US-hosted services. Major tech companies like Microsoft and AWS are attempting to reassure European clients with initiatives like the EU Data Boundary and Sovereign Cloud offerings. However, skepticism remains high among European governments and companies, who fear that these measures cannot guarantee immunity from US legal actions. The discussions around digital sovereignty were notably prominent at KubeCon Europe 2026, where experts expressed concerns over the risks of dependency on US tech. Thierry Carrez from the Linux Foundation Europe articulated that the situation is not merely theoretical, citing past incidents where US companies complied with government demands. The concept of digital sovereignty is evolving from a theoretical framework to a practical agenda, with potential implications for EU procurement policies and regulatory measures against non-European companies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…