 Theregister
Former NSA Chiefs Warn of Cybersecurity Complacency and Evolving Threats
Article Content

- •Former NSA directors express concern over U.S. complacency towards cyber threats.
- •Panelists emphasize the need for a cohesive federal cybersecurity strategy.
- •Growing threats from AI and state actors like China pose significant risks.
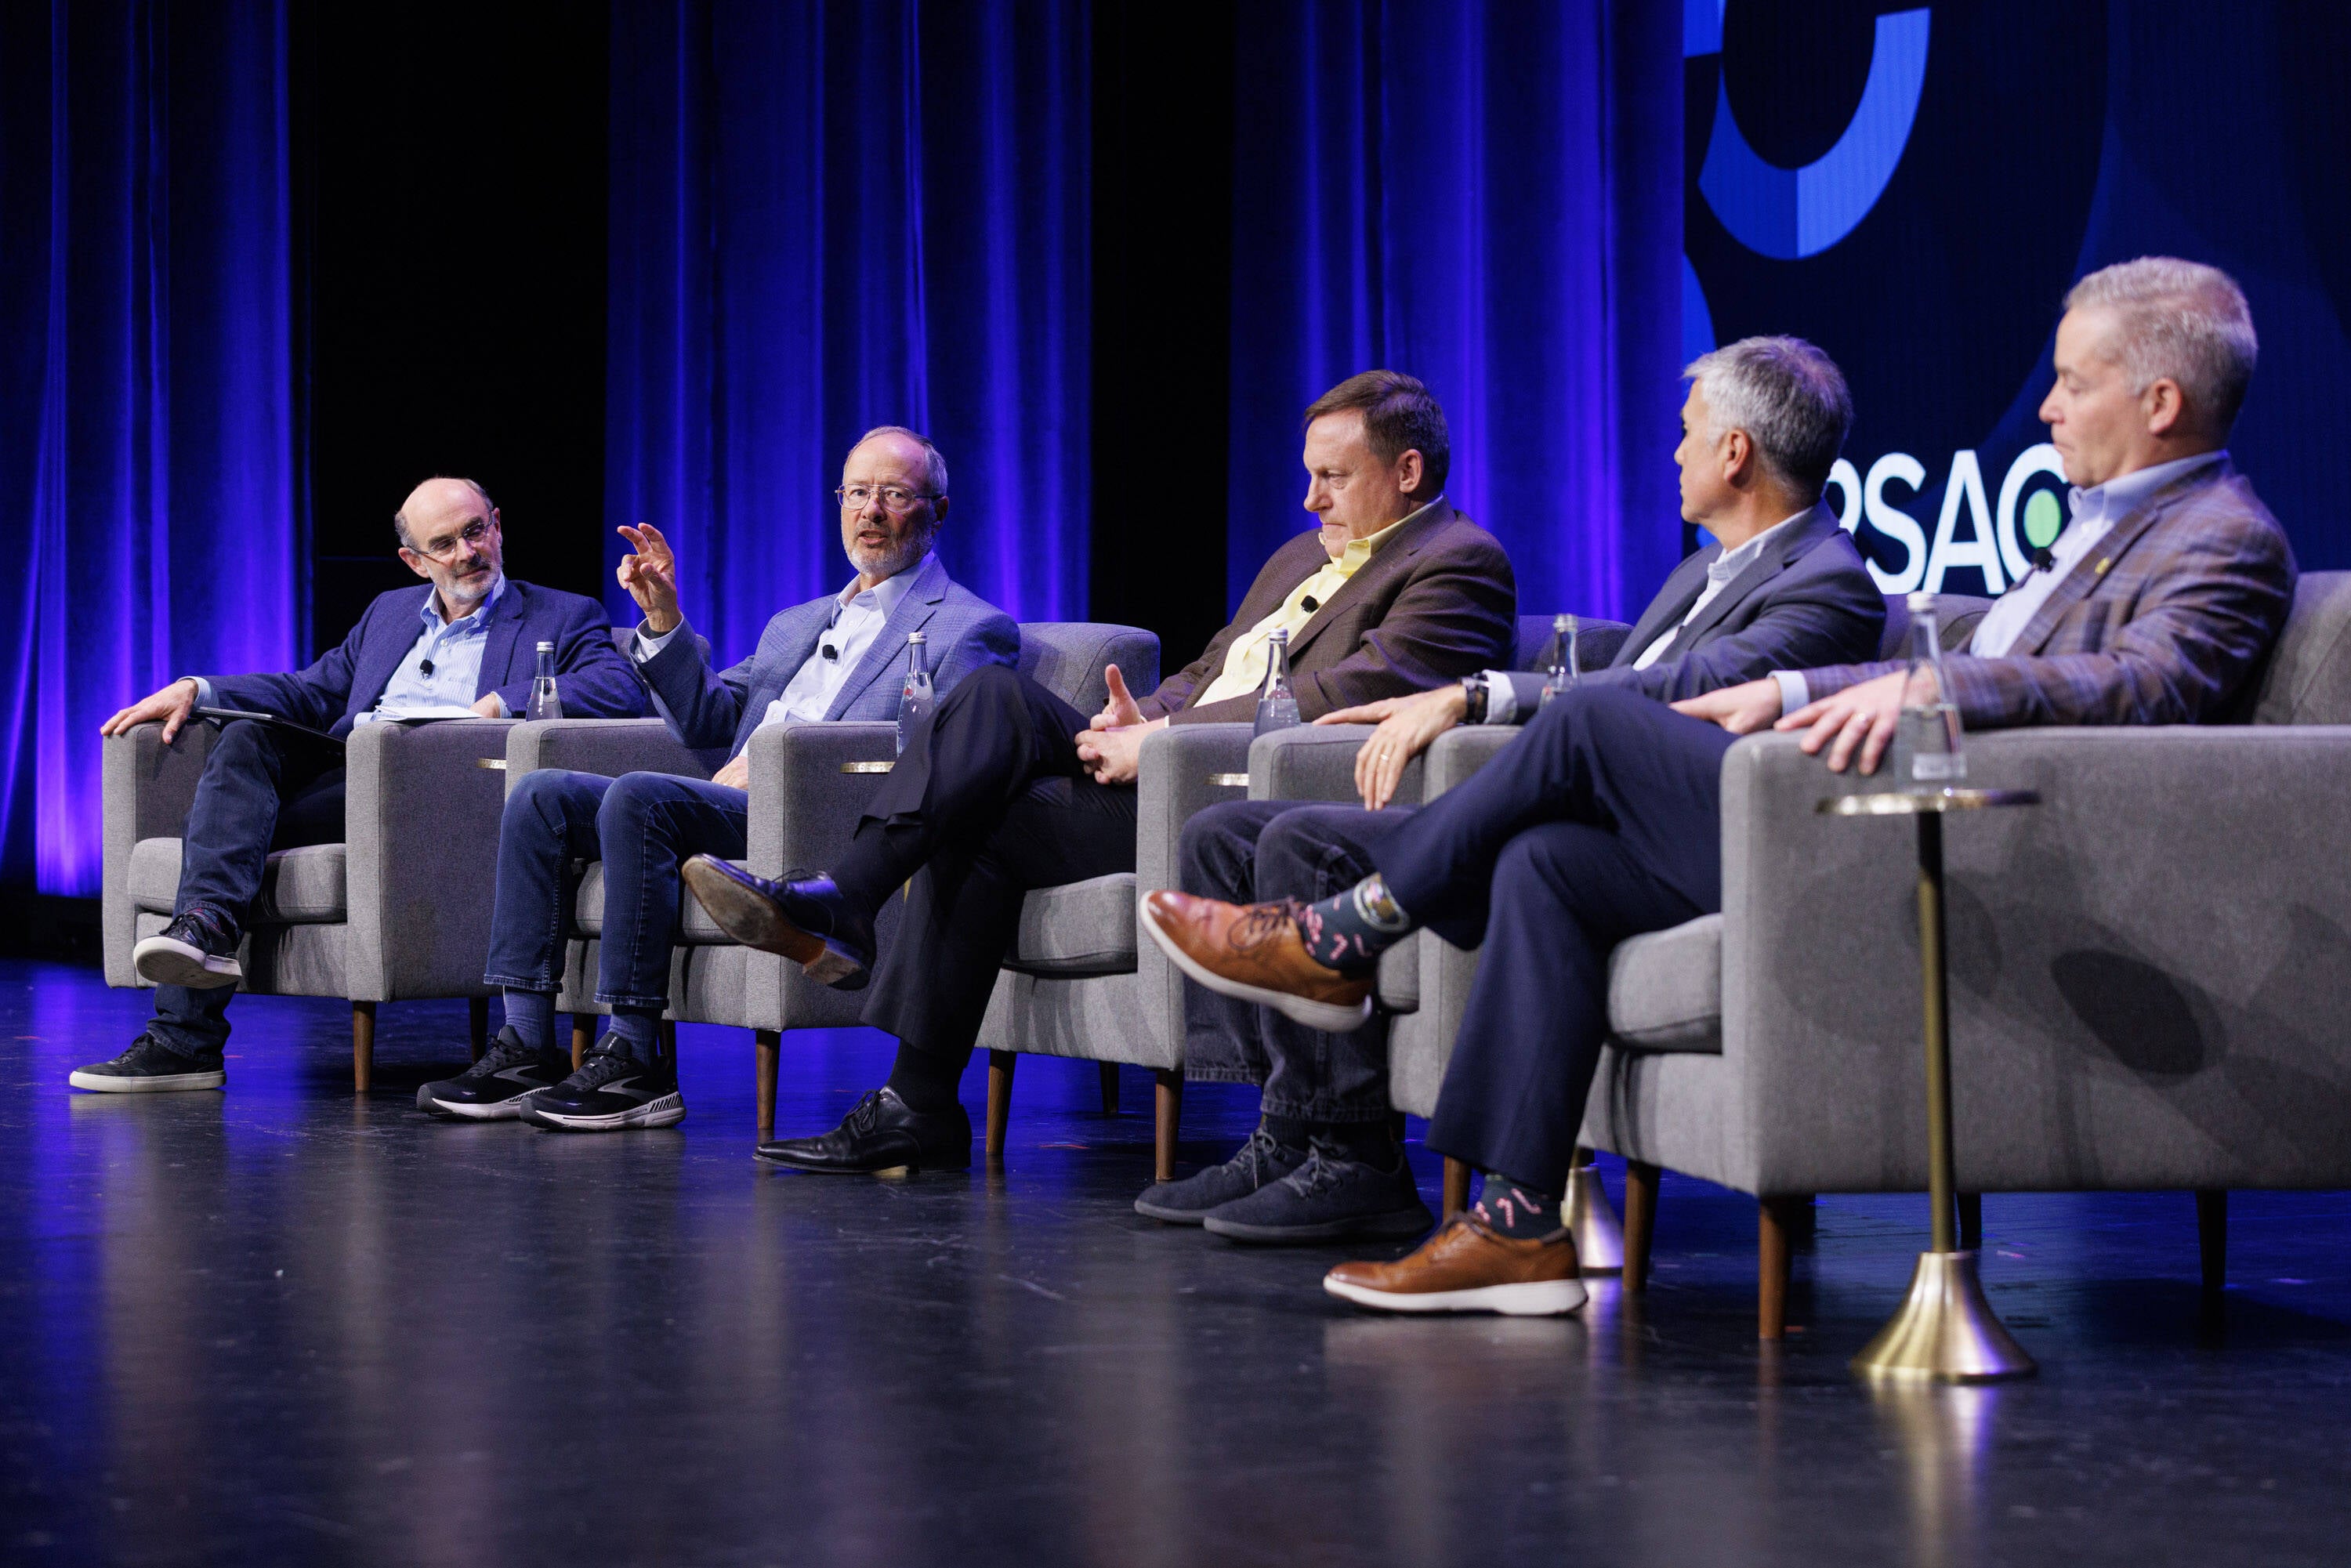
At the RSAC 2026 Conference, four former NSA directors discussed the shifting landscape of cybersecurity, emphasizing the growing threats from state actors and cybercriminals. They expressed concerns about the U.S. becoming 'numb' to cyber threats, with retired General Paul Nakasone noting that the scale of cyber intrusions has become overwhelming. The panel highlighted the lack of a cohesive federal data privacy framework and the political divisions hindering effective cybersecurity legislation. Former NSA Director Mike Rogers pointed out that without a significant traumatic event, the public's perception of cyber threats remains muted. The discussions also touched on the necessity for offensive cyber capabilities and the importance of public-private collaboration in addressing these challenges. The former officials warned that adversaries like China are advancing rapidly, particularly in artificial intelligence, which could exacerbate cybersecurity risks. They called for a reevaluation of the criteria for responding to cyberattacks, stressing that the determination of a 'red line' for kinetic responses ultimately lies with the President.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Salt Typhoon, Stuxnet and Sony Pictures in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Dutch Intelligence Warns of Chinese Malware Targeting Edge Devices Dutch intelligence agencies have reported a surge in Chinese cyberattacks targeting edge devices such as routers and firewalls. A newly discovered malware can survive firmware updates and has compromised 20,000 network appliances globally. The Military Intelligence and Security Service (MIVD) and the General…
 CISA's CI Fortify Initiative Enhances Resilience for Critical Infrastructure The CI Fortify initiative, launched by CISA and international partners, aims to ensure critical infrastructure can maintain essential services during cyber attacks. This initiative comes in response to recent attacks on U.S. water systems attributed to Iranian hackers, which highlighted vulnerabilities in operational…