 www.sh.consulting
Hazy Hawk Campaign Hijacks Subdomains at 34 US Universities
Article Content

- •34 major US universities had subdomains hijacked by the Hazy Hawk threat actor.
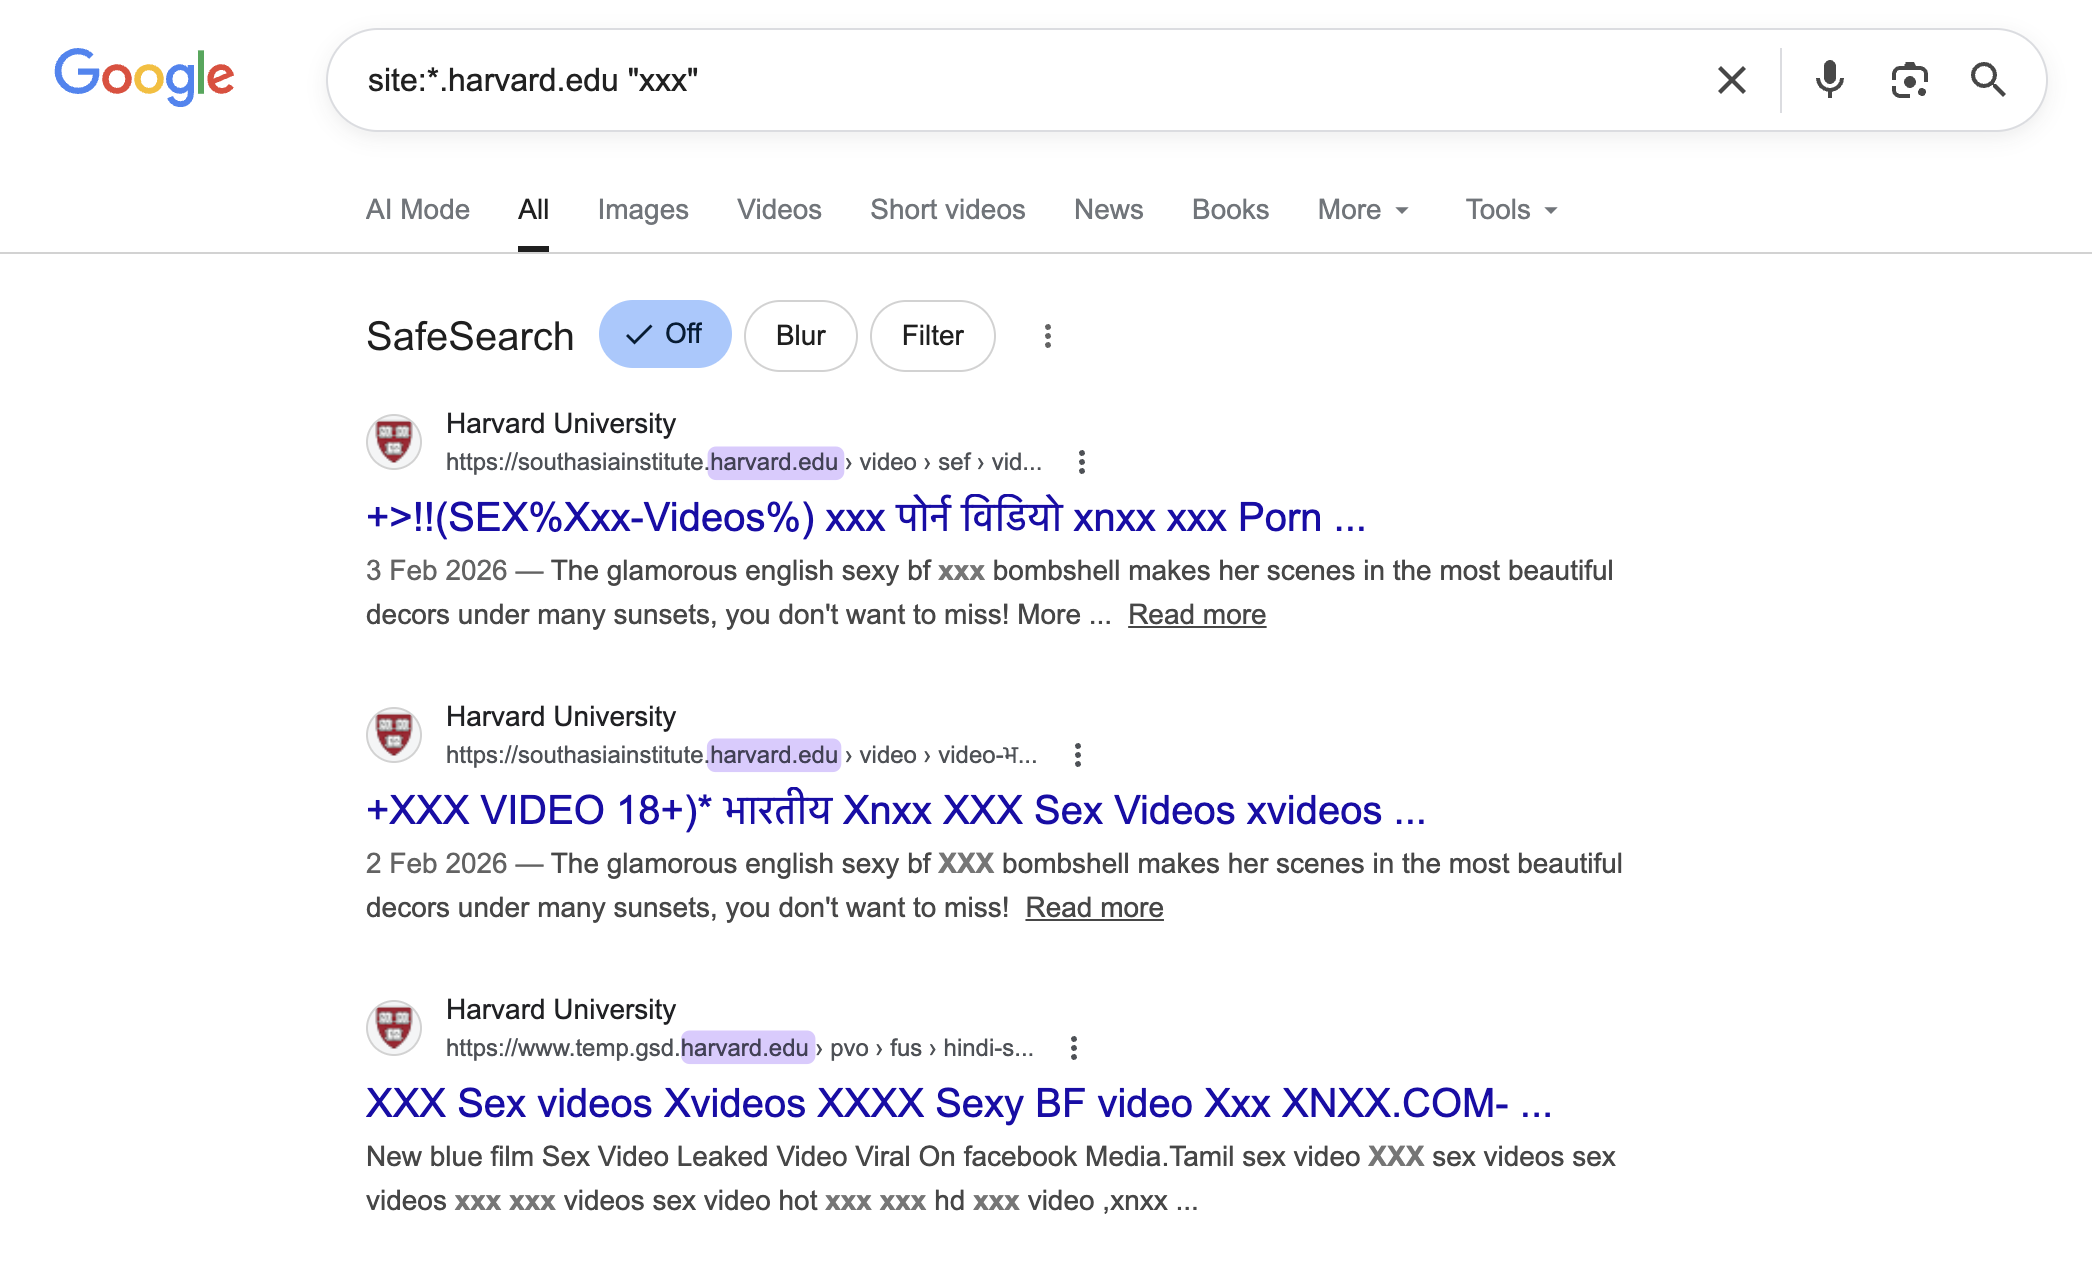
- •Attackers served explicit content through abandoned CNAME records, indexed by Google.
- •The incident reveals significant vulnerabilities in university IT management practices.
In early April 2026, a coordinated subdomain takeover campaign was discovered, affecting 34 major US universities, including MIT, Harvard, and Stanford. The attackers, identified as Hazy Hawk, exploited abandoned CNAME records to hijack subdomains and serve explicit pornographic spam that was indexed by Google. The attack method involves registering accounts on external platforms that match orphaned subdomains, allowing full control over the content served. This incident highlights a significant security gap in university IT practices, as many institutions fail to maintain a comprehensive inventory of their DNS records. The campaign's impact is extensive, potentially affecting many more universities given the number of abandoned subdomains across the .edu domain space. The Department of Defense Education Activity was also flagged as having a vulnerable domain. The situation remains critical as affected institutions work to regain control of their subdomains.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Hazy Hawk and Antioch University in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…