 Technadu
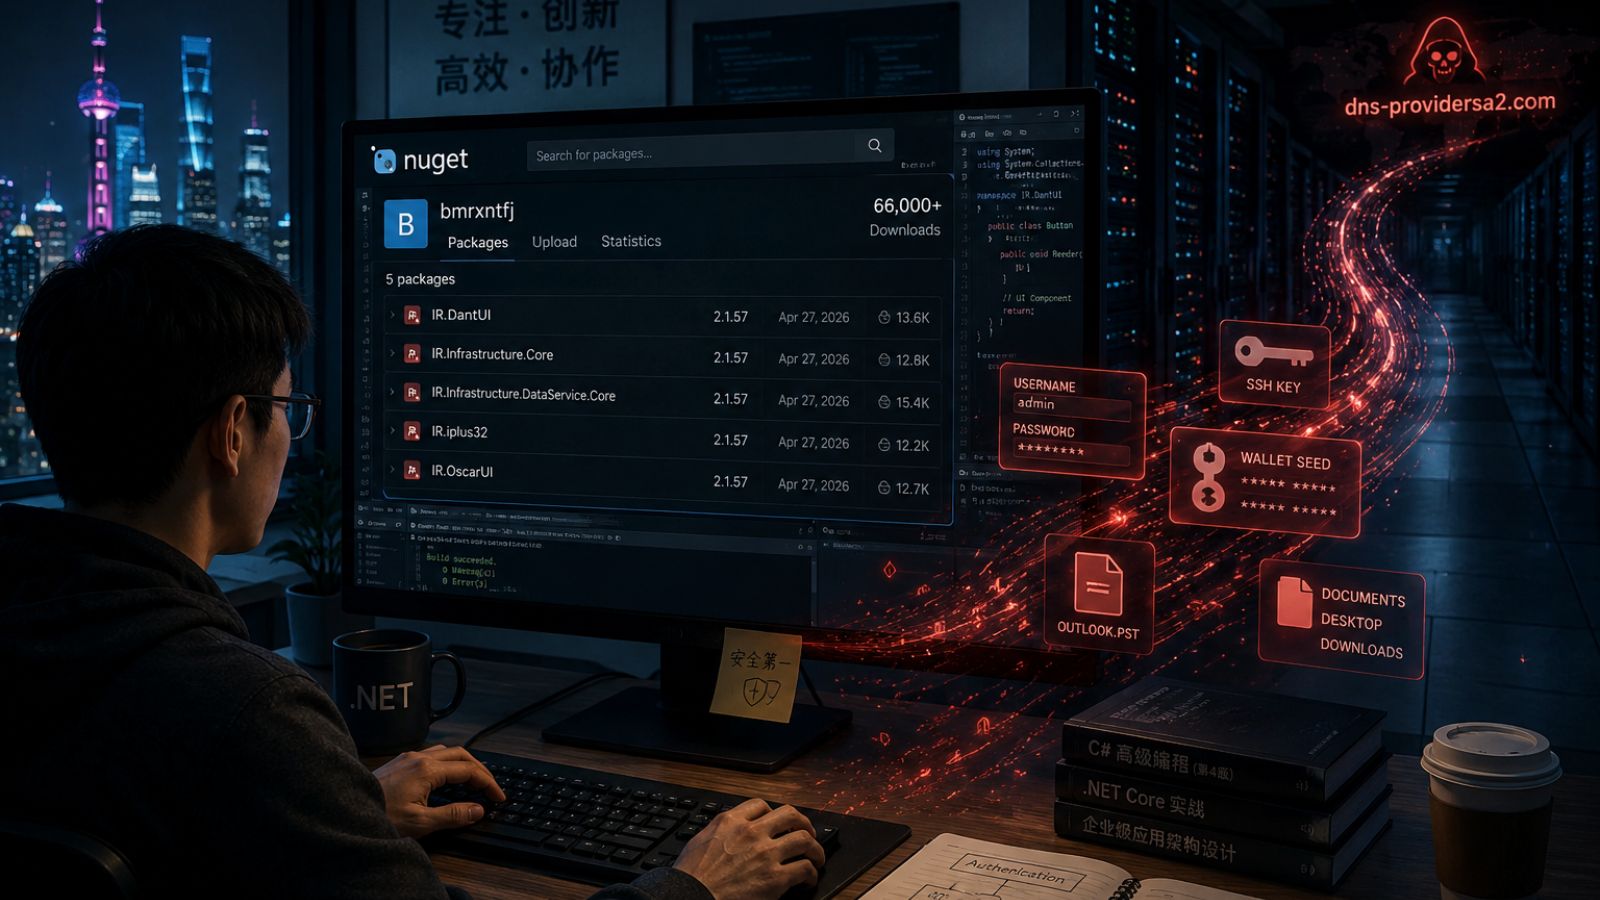
Malicious NuGet Packages Target Chinese Developers, Steal Sensitive Data
Article Content

- •Five malicious NuGet packages impersonate legitimate libraries targeting Chinese developers.
- •The infostealer collects sensitive data, including browser credentials and crypto wallet information.
- •Cybersecurity teams are urged to implement detection measures and rotate credentials immediately.
Five malicious NuGet packages were discovered targeting developers in the Chinese .NET ecosystem. The packages, published under the account bmrxntfj, impersonate legitimate libraries and have accumulated around 65,000 downloads. They deploy a sophisticated infostealer that targets browser credentials, SSH keys, and cryptocurrency wallets. The attack leverages extensive version manipulation to evade detection, with 219 out of 224 versions marked as 'listed: false'. The primary command-and-control domain for the stolen data is dns-providersa2.com, registered on March 12, 2026. Cybersecurity researchers have submitted takedown requests to NuGet's security team, but the packages remain active as of the latest reports. Developers are advised to use legitimate libraries and rotate credentials from potentially compromised systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Critical SQL Injection Zero-Day in Arista VeloCloud Orchestrator Exploited Arista Networks has patched a critical zero-day vulnerability (CVE-2026-114625) in its VeloCloud Orchestrator (VCO) that is actively being exploited. The flaw allows authenticated users, even those with basic privileges, to escalate their access to superuser status via a low-complexity SQL injection attack. This…