 www.nato.int
NATO Enhances Baltic Security Amid Rising Sabotage Threats
Article Content

- •NATO launched 'Baltic Sentry' to enhance military presence in the Baltic Sea.
- •Recent sabotage incidents have targeted undersea cables, raising security concerns.
- •The initiative includes deploying naval drones and integrating national surveillance assets.
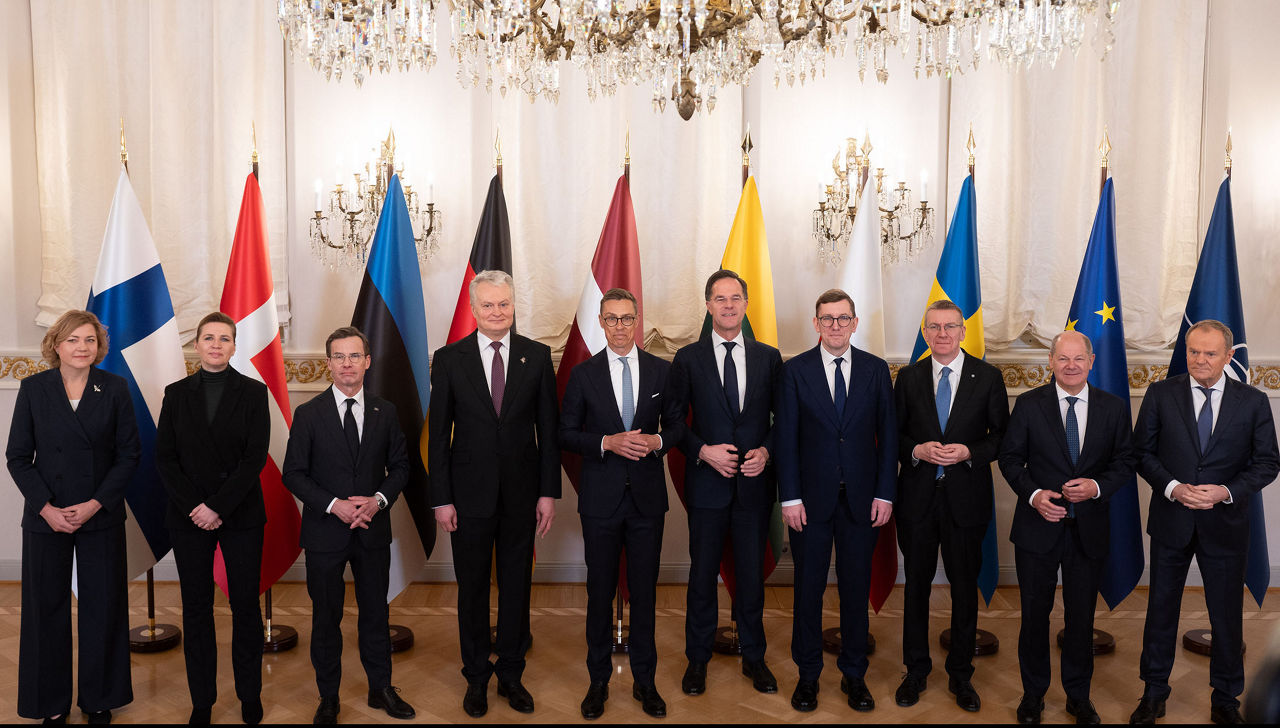
NATO has launched 'Baltic Sentry' to bolster military presence in the Baltic Sea following recent sabotage incidents targeting critical undersea infrastructure, including energy and communication cables. The initiative was announced by NATO Secretary General Mark Rutte during a summit with Baltic Sea Allies on January 14, 2025. This comes after damage to cables connecting Estonia and Finland on December 25, 2024, which is being investigated as possible sabotage. The new military activity will utilize frigates, maritime patrol aircraft, and naval drones to enhance protection and response capabilities. NATO aims to integrate national surveillance assets and work with industry to improve resilience against future threats. Rutte emphasized the need for robust enforcement measures, including potential legal actions against threats to infrastructure. The initiative reflects growing concerns over the security of critical infrastructure in the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…