 Technadu
Ransomware Evolution: Encryptionless Extortion and EDR Bypass Tactics Rise
Article Content

- •Ransomware incidents decreased globally, but threats remain sophisticated and entrenched.
- •Attackers are increasingly using EDR killers and BYOVD techniques to disable security tools.
- •ShinyHunters and other groups are moving towards encryptionless extortion, focusing on data theft.
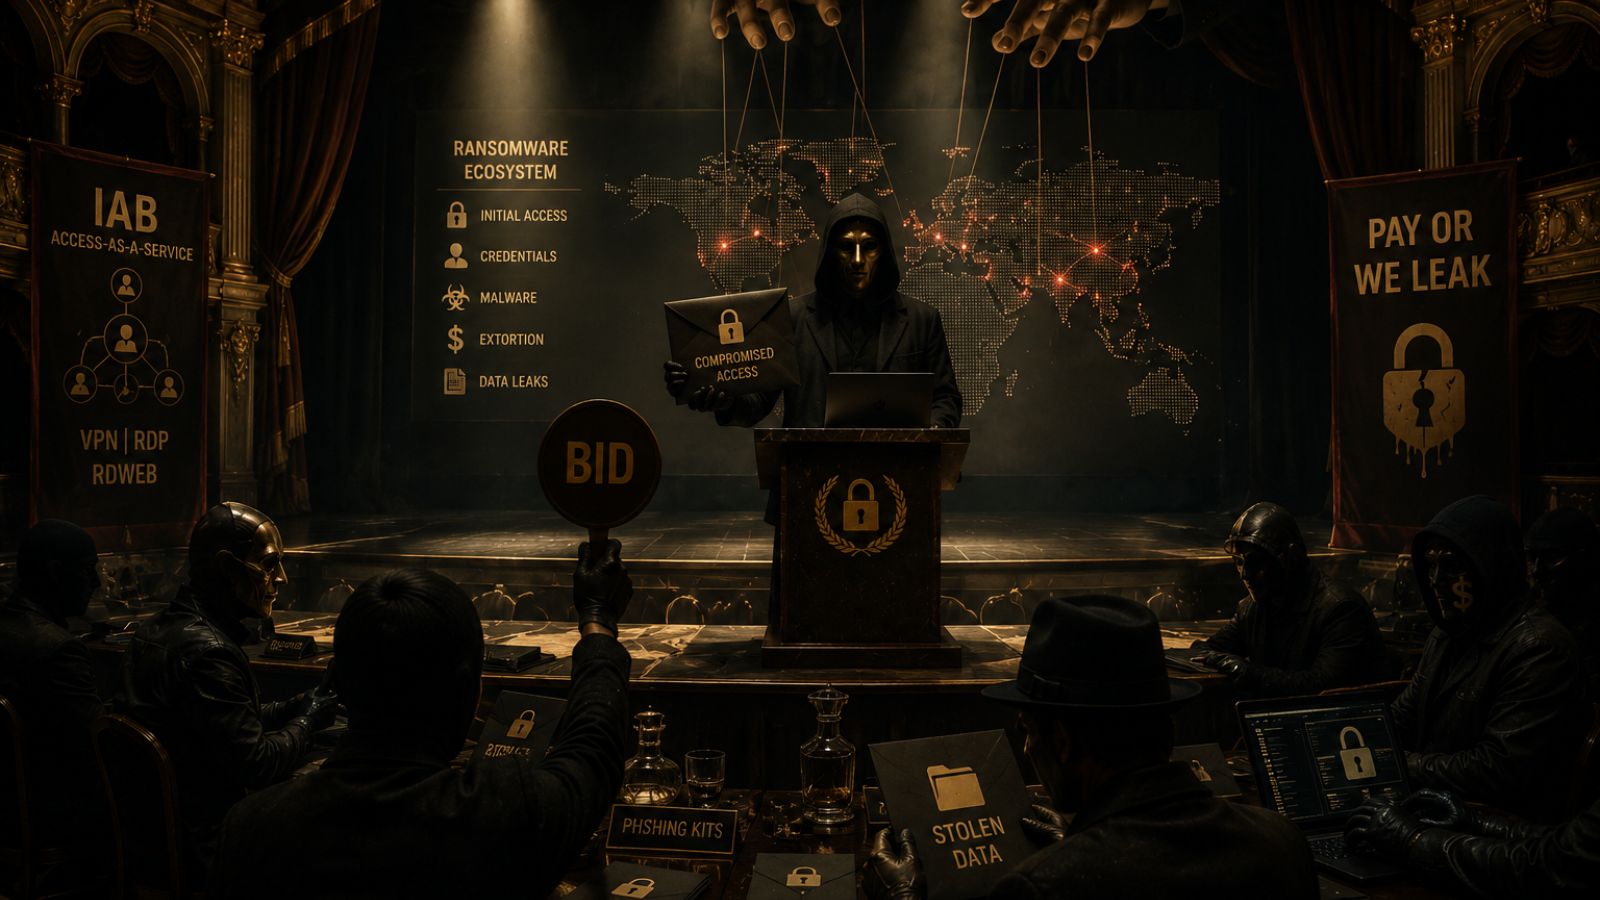
Kaspersky's 2026 report indicates a decline in ransomware incidents, yet the threat remains significant. Attackers are increasingly using EDR killers and BYOVD techniques to bypass security measures. The PE32 ransomware family employs post-quantum cryptography, specifically the ML-KEM standard, to secure its operations. With global ransom payments dropping to 28% in 2025, groups like ShinyHunters are shifting to encryptionless extortion, focusing on data theft and public leaks. The industrialization of ransomware attacks is supported by initial access brokers exploiting RDP and VPN vulnerabilities. Qilin emerged as the most active ransomware group, alongside Cl0p and Akira. Law enforcement has responded with takedowns of major dark web platforms, including RAMP and LeakBase, to disrupt these operations. The overall landscape shows a shift towards more sophisticated and varied attack methodologies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Akira, VX Crypt and Die Linke in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Chinese Smishing Gang Targets Ireland and Four Other EU Countries Ireland is identified as one of five EU countries targeted by the Chinese text-scam group known as Smishing Triad, as reported by the EU cyber security agency Enisa. This group conducts large-scale smishing operations, which involve sending fraudulent text messages that impersonate legitimate organizations to steal…
 Attackers Exploit MFA Gaps in SonicWall VPN Access On August 4, 2026, an Akira ransomware affiliate successfully accessed a SonicWall SSL VPN by spraying passwords, exploiting the lack of multi-factor authentication (MFA). After gaining access, the attacker used RDP to reach the domain controller and enumerate Active Directory, although the ransomware deployment…