 Heise.De
Raspberry Pi OS 6.2 Enhances Security by Disabling Passwordless Sudo
Article Content

- •Raspberry Pi OS 6.2 disables passwordless sudo by default to enhance security.
- •Existing installations will not automatically switch to the new security setting.
- •Users can revert to passwordless sudo if they prefer, but this poses a security risk.
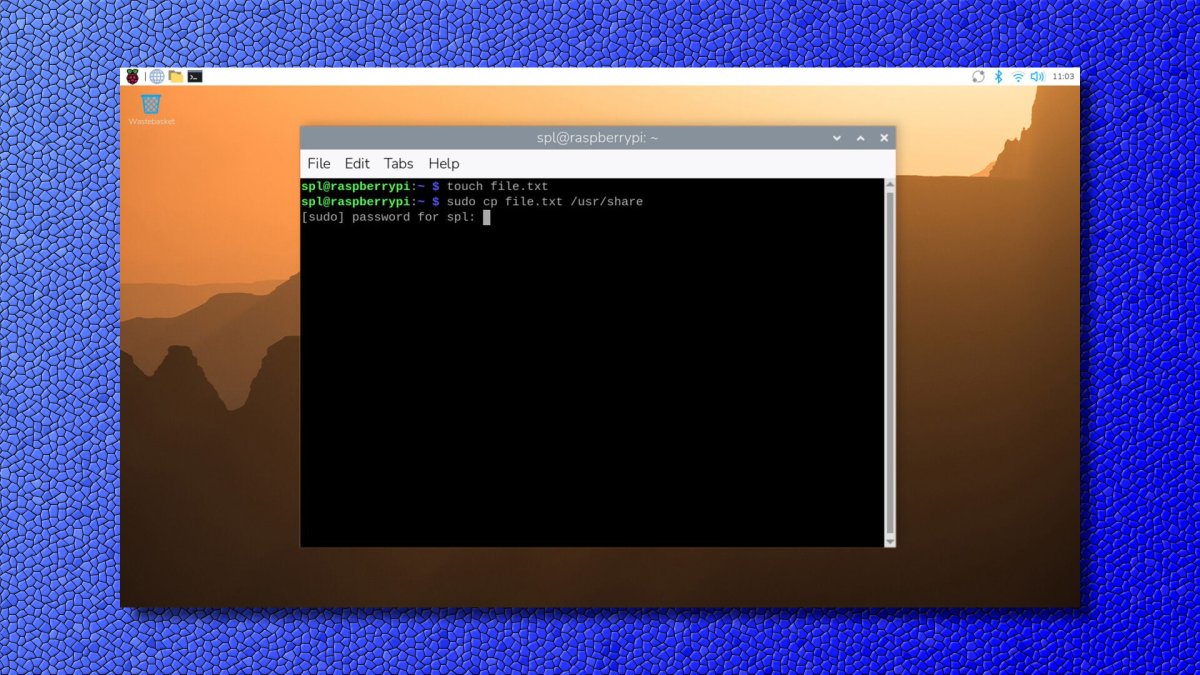
On April 15, 2026, the Raspberry Pi project released Raspberry Pi OS 6.2, which includes a significant security enhancement by disabling passwordless sudo by default for new installations. This change aims to improve security against potential attacks, as the previous configuration allowed regular users and potential intruders to execute administrative tasks without entering a password. Users can still revert to the previous setting if desired, but existing installations will not automatically adopt this change. The update also includes various small changes and bug fixes, but the main focus is on enhancing the operating system's security posture. The developers acknowledge the challenge of balancing security improvements with user convenience. The update is based on Debian Trixie, marking the second update since the transition to this version. The maintainers encourage users to be proactive in securing their systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…