 Kahawatungu
Romanian Hospitals Forced to Use Paper After Major Cyberattack
Article Content

- •Over 100 Romanian hospitals disconnected from the internet to mitigate a ransomware attack.
- •The ransomware, BackMyData, scrambled files and demanded €160,000 in bitcoin as ransom.
- •Medical staff adapted by using manual processes, demonstrating resilience in crisis management.
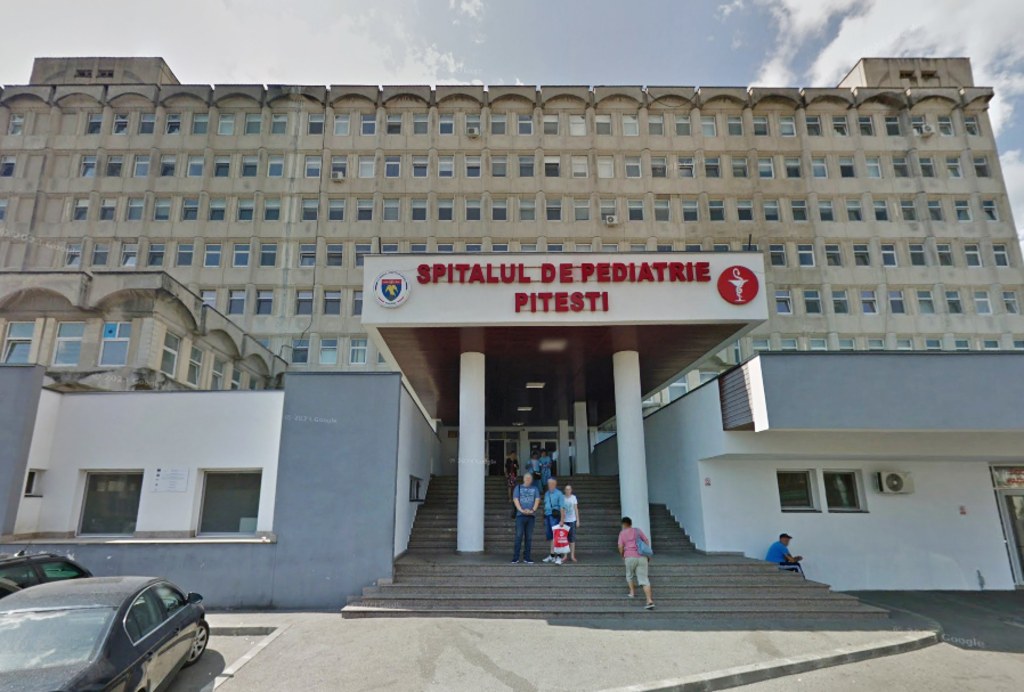
In February 2024, over 100 hospitals in Romania were targeted by a significant cyberattack that exploited vulnerabilities in the Hippocrates medical software, deploying ransomware known as BackMyData. The attack forced the national cyber-security centre to disconnect hospitals from the internet to prevent further spread, impacting patient care and operations. Medical staff reverted to pen and paper for patient records and care processes, creating temporary offline systems to continue treatment. The ransomware demanded a ransom of €160,000 in bitcoin, which the Romanian government refused to pay. This incident has been recognized as one of the largest cyberattacks on healthcare systems globally, prompting discussions on disaster response strategies. Cyber investigators identified that 26 hospitals were infected, highlighting the vulnerability of healthcare infrastructure to cyber threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Backmydata and Ascension in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in F5 BIG-IP APM Exploited for Remote Code Execution F5 Networks has reported a critical vulnerability in its BIG-IP Access Policy Manager (APM), tracked as CVE-2026-94127, which is being actively exploited in the wild. The flaw allows unauthenticated attackers to execute remote code on systems configured with both an APM access policy and an OAuth profile. This…
 Massive Network of AI Proxy Servers Used for Malicious Activities Uncovered Security researchers from Team Cymru have identified over 10,000 proxy servers in China facilitating malicious AI activities. These servers, termed 'transfer stations,' are primarily used to bypass geographic restrictions and conduct model distillation attacks against frontier AI models. The infrastructure allows…