 Defensedaily
Space Force Contracts $3.2 Billion for Space-Based Interceptors
Article Content

- •The Space Force has awarded $3.2 billion in contracts for space-based interceptors.
- •Twelve companies, including Lockheed Martin and SpaceX, are involved in the Golden Dome initiative.
- •The program aims to develop missile defense capabilities by 2028 to counter advanced aerial threats.
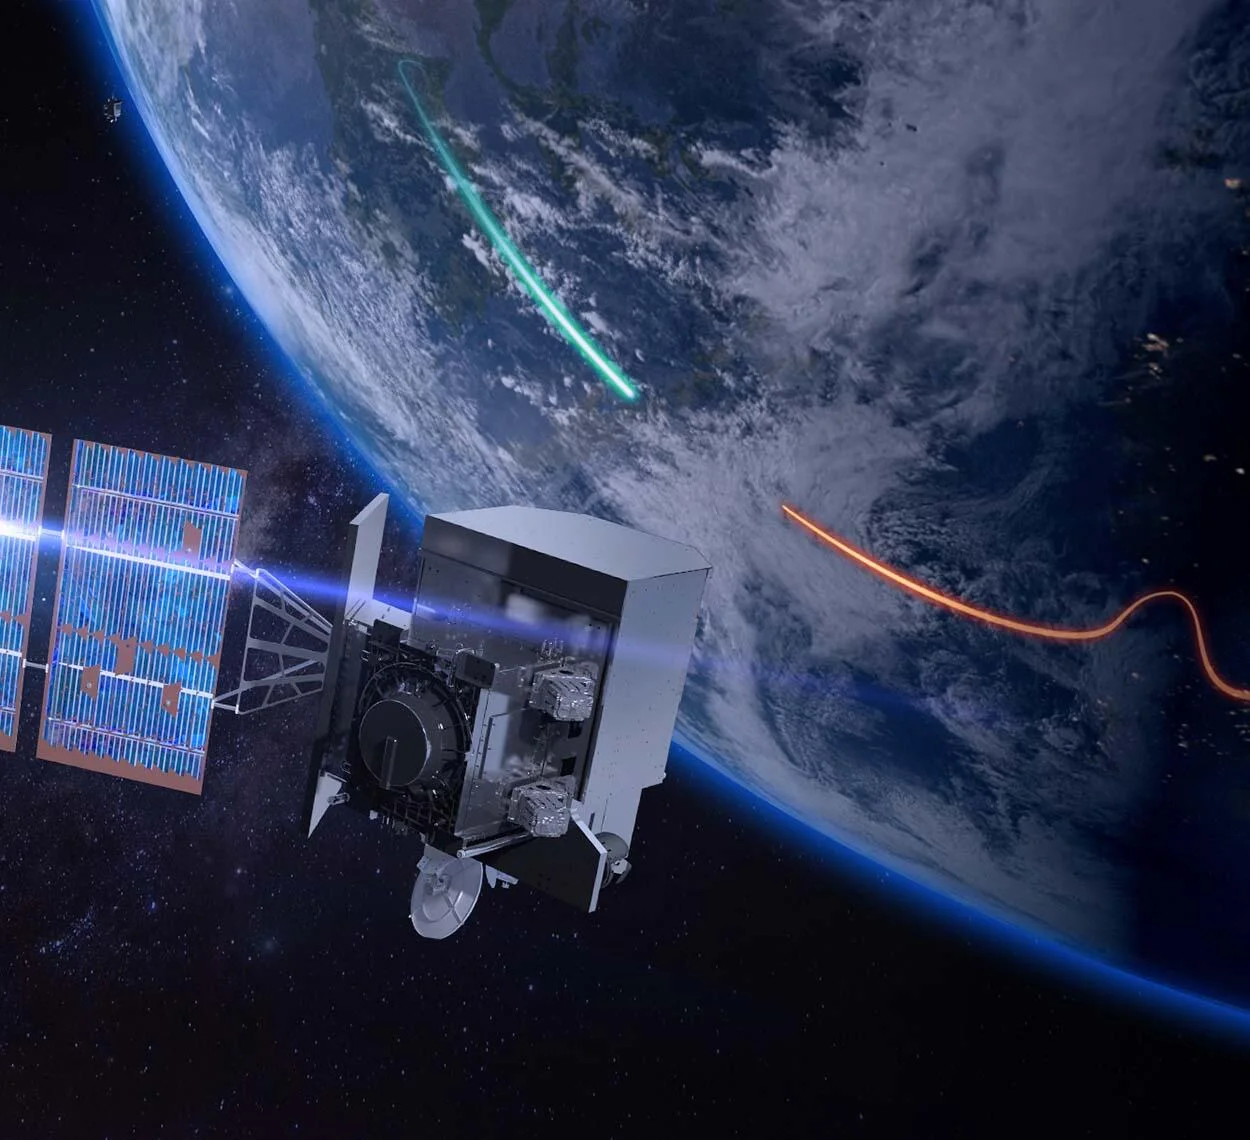
The U.S. Space Force has awarded contracts totaling up to $3.2 billion to 12 companies for the development of space-based interceptor (SBI) prototypes as part of the Golden Dome initiative. This program aims to create a missile defense architecture capable of countering various aerial threats, including ballistic and hypersonic missiles. The contracts were awarded under Other Transaction Authority (OTA) agreements, which provide flexibility in contracting. Companies involved include major defense contractors such as Lockheed Martin, Northrop Grumman, and SpaceX. The Golden Dome program is projected to cost $185 billion, with initial capabilities expected by 2028. The Pentagon is seeking $17.5 billion in fiscal 2027 for this initiative. The development of SBIs has become feasible due to advancements in technology and reduced launch costs. However, experts warn of significant technical challenges ahead. The program is a response to rapidly advancing adversary missile capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Lockheed Martin in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 New Task Force Established for Cyber Defense of Golden Dome Initiative US Northern Command has established Joint Task Force-Gold (JTF-Gold) to coordinate cyber defense for the Golden Dome initiative. Col. Kevin Stonerook announced that the task force's new mission focuses on defending against cyberattacks targeting the homeland missile defense architecture. The task force, which consists…
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…