 Vietnam.Vn
Student Malware Ring Infects 94,000 PCs, Generates Billions in Illicit Gains
Article Content

- •A student-led malware ring infected over 94,000 computers worldwide.
- •The malware was designed to steal sensitive browser data and bypass security protections.
- •Authorities have charged 12 individuals involved in the operation with serious cybercrime offenses.
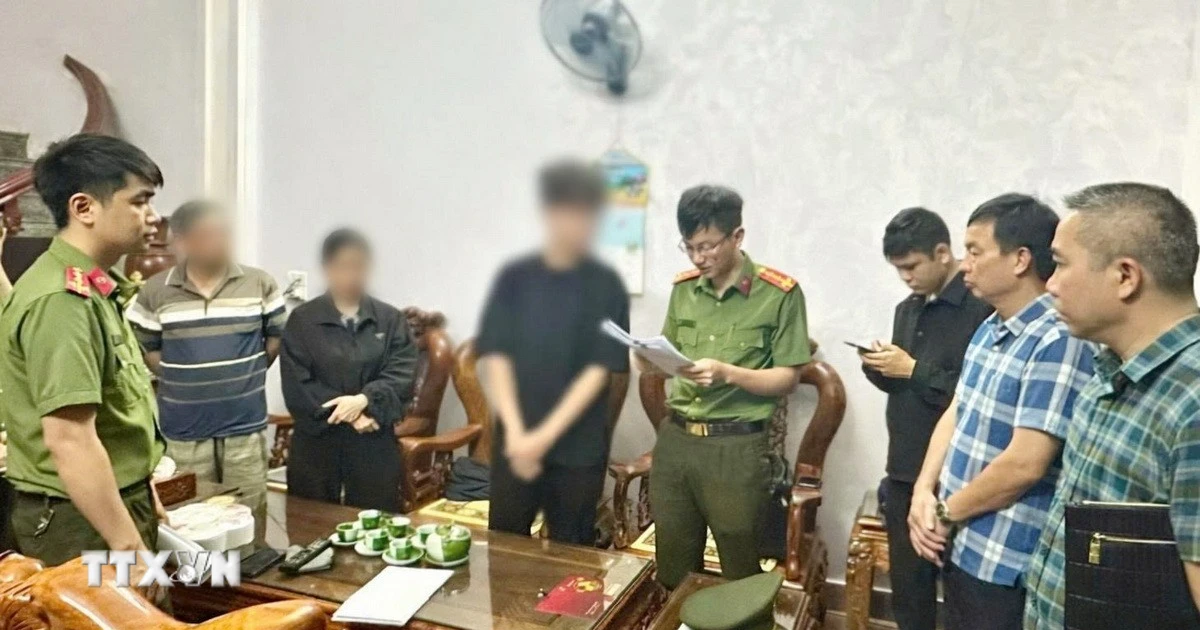
On March 25, 2026, Vietnamese authorities reported the dismantling of a malware distribution network led by high school students, which infected over 94,000 computers globally. The primary suspect, identified as N.V.X., began programming in 2023 and developed malware capable of extracting sensitive data from web browsers. The malware, known as 'PXA Stealers,' was designed to steal login cookies and passwords, which were then sold for profit. The group operated through Telegram channels to manage and exploit the stolen data. Authorities estimate that the operation generated tens of billions of Vietnamese dong in illegal revenue. Twelve suspects have been charged with producing and distributing malicious software. The malware was continuously refined to evade detection, indicating a sophisticated operation. The investigation highlights the growing trend of cybercrime involving younger individuals leveraging programming skills for illicit activities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Adonis in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…