 Straitstimes
Taiwan Activates Backup Communications After Undersea Cable Breaks
Article Content

- •Taiwan activated backup communications for Dongyin after an undersea cable break.
- •The cable was damaged by shifting wreckage, likely due to poor weather conditions.
- •Repairs to the cable are expected to be completed by the end of July 2026.
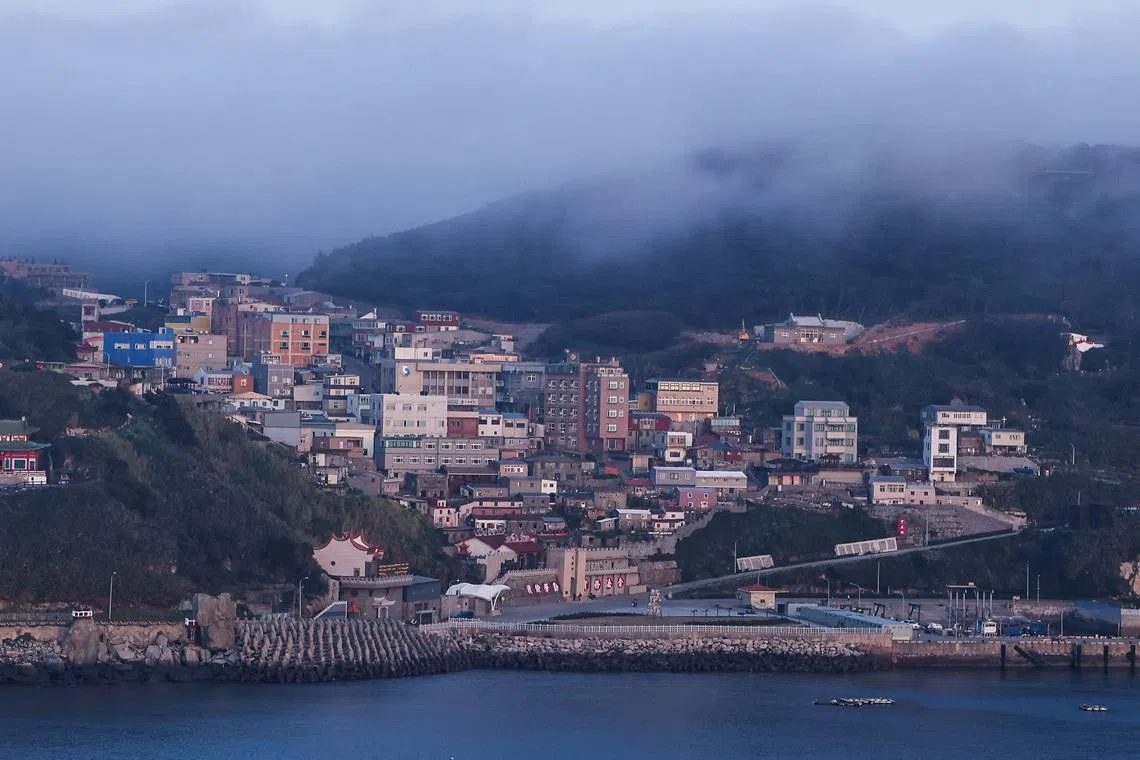
Taiwan has activated backup communications for Dongyin, its northernmost territory, after an undersea cable linking the island to Beigan in the Matsu Islands broke due to shifting ship wreckage, likely caused by poor weather conditions. The incident has raised concerns about the vulnerability of undersea communication cables, which have previously been attributed to damage from Chinese vessels. Dongyin, home to approximately 1,500 residents and a significant military presence, relies on this cable for internet and voice communications. The Ministry of Digital Affairs reported that a microwave communication backup system is now operational, ensuring mobile phone and internet services are functioning normally, although cable television services are down and some internet services may face delays. Repairs by Chunghwa Telecom are expected to be completed by the end of July, contingent on weather conditions. This incident follows previous disruptions in 2023, where undersea cables were also cut, with Taiwan attributing the damage to Chinese ships without evidence of deliberate tampering. Taiwan continues to enhance its communication resilience, including trials for low-Earth-orbit satellite systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…