 Theguardian
Taiwan President Cancels Africa Trip Amid Chinese Pressure on Airspace Access
Article Content

- •Taiwan's President Lai Ching-te canceled a trip to Eswatini due to denied overflight rights.
- •China allegedly pressured Seychelles, Mauritius, and Madagascar to revoke flight permits.
- •This incident underscores China's increasing influence over Taiwan's diplomatic relations.
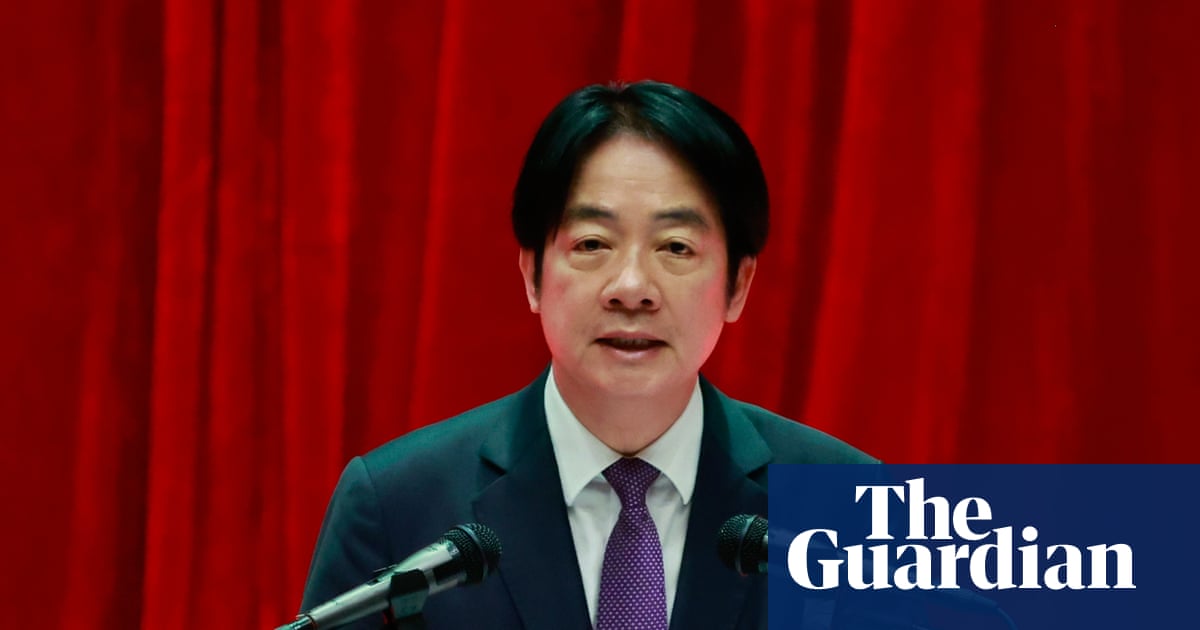
Taiwan's President Lai Ching-te was forced to cancel a planned trip to Eswatini after Seychelles, Mauritius, and Madagascar revoked overflight permissions for his aircraft. This unprecedented cancellation is attributed to alleged economic coercion from China, which claims Taiwan as its territory. Lai's office stated that the revocation of flight permits was due to intense pressure from Chinese authorities, including threats of economic sanctions. The incident highlights China's increasing influence over nations that have diplomatic ties with Taiwan, which now has only 12 allies remaining. Lai condemned China's actions as a threat to international order and reaffirmed Taiwan's commitment to engage globally despite such suppression. The situation reflects ongoing tensions between Taiwan and China, particularly under the leadership of Lai, who is viewed unfavorably by Beijing. The cancellation marks the first time a Taiwanese president has had to abandon a foreign trip due to Chinese pressure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (12)
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…