 Ifex
Turkey's Disinformation Law Faces Growing Criticism from Press Freedom Groups
Article Content

- •Turkey's disinformation law has led to the prosecution of 83 journalists since October 2022.
- •The law is criticized for its vague definitions, enabling arbitrary suppression of journalism.
- •Press freedom organizations are calling for the repeal of the disinformation law and release of imprisoned journalists.
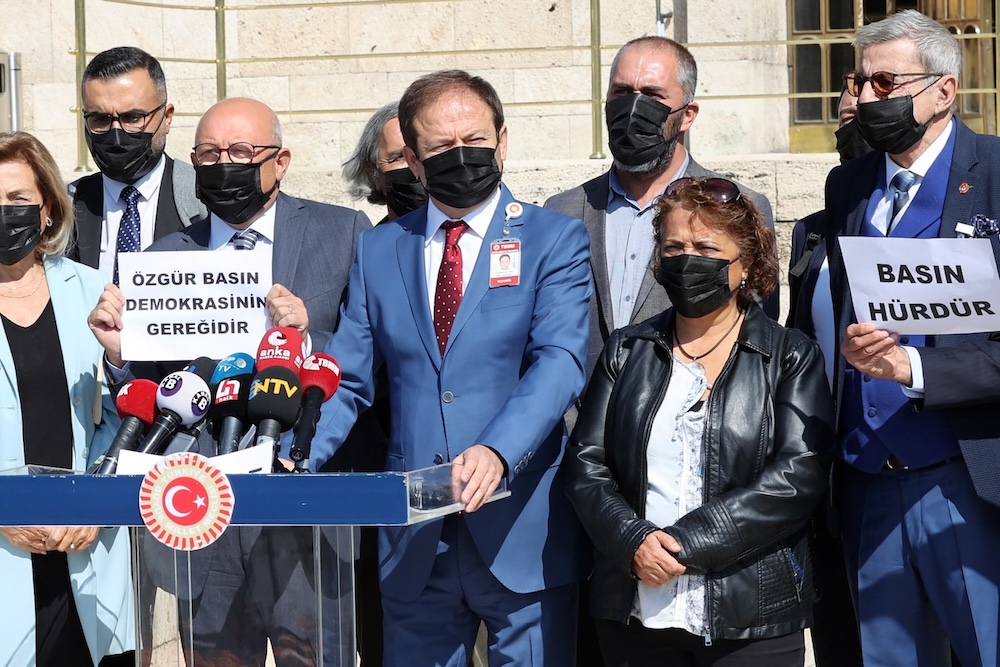
On April 28, 2026, twenty-five press and freedom of expression organizations condemned Turkey's 'disinformation law', which has led to the arrest and prosecution of at least 83 journalists since its enactment in October 2022. The law, formally known as Article 217/A of the Turkish Penal Code, is criticized for its vague definitions and broad application, allowing authorities to suppress legitimate journalism. Prominent journalists İsmail Arı and Alican Uludağ are among those frequently targeted, with both currently imprisoned. The organizations demand the immediate release of all journalists detained under this law and the complete repeal of Article 217/A. The situation reflects a broader trend of legal pressures on media freedom in Turkey, which is viewed as increasingly hostile to independent journalism. Recent reports indicate that the law's application has intensified, raising alarms about the state of press freedom in the country.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…