 Kyivpost
US Sanctions Easing Fails to Boost Russian Oil Exports Amid Drone Strikes
Article Content

- •Russia's oil exports declined despite a partial easing of US sanctions.
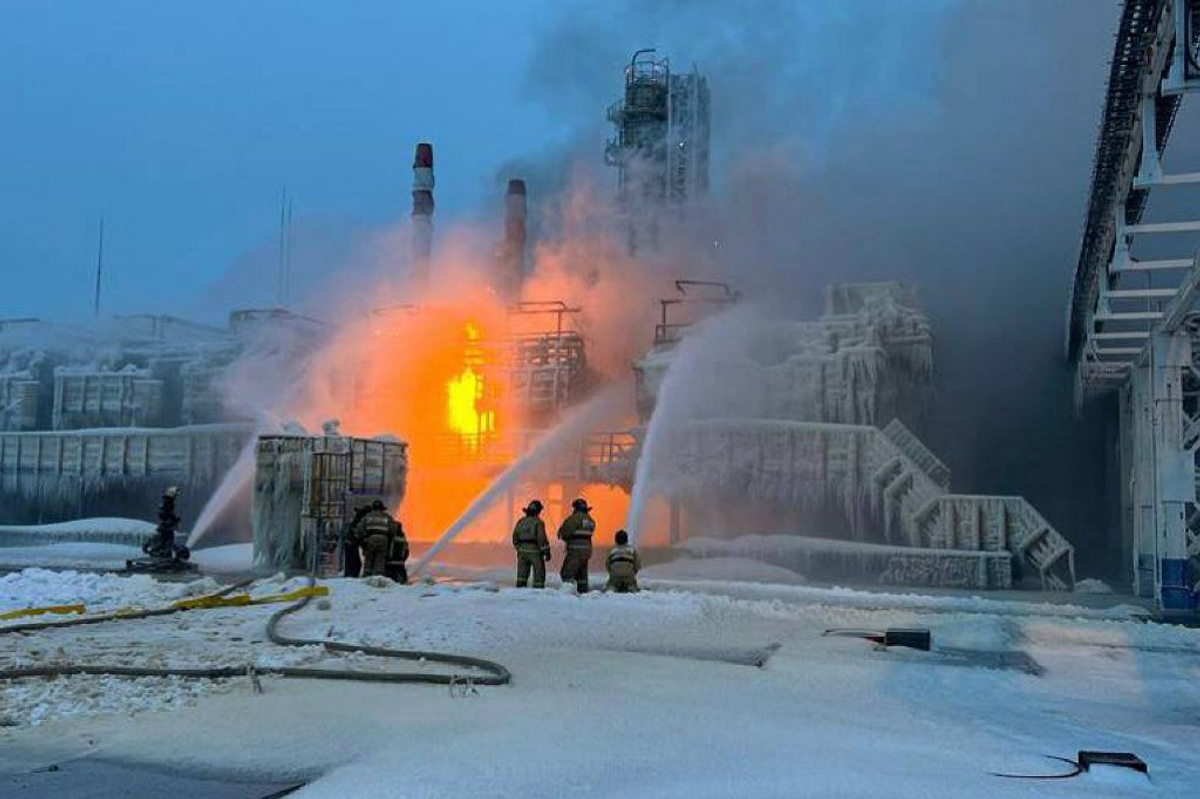
- •Drone strikes by Ukraine on Russian ports have severely impacted oil shipments.
- •A rare ceasefire was announced by both Russia and Ukraine for Orthodox Easter.
Despite a partial easing of US sanctions, Russia's oil export volumes did not increase in March 2026. Ukraine's Foreign Intelligence Service reported that logistical constraints and disruptions at key export infrastructure were significant factors in this decline. Oil shipments from Russian ports fell to 3.46 million barrels per day (bpd), down from 3.49 million bpd in February. Similarly, petroleum product exports decreased from 2.21 million bpd to 2.19 million bpd. Notably, the Primorsk port saw a sharp drop in exports from over 1.1 million bpd to approximately 732,000 bpd by the end of March. Concurrently, Ukraine conducted drone strikes on Russian oil infrastructure, costing Russia an estimated $970 million in oil revenues in a single week. The Kremlin announced a ceasefire for Orthodox Easter following Ukraine's call for a truce, marking a rare agreement between the two sides. The ongoing conflict and infrastructure disruptions continue to impact Russia's oil revenue significantly.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…