 Darkreading
Venom Stealer MaaS Platform Enables Automated Continuous Data Theft
Article Content

- •Venom Stealer automates credential theft and continuous data exfiltration.
- •The platform uses ClickFix social engineering to trick victims into executing malware.
- •It is sold on a subscription basis, indicating a thriving cybercriminal business model.
The newly identified Venom Stealer malware-as-a-service (MaaS) platform automates credential theft and continuous data exfiltration, posing a significant threat to users. Sold on cybercrime networks, it integrates ClickFix social engineering techniques to maintain ongoing access to stolen data. The platform operates on a subscription model, with prices ranging from $250 per month to $1,800 for lifetime access. Attackers can deploy the malware through fake web pages that trick victims into executing commands themselves, thereby bypassing detection systems. Once active, Venom Stealer continuously monitors for new credentials and extracts sensitive information, including cryptocurrency wallet data. The malware's capabilities extend to automated wallet cracking and fund transfers across blockchain networks. BlackFog researchers reported that the platform is actively maintained, with multiple updates released in March 2026. This development highlights the growing sophistication of cybercriminal tools available on the dark web.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
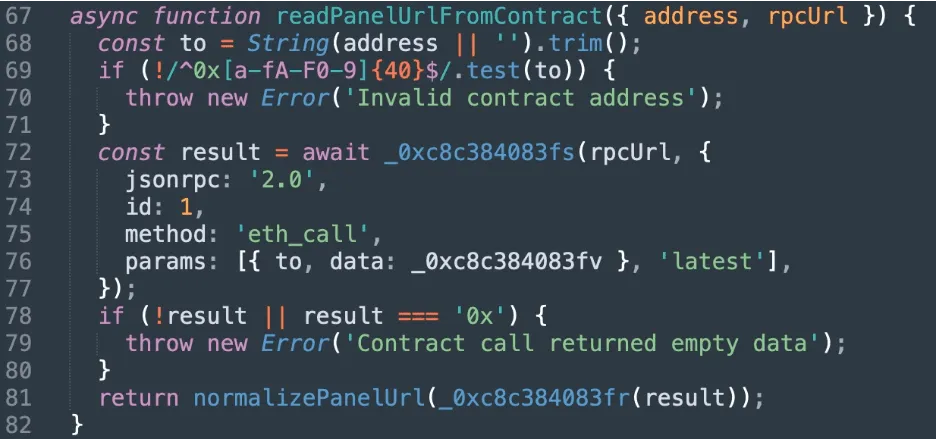 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…