 Foro3D
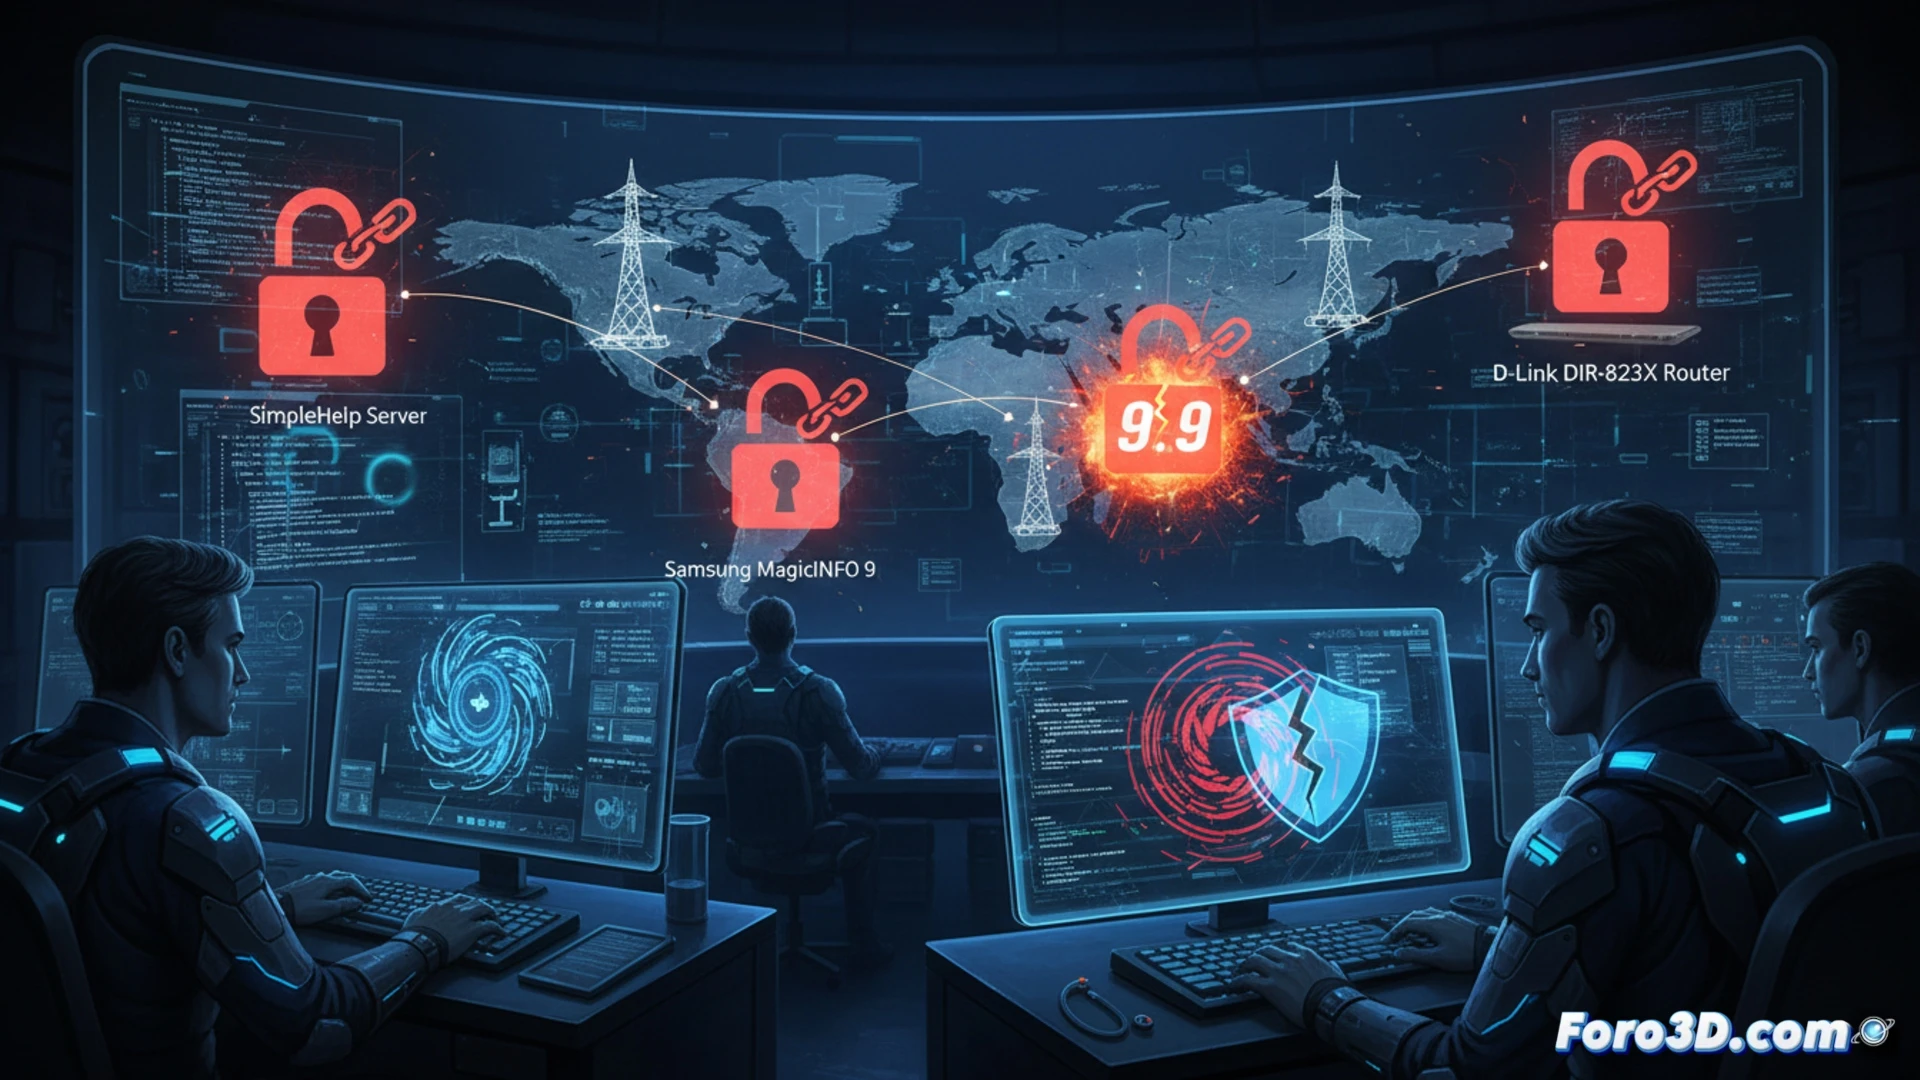
CISA Alerts on Critical Flaws in SimpleHelp, Samsung MagicINFO, and D-Link Devices
Article Content

- •CISA added four critical vulnerabilities to its KEV catalog on April 24, 2026.
- •CVE-2024-57726 in SimpleHelp allows privilege escalation, exploited by DragonForce ransomware.
- •Federal agencies must patch affected systems by May 8, 2026, to avoid exploitation.
On April 24, 2026, CISA added four actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog. The affected products include SimpleHelp remote management software, Samsung MagicINFO 9 Server, and D-Link DIR-823X routers. The most critical flaw, CVE-2024-57726, has a CVSS score of 9.9 and allows low-privileged users to escalate privileges to server admin without additional authentication. This vulnerability is being exploited by the DragonForce ransomware operation, which uses it to deploy ransomware across managed devices. Additionally, Samsung's MagicINFO has a command injection vulnerability, and D-Link routers are affected by a buffer overflow. CISA has mandated that federal agencies must patch or discontinue use of these products by May 8, 2026. Organizations using these systems are urged to take immediate action to mitigate risks associated with these vulnerabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track DragonForce, Mirai and Samsung in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Emerging EDR Killer Tool Targeting Ransomware Groups A new malicious tool, referred to as the EDR killer, is being actively used by at least eight ransomware groups, including Blacksuit and Medusa, to disable endpoint detection and response (EDR) solutions. This tool is believed to be an evolution of the EDRKillShifter developed by RansomHub, which allows ransomware…
 [DRAGONFORCE] Ransomware Attacks Target Community Property Management and Owen Leigh Optometry On September 16, 2026, the DRAGONFORCE ransomware group listed two organizations on a leak site: Community Property Management in the U.S. and Owen Leigh Optometry in the U.K. Community Property Management is reported to have over 200 GB of data claimed as stolen, while Owen Leigh Optometry's alleged data exfiltration…