Frequency
5
occurrences
First Seen
April 25, 2026
Last Seen
September 25, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
On April 24, 2026, CISA added four actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog. The affected products include SimpleHelp remote management software, Samsung MagicINFO 9 Server, and D-Link DIR-823X routers. The most critical flaw, CVE-2024-57726, has a CVSS score...
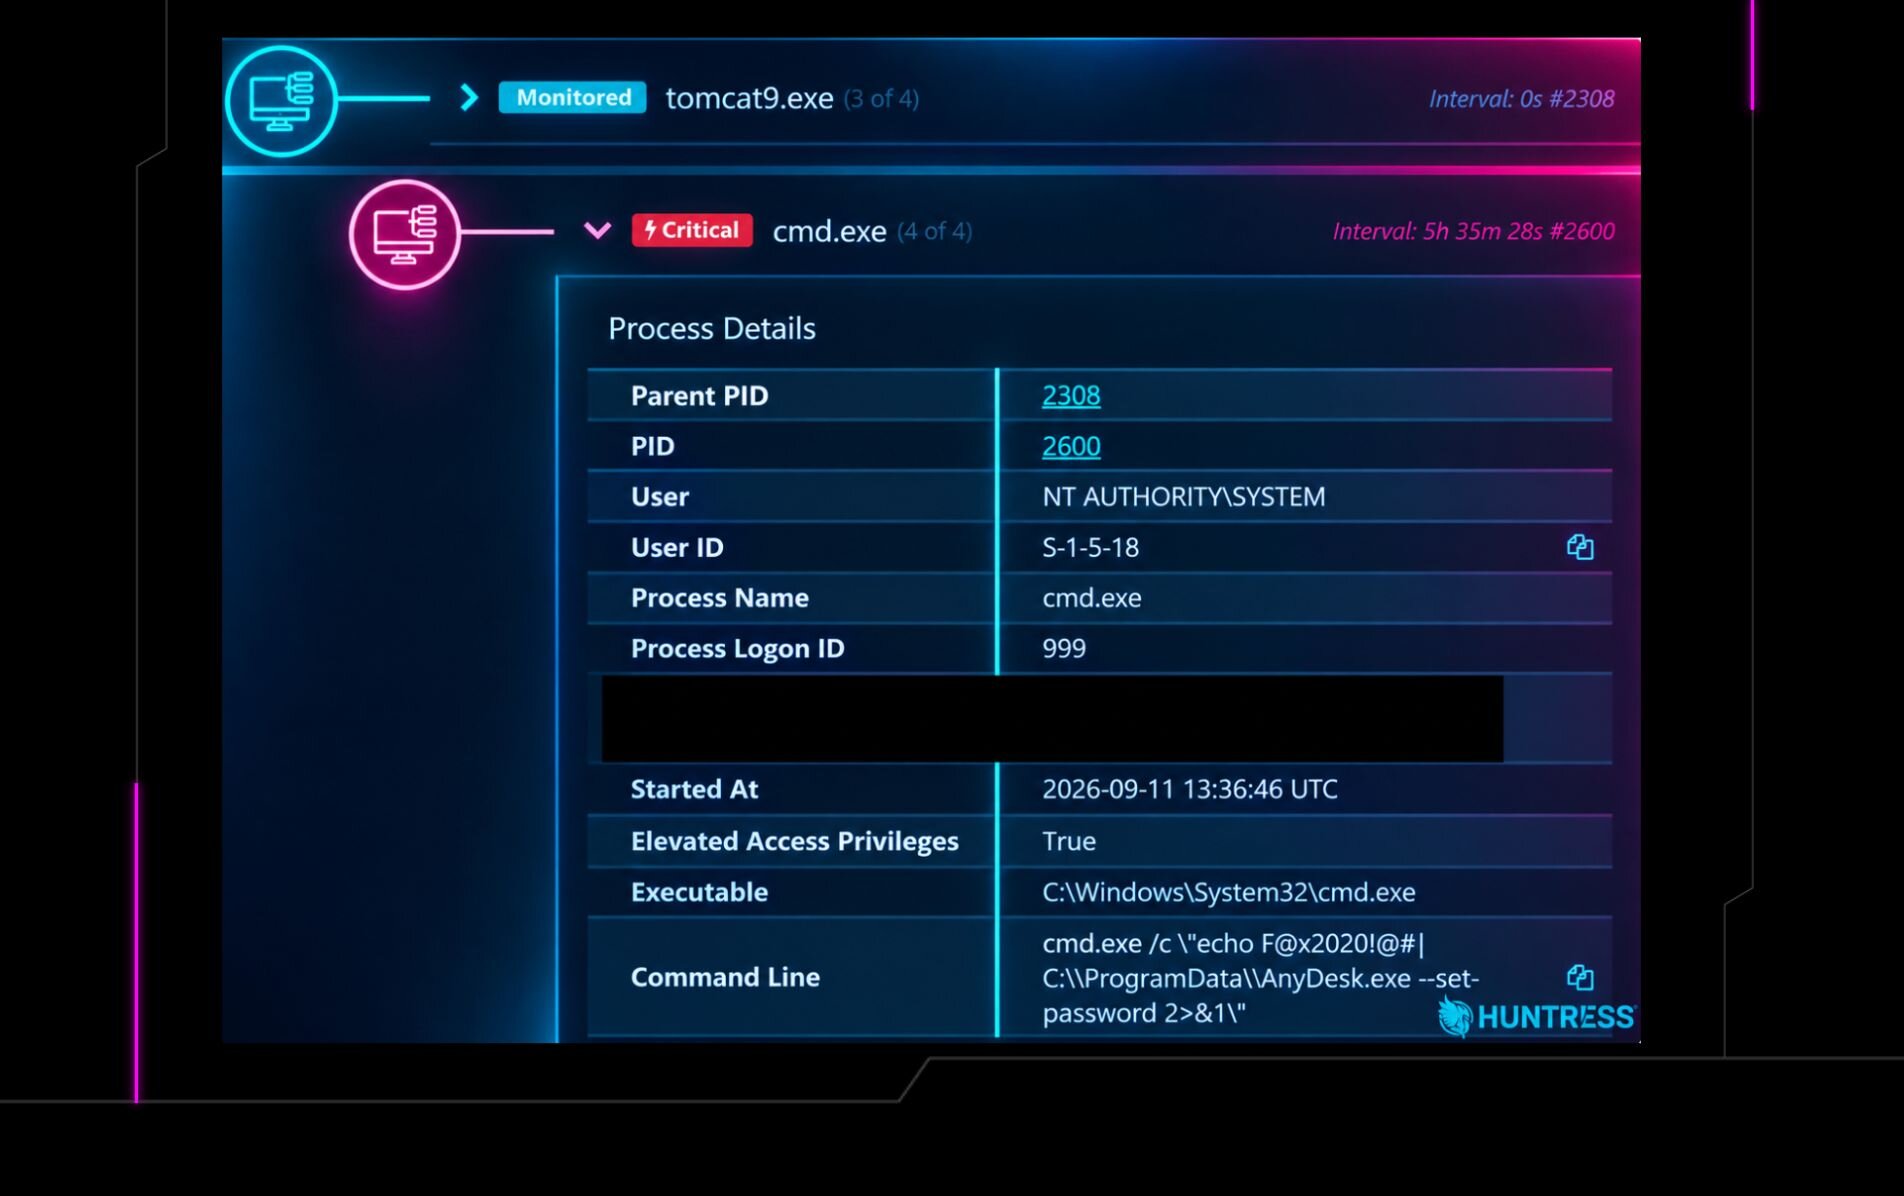
In early September 2026, a threat actor exploited CVE-2025-4632, a vulnerability in Samsung MagicINFO, to compile a cryptominer directly on a victim's endpoint. The attack began with the installation of a rogue AnyDesk instance after multiple failed attempts, followed by creating a new local admin a...
Public Exploits
Checking GitHub for proof-of-concept code…