Skip to content

Threat intelligence API / build

What you can build with the API

Runnable scripts against the live API. A free key covers every one, and most are under 30 lines.

Each page has step-by-step instructions with screenshots, the full script, the output from a real run, and what a run costs in credits. Every page is also available as Markdown or JSON: append .md or .json to the URL.

Alerting

  • Brand and domain dark-web monitor

    Are my brands or domains showing up on the dark web?
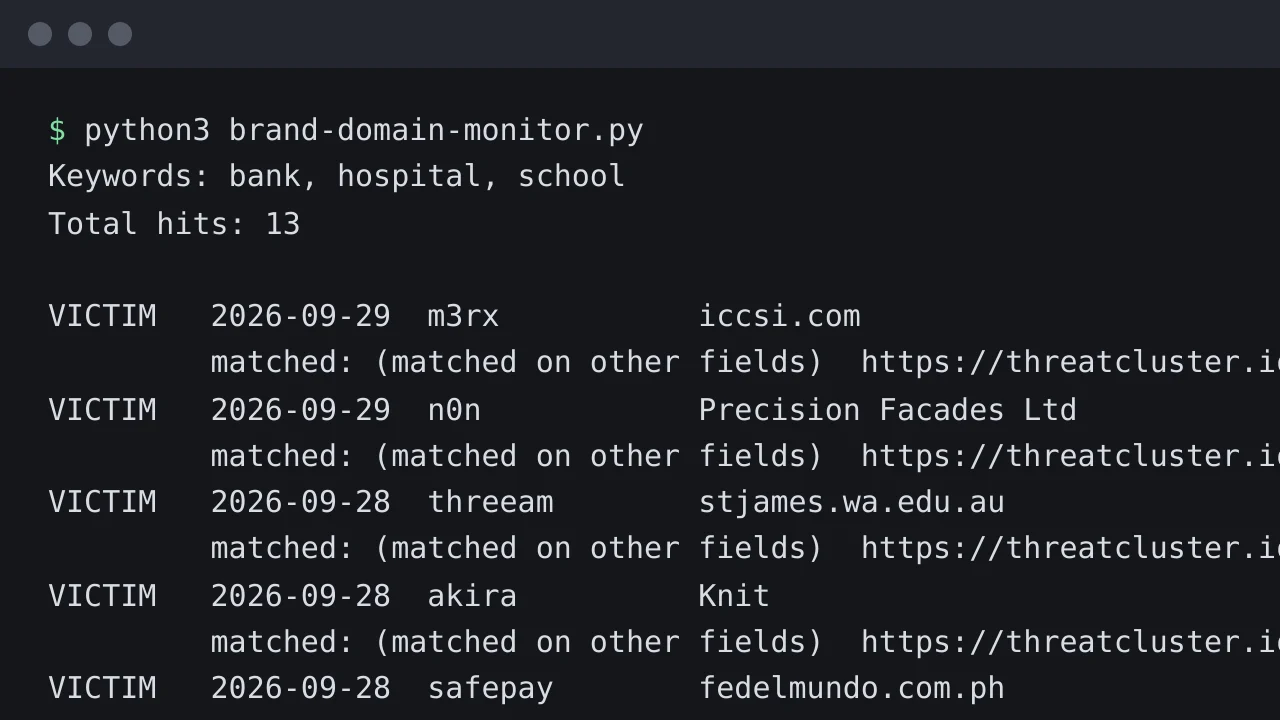
    /darkweb/keyword-hits3 credits per runfree key
    A terminal running the script with the default keywords bank, hospital and school, printing matching leak-site listings with date, group, name, country, sector and link
  • Sector ransomware watch for Slack

    New dark-web ransomware victims for a sector/country, as a Slack message.
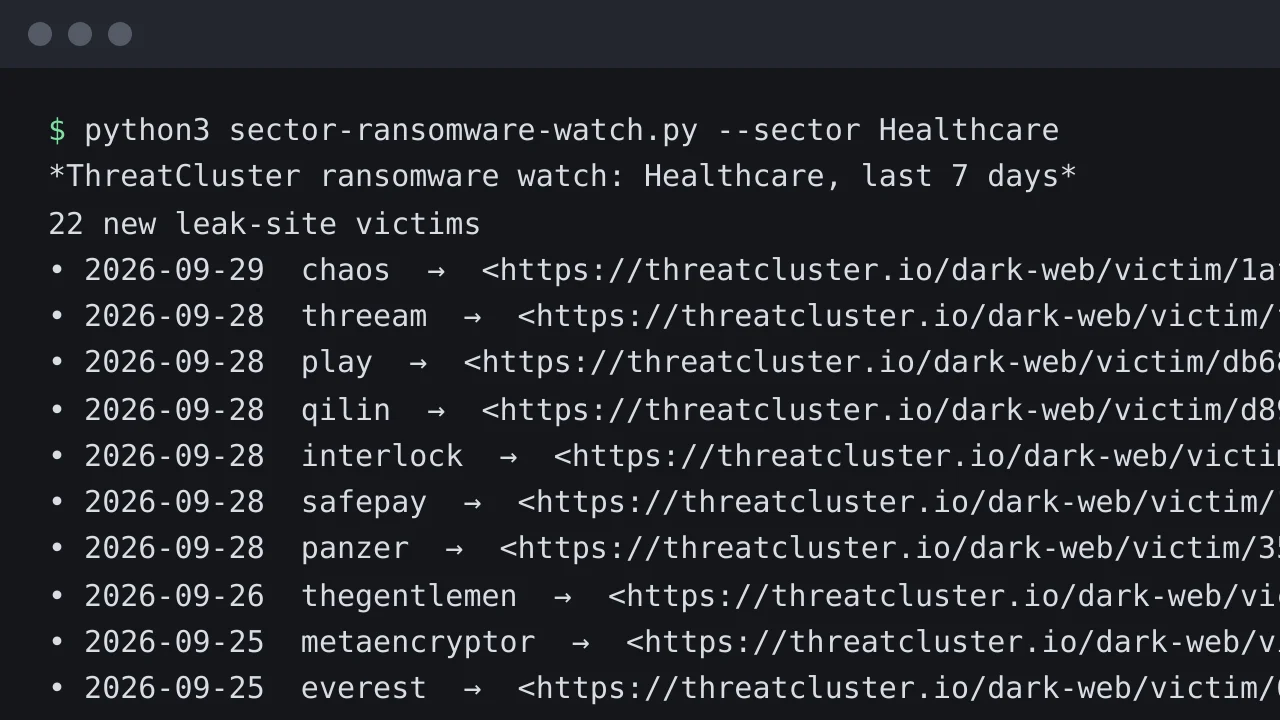
    /darkweb/ransomware/victims /darkweb/ransomware/victims/facets2 credits per runfree key
    A terminal running the script for the Healthcare sector and printing a Slack-formatted list of leak-site victims with the date, group, name and country

Triage

  • CVE triage: KEV and EPSS filter

    From a list of CVE ids, keep only the ones that matter right now.
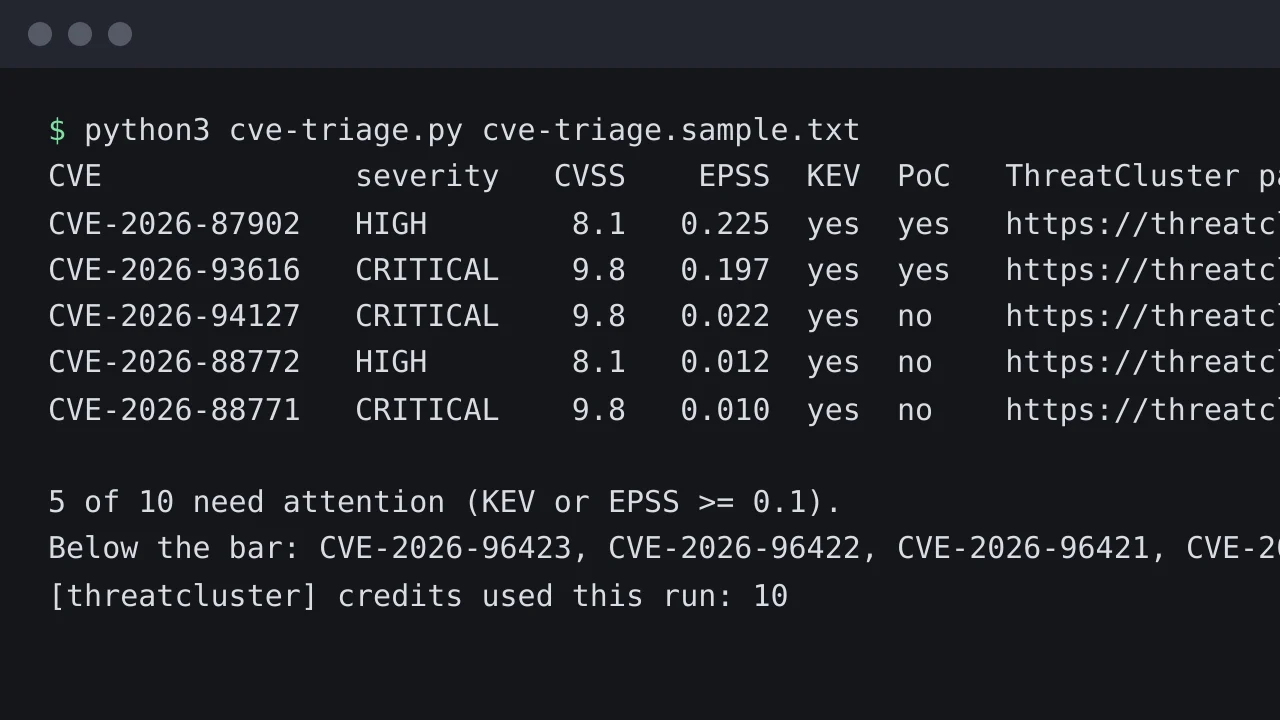
    /vulnerabilities/{cve_id}10 credits per runfree key
    A terminal running the script on ten CVE ids and printing the five that are in CISA KEV, with severity, CVSS, EPSS, KEV and public-exploit columns
  • Exploited this week

    CVEs from the last 7 days that are in KEV or have a public exploit.
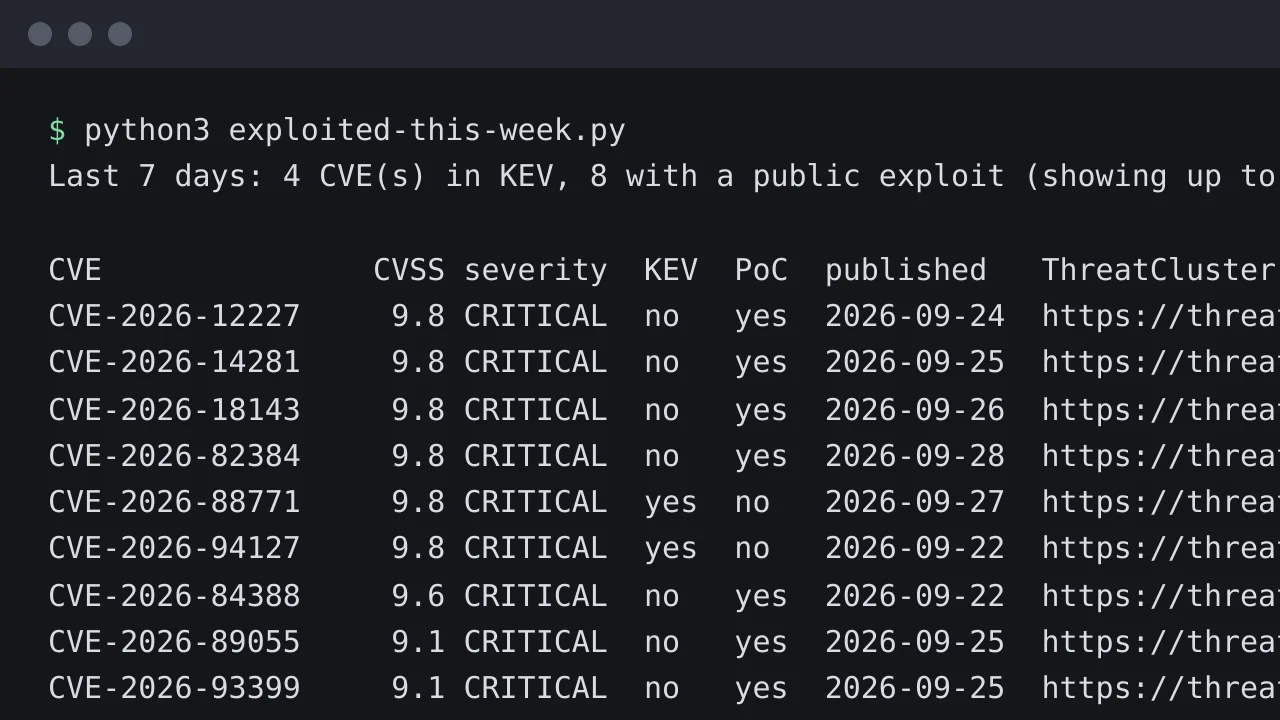
    /vulnerabilities2 credits per runfree key
    A terminal running the script and printing a table of CVEs with CVSS, severity, KEV and public-exploit flags, publication date and a link

Enrichment

  • IOC blocklist export

    Validated malicious domains and IPs as plain blocklists.
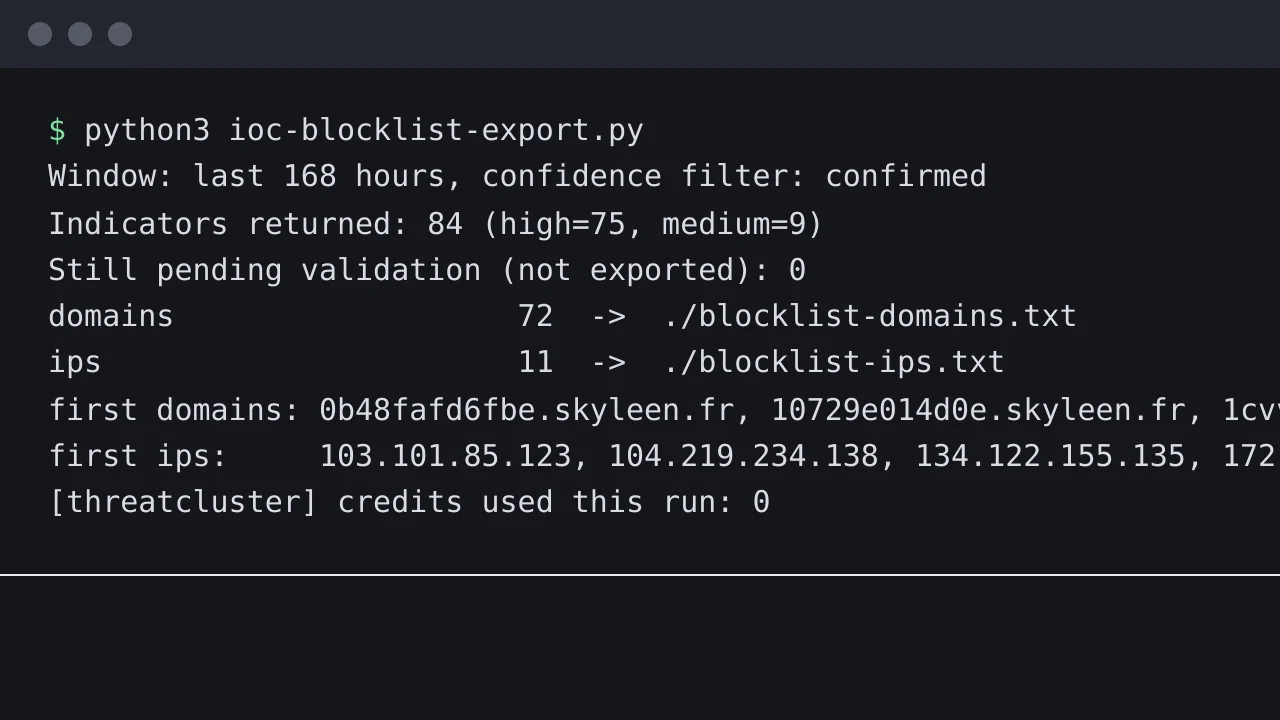
    /iocs/export3 credits per runfree key
    A terminal running the export: 84 indicators returned, none pending, 72 domains and 11 IP addresses written to two files
  • SIEM indicator enrichment

    What does ThreatCluster know about this indicator?
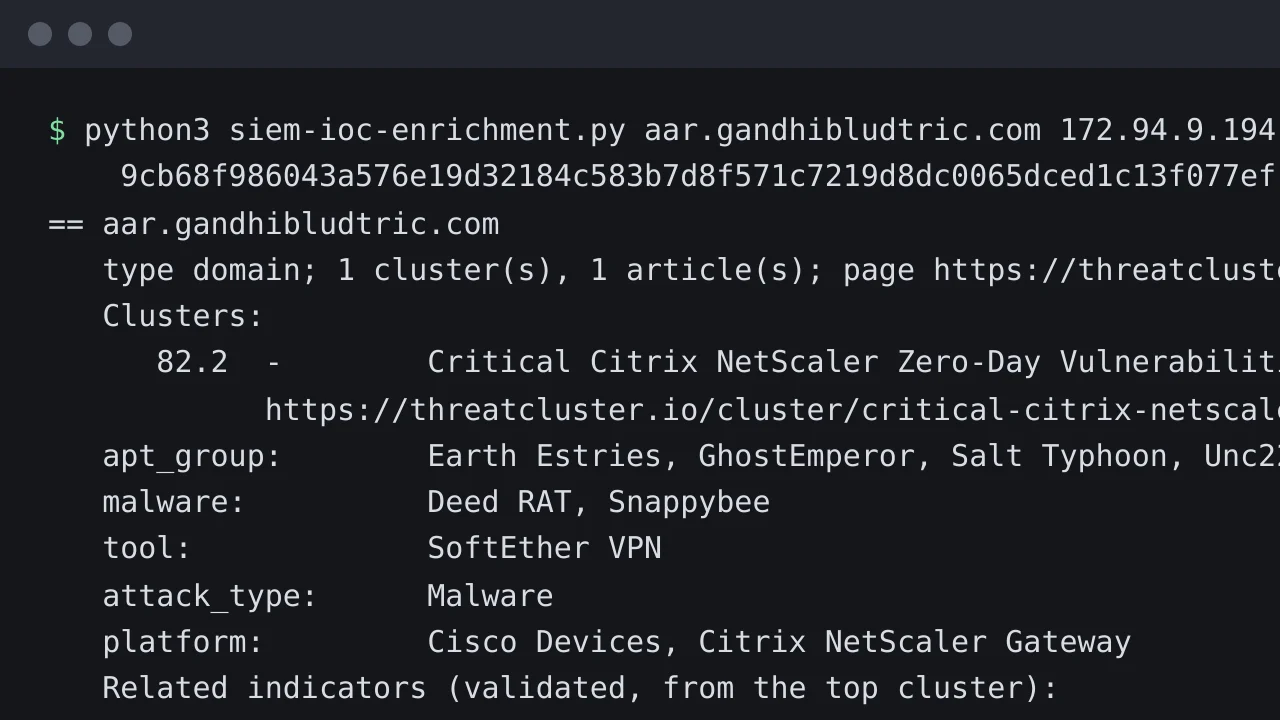
    /entities/search /entities/{type}/{value} /threats/{slug}/iocs6 credits per runfree key
    A terminal enriching a domain and an IP address: each shows its incident with a threat score and link, the threat actors and malware named with it, and related validated indicators

Agents

Integrations · Quickstart and plans · Output formats · OpenAPI reference