
Build your own threat feed
Pick the vendors you run, your industry and where you operate. Your feed, digest and alerts then narrow to what can actually reach you.
Used by 100+ security teams.
Remote Code Execution Vulnerability in C-Kermit
23h agoC-Kermit version 6.0.192 prior to 11.1.515 has a remote code execution vulnerability identified as CVE-2026-129125. This flaw allows Kermit clients to execute shell commands on servers where host commands are disabled by exploiting REMOTE QUERY evalu...

Path Traversal Vulnerability in Seafile SeaDoc Converter
5h agoSeafile SeaDoc converter versions 2.0.4 to 2.0.10 and 3.0.0 to 3.0.7 are affected by CVE-2026-129167, an absolute path traversal vulnerability. This flaw allows unauthenticated attackers with a public token to execute arbitrary code by supplying an a...
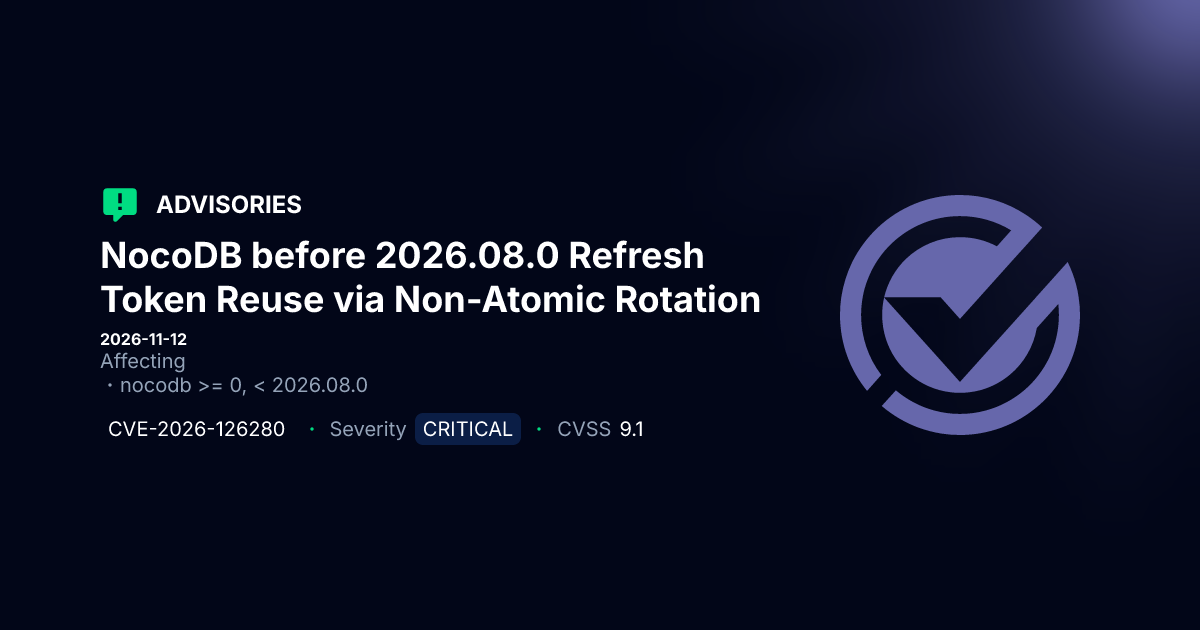
CVE-2026-126280 in NocoDB Allows Refresh Token Reuse
13h agoNocoDB versions prior to 2026.08.0 contain a vulnerability (CVE-2026-126280) that allows attackers to exploit a race condition in refresh-token rotation. This flaw enables the reuse of captured refresh tokens, allowing unauthorized access to user ses...
Chinese Hackers Exploit Stolen LLM API Keys for Credential Theft via ARTEX
4h agoChinese-nexus threat actors utilized ARTEX, an open-source penetration-testing framework, to exploit stolen large language model API keys for credential theft. Amazon Threat Intelligence reported that these operations were detected between October 3...
CVE-2026-129126 in C-Kermit Exposes Servers to Remote Compromise
5h agoC-Kermit versions prior to 11.1.515 contain a heap buffer overflow vulnerability (CVE-2026-129126) in the putsrv() function, allowing attackers to send crafted packets that can overwrite memory beyond the srvcmd buffer. This vulnerability affects ser...
Explore the intelligence behind this feed
Every actor, malware family, CVE and company in the reporting has its own intelligence page — AI overview, timeline, relationships, IOCs. No login needed.
Authentication Bypass in Vvveb CMS Exposed to Attack
10h agoA vulnerability, CVE-2026-126377, was disclosed for Vvveb versions before 1.0.9.0, allowing unauthenticated attackers to exploit an authentication bypass in the generateCookie() function. This vulnerability enables attackers to brute-force cookie val...
Falcon C2 Framework Compromises Government Browsers in Southeast Asia and Middle East
9h agoUnit 42 has identified the Falcon command-and-control framework, also known as XG or Xiàng Gē, which has been used to compromise browsers of government entities in one Middle Eastern country and four Southeast Asian countries between March and May 20...
Critical RCE Vulnerability in Confluence Data Center Disclosed
20h agoAtlassian has disclosed a critical remote code execution vulnerability (CVE-2026-90436) affecting Confluence Data Center, which utilizes a vulnerable third-party library, Apache Axis. This vulnerability allows attackers to execute arbitrary code if t...

Active Exploitation of CVE-2026-90436 in Apache Axis 1.x Confirmed
10h agoCSIRT Italia has reported active exploitation of CVE-2026-90436 in Apache Axis 1.x, a vulnerability with a CVSS score of 9.8. This flaw allows unauthenticated remote attackers to execute arbitrary code via unsafe deserialization of incoming SOAP mess...
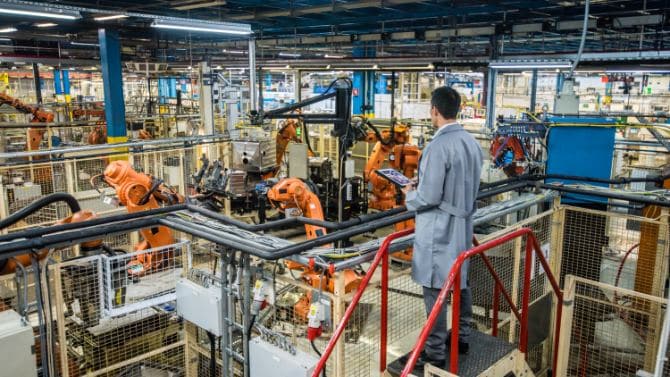
Cyber Attacks Target OT Systems Amid Geopolitical Tensions
16h agoIn November 2026, threat actors exploited vulnerabilities in operational technology (OT) systems, affecting critical infrastructure. A significant incident involved the compromise of refrigeration control panels used by multiple supermarket chains in...

Sign up to keep reading
There's a lot more below this.
A free account unlocks the rest of today's feed, a feed built around your own stack and sector, and the daily digest. 20,000+ sources, clustered in real time.
Free forever. No card. 5 tracked interests + the daily digest included.
How this feed is built
- 20,000+ sources monitored. News, vendor research, CERT advisories, ransomware leak sites. Collected continuously.
- Clustered into incidents. One story becomes one record: deduplicated, scored, with the actors, CVEs and IOCs extracted.
- Rebuilt around you. A free account turns this into your feed, plus the daily digest and alerts.
Trending Threats
Gaining coverage in the last 24 hours
Ransomware victims
Live from our dark web monitoring
Daily Digest
Today's top threats from 20,000+ sources — one five-minute email each morning instead of an hour of scanning. Free, no account needed.