 Feeds.Feedburner
CISA Contractor Exposes Sensitive AWS Credentials on Public GitHub
Article Content

- •A public GitHub repository exposed sensitive AWS GovCloud credentials for six months.
- •The repository contained plaintext passwords and access tokens for multiple internal CISA systems.
- •CISA has confirmed no evidence of data compromise, but some credentials remained valid for 48 hours post-disclosure.
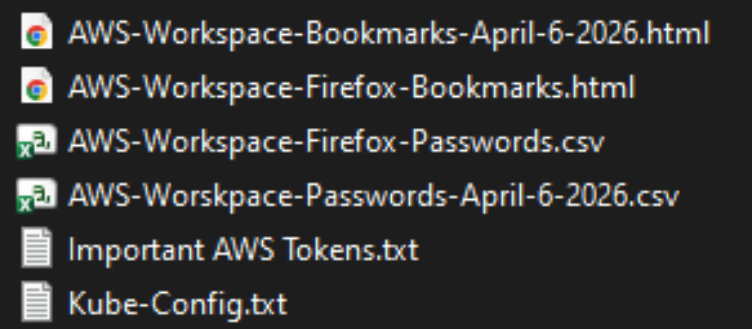
A contractor for the U.S. Cybersecurity and Infrastructure Security Agency (CISA) left a public GitHub repository named 'Private-CISA' exposed for six months, containing sensitive credentials including AWS GovCloud access keys and internal CISA system passwords. Discovered by GitGuardian researcher Guillaume Valadon on May 14, 2026, the repository included files such as 'importantAWStokens' and 'AWS-Workspace-Firefox-Passwords.csv', which detailed access to critical infrastructure. The repository was created on November 13, 2025, and remained accessible until it was taken down on May 15, 2026, after Valadon alerted CISA. Despite the quick response, some credentials remained valid for an additional 48 hours, raising concerns about potential exploitation. CISA has stated there is currently no evidence that sensitive data was compromised as a result of the incident. The leak highlights significant lapses in security practices, especially given CISA's role in advising on cybersecurity.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (41)
Following this threat?
Track CISA and CVE-2025-30066 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…