Skip to content
Product
Use it
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Recipes
Runnable examples for the free key.
Free feeds
RSS, ransomware feed, IOC blocklist, MISP — no key.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
The data
Incident records
900 articles a day become ~70 scored incidents.
Dark web
First-party leak-site collection: victims, groups, markets.
Validated IOCs
Indicators with a false-positive gate; STIX, MISP, CSV.
Vulnerabilities
CVEs with EPSS, KEV and exploit status.
Entity graph
Actors, malware, CVEs, companies — pivotable.
For teams
For service providers
Per-client feeds, alerts and branded digests.
Use cases
How teams and builders use the corpus.
About ThreatCluster
What it is and how it is built.
Pricing
Docs
Reference
OpenAPI (Swagger)
Every endpoint, parameter and response model.
ReDoc
The same reference, long-form.
Examples on GitHub
curl, Python and Node quickstarts; daily spec snapshot.
Guides
Quickstart & plans
Key, scopes, budgets, tiers.
Integrations
Splunk, Sentinel, Elastic, agents and terminals, step by step
Export formats
STIX 2.1, MISP, CSV, text.
CLI setup
Install, log in, wire an agent.
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Recipes
Free feeds
CLI & agents
The data
Incident records
Dark web
Validated IOCs
Vulnerabilities
Entity graph
For teams
For service providers
Use cases
About ThreatCluster
Docs
OpenAPI (Swagger)
ReDoc
Examples on GitHub
Quickstart & plans
Integrations
Export formats
CLI setup
Pricing
Contact
Get a free key
Sign in
Back
CWE-798 - Use of Hard-coded Credentials
CWE Weakness
Threat entity extracted from intelligence sources
Oct 17: 5 mentions
Oct 18: 1 mention
Oct 19: 5 mentions
Oct 20: 5 mentions
Oct 21: 2 mentions
Oct 22: 5 mentions
Oct 23: 1 mention
Oct 17
Oct 20
Oct 23
Entities
›
cwe
›
CWE-798 - Use of Hard-coded Credentials
Frequency
395
occurrences
First Seen
April 15, 2026
Last Seen
October 23, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Threat Actors
Sandworm
Energetic Bear
Berserk Bear
Static Tundra
Ghost Blizzard
Dragonfly
Crouching Yeti
Lazarus Group
APT28
ShinyHunters
Malware
Mirai
Kimwolf
Cobalt Strike
ShadowPad
GodZilla
Tools
PowerShell
Docker
Hugging Face
Curl
Python
Node.js
Shodan
Nginx
CVEs
CVE-2026-20316
CVE-2026-63692
CVE-2026-67269
CVE-2026-63688
CVE-2026-61421
CVE-2026-54472
CVE-2026-67273
CVE-2026-20079
Regions
China
Russia
United States
India
Iran
Sectors
Government
Energy
Financial
Healthcare
Manufacturing
Transportation
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
3
IA
Initial Access
T1078 - Valid Accounts
T1190 - Exploit Public-Facing Application
T1566 - Phishing
4
EX
Execution
T1059 - Command and Scripting Interpreter
T1053 - Scheduled Task/Job
T1203 - Exploitation for Client Execution
T1047 - Windows Management Instrumentation
4
PE
Persistence
T1505.003 - Web Shell
T1543.003 - Windows Service
T1547 - Boot Or Logon Autostart Execution
T1574 - Hijack Execution Flow
2
PE
Priv Esc
T1055 - Process Injection
T1068 - Exploitation for Privilege Escalation
1
DE
Defense Evasion
T1027 - Obfuscated Files Or Information
4
CA
Cred Access
T1003 - OS Credential Dumping
T1110 - Brute Force
T1552.001 - Credentials In Files
T1555.003 - Credentials From Web Browsers
-
DI
Discovery
No techniques detected
1
LM
Lateral Mov
T1021 - Remote Services
-
CO
Collection
No techniques detected
2
C2
C2
T1071 - Application Layer Protocol
T1105 - Ingress Tool Transfer
2
EX
Exfil
T1041 - Exfiltration Over C2 Channel
T1567 - Exfiltration Over Web Service
1
IM
Impact
T1486 - Data Encrypted for Impact
27
techniques detected across
10
tactics
Related Clusters (50)
Critical Cisco FMC Vulnerabilities Under Active Exploitation
Sep 9
·
72 sources
88
Operation Highland: Velvet Ant's Decade-Long Espionage Campaign
Jun 13
·
8 sources
81
Critical Buffer Overflow Vulnerability in Silex Devices (CVE-2026-32956)
Apr 20
·
2 sources
80
Chinese Hackers Exploit Zyxel Switch Vulnerability CVE-2026-7273
Sep 22
·
5 sources
79
AI-Driven Cyber Attacks Targeting Critical Infrastructure and Data Security
Sep 14
·
3 sources
79
CISA Alerts on Critical Flaws in SimpleHelp, Samsung MagicINFO, and D-Link Devices
Apr 26
·
3 sources
78
EU Sanctions Russia Over Ongoing Cyber Espionage Campaign
Jul 13
·
125 sources
78
Critical Authentication Bypass Vulnerability in AWS Loom Exposed
Oct 5
·
3 sources
78
Critical Vulnerability in Issabel Framework Allows Remote Code Execution
Sep 16
·
2 sources
78
Russian FSB Exploits Vulnerable Routers to Target Critical Infrastructure
Jul 13
·
51 sources
78
Critical Vulnerabilities in Yarbo Robot Firmware Expose Devices to Remote Attacks
May 7
·
0 sources
78
Escalating Cyber Threats Targeting U.S. Critical Infrastructure
Aug 12
·
1 sources
78
Russia Hacks Civilian Cameras to Monitor NATO Military Logistics
Jul 11
·
20 sources
77
APT36 Launches Operation RapidRust with New Rust Malware Tools
Sep 18
·
4 sources
77
Iranian Hackers Disable UK Power Plant for Four Days
Aug 22
·
80 sources
77
VerdantBamboo's 18-Month Cyber Campaign Targets Managed Service Providers
Jun 5
·
1 sources
76
Harvester APT Group Unveils New GoGra Linux Backdoor Using Microsoft Graph API
Apr 22
·
9 sources
76
Go Malware Campaign Targets Terraform Providers and Go Modules
Sep 23
·
2 sources
76
SHEETCREEP Espionage Campaign Uses UAE-India Lure for RAT Deployment
Jun 12
·
3 sources
76
State Actors Target Water Systems Amid Weak Cyber Defenses
Jun 26
·
2 sources
76
HOLLOWGRAPH Malware Exploits Microsoft 365 Calendars for Espionage
Jul 20
·
9 sources
75
Critical SQL Injection and XSS Vulnerabilities in RoundcubeMail Affect Fedora Users
Jun 4
·
2 sources
74
Russian Cyber Threats Targeting Consumer Routers
Aug 24
·
2 sources
74
Over 24,000 Servers Expose Password Hashes via BMC Vulnerability
Jul 28
·
9 sources
74
Human Attacker Exploits Marimo RCE at Machine Speed
Sep 14
·
4 sources
74
LiteLLM Supply Chain Attack Exposes Critical Credentials
Jun 12
·
0 sources
74
Iranian Hackers Breach US Gas Station Fuel Monitoring Systems
May 16
·
38 sources
74
Malware Threat from Image Processing Packages
Oct 13
·
0 sources
73
Critical cPanel Vulnerability Exploited for Hosting Server Compromise
Sep 22
·
1 sources
73
Microsoft Issues Critical Security Patches for August 2026
Aug 12
·
2 sources
73
Critical FreePBX Vulnerability Exposes User Portals to Attackers
May 20
·
3 sources
73
Massive Security Flaw Exposes 1.1 Million Baby Monitors to Hackers
May 14
·
2 sources
73
Mustang Panda Espionage Campaigns Target India's Government and Energy Sectors
Jun 30
·
2 sources
73
Critical Vulnerabilities in Exposed MCP Servers Threaten Sensitive Data
Jul 29
·
2 sources
73
Evolution of Chinese-Nexus Cyber Operations: Strategic Long-Term Threats
Apr 2
·
255 sources
73
Cisco FMC Static Credential Vulnerability Under Active Exploitation
Jul 30
·
19 sources
72
Critical Vulnerabilities in SxDevOps Expose Remote Code Execution Risks
Sep 20
·
6 sources
72
Acer Addresses Critical Zero-Day Vulnerabilities in Wave 7 Routers
Jun 4
·
4 sources
72
Gitea Vulnerability Exposes 30,000 Private Container Images to Attackers
May 28
·
4 sources
72
Critical Vulnerabilities Discovered in Apache OFBiz Affecting All Versions Pre-24.09.06
May 21
·
3 sources
72
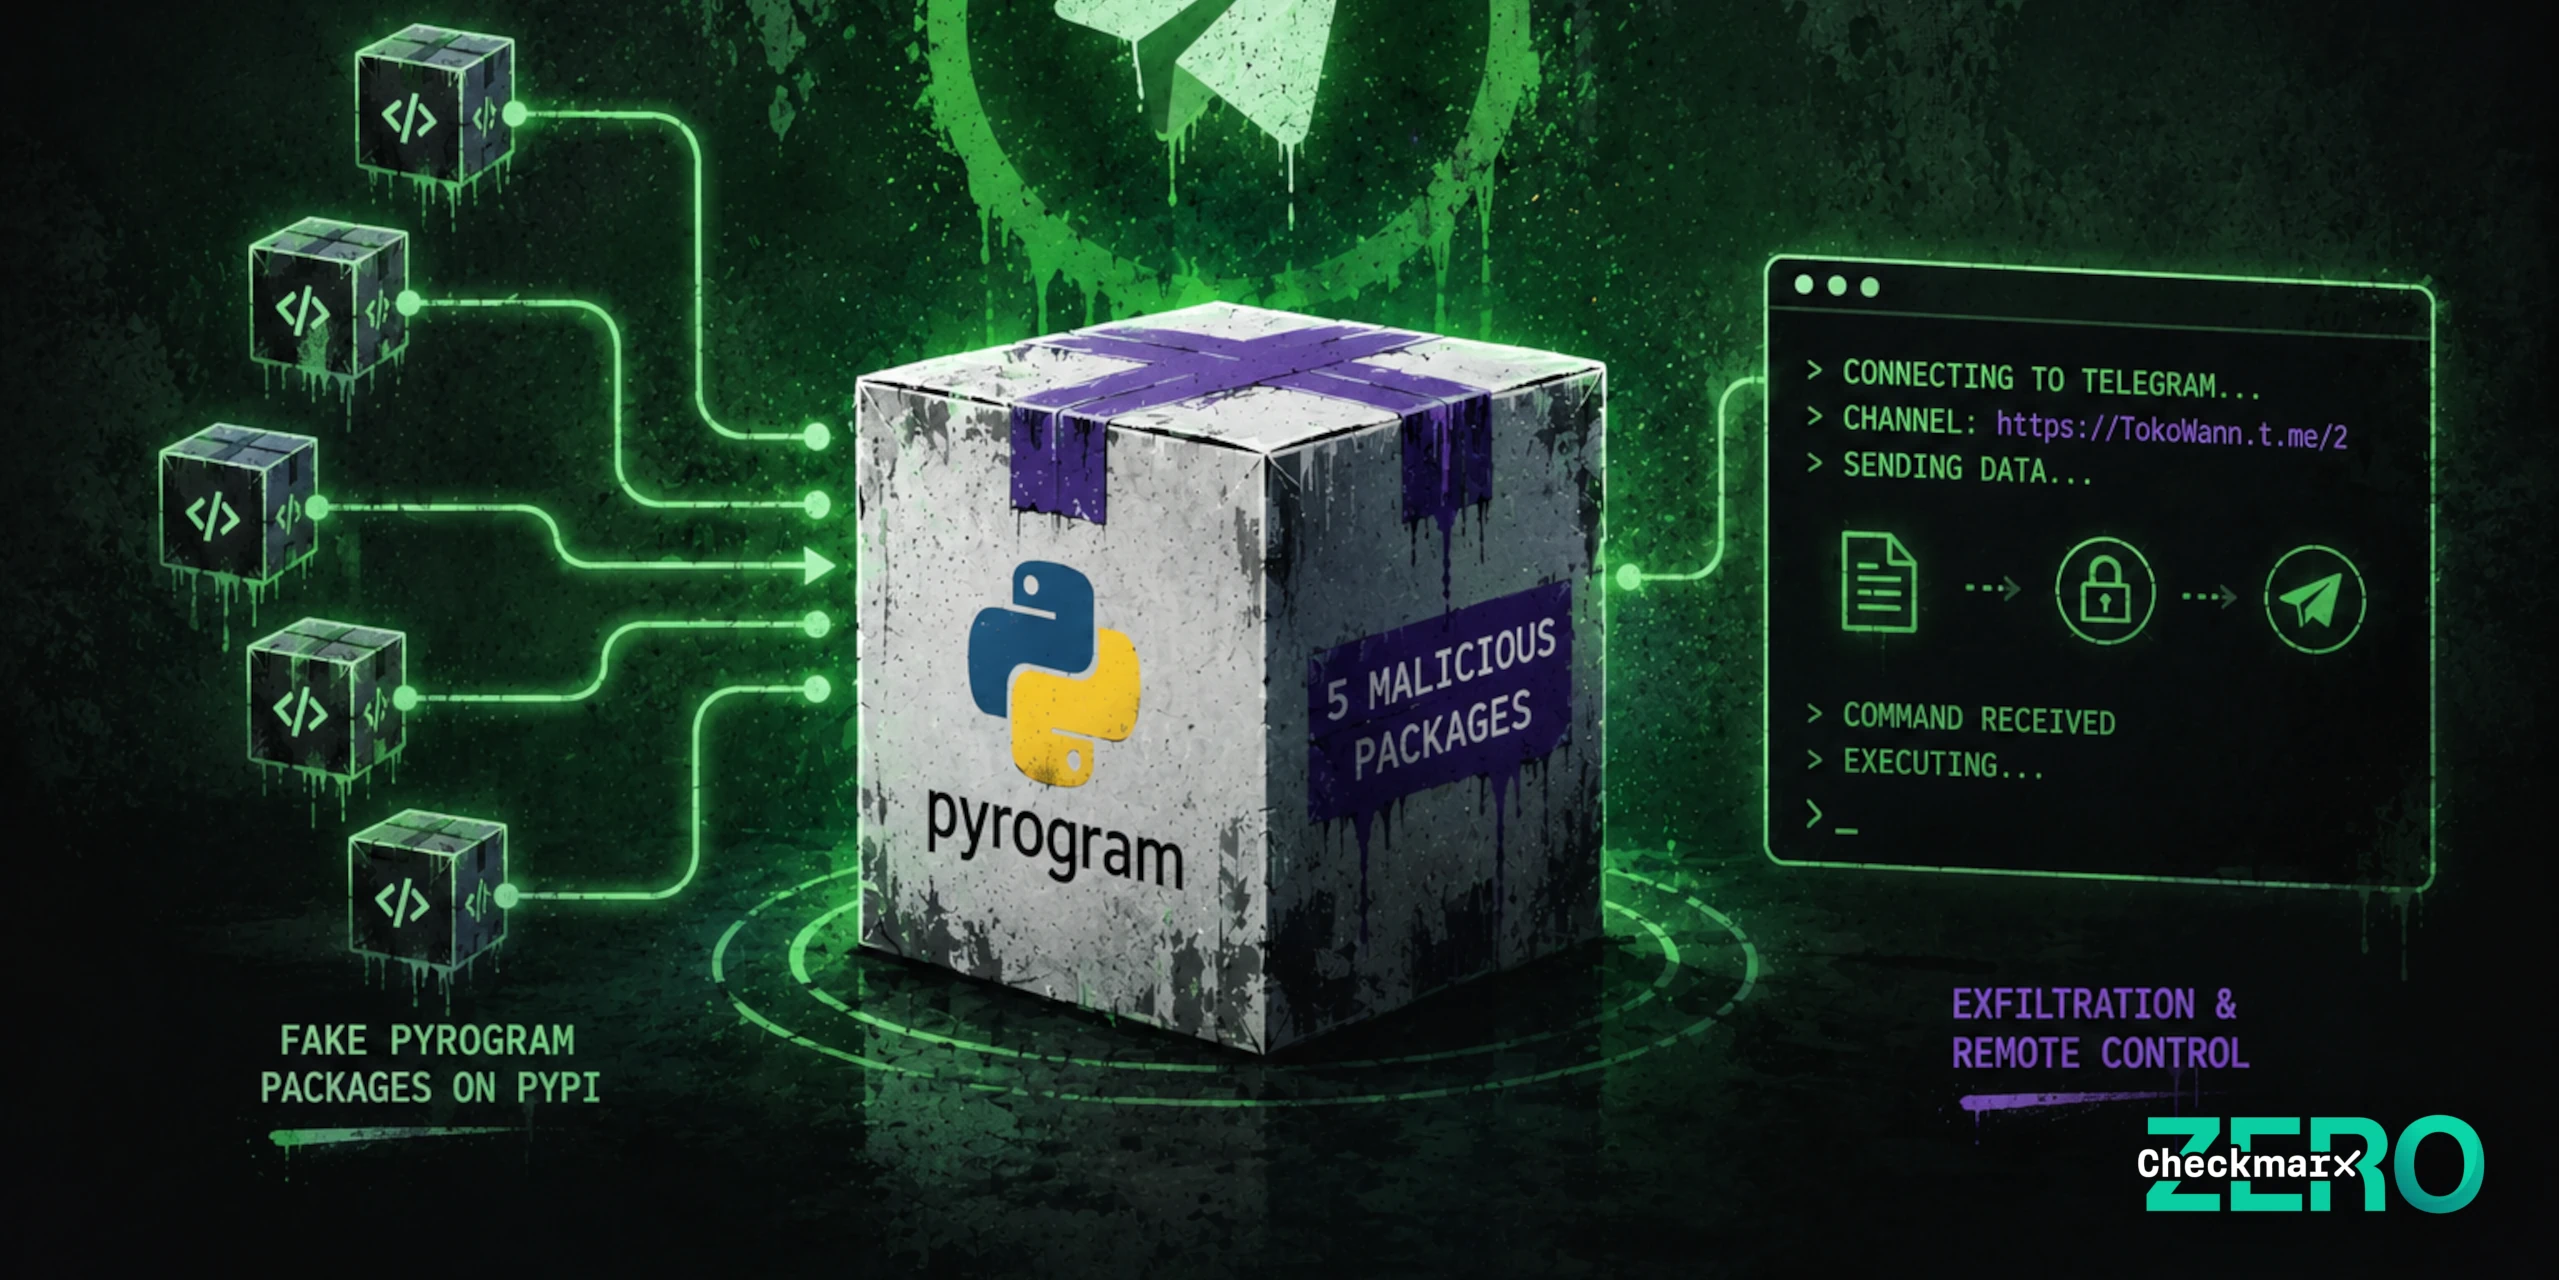
Operation Navy Ghost Targets Telegram Bot Developers with Malicious PyPI Packages
Jun 30
·
2 sources
72
Zeabur Shuts Down After Major Security Breach Exposing 3.2M Records
2d ago
·
2 sources
72
Critical CVE-2026-76658 Vulnerability in HPE Fabric Composer
Sep 2
·
2 sources
72
Toy Ghouls Launch GenieLocker Ransomware Targeting Russian Manufacturing
Jul 30
·
3 sources
72
Smishing Triad's JWR Kit Targets Victims via SMS Phishing
Sep 16
·
2 sources
71
Novo Nordisk Data Breach Exploits Hardcoded GitHub Tokens
Sep 12
·
2 sources
71
TeamFiltration Campaign Targets Microsoft 365 Accounts in Chile
Sep 24
·
3 sources
71
Mini Shai-Hulud Supply Chain Attack Targets SAP npm Packages
Apr 29
·
545 sources
71
Critical Security Bypass in Fedora Keylime Affects Multiple Versions
Jun 7
·
2 sources
71
AI-Driven Ransomware Attack Completes in Under 10 Hours
Sep 2
·
23 sources
71
Prev
1 / 10
Next
Related Articles (50)
Darktrace
·
10h ago
CSIS Significant Cyber Incidents
www.csis.org
·
11h ago
Gamaredon X Turla Collab
www.welivesecurity.com
·
16h ago
Fishmongers Arsenal Upgraded Sprysocks Windows
www.welivesecurity.com
·
19h ago
MAL 2026 2144
osv.dev
·
1d ago
Trigger Dev Before 4.5.6 Authentication Bypass Via Hardcoded Default Secrets
www.vulncheck.com
·
1d ago
Ransomware Attack Encrypts 182GB of Data Following Decade
The420.In
·
1d ago
Nowsecure Uncovers Multiple Security And Privacy Flaws In Deepseek Ios Mobile App
www.nowsecure.com
·
2d ago
Zeabur shutting down after second security breach in two months
Bleepingcomputer
·
2d ago
October 2026 Security Incident
zeabur.com
·
2d ago
Pages Node 7292606
www.ibm.com
·
2d ago
CVE Alert: CVE-2026-109126 – IBM
Redpacketsecurity
·
2d ago
“'Password1' is not an appropriate password”: Two Welsh organisations reprimanded after ...
Ico.Uk
·
3d ago
Litellm Credential Stealer Hidden In Pypi Wheel
www.stepsecurity.io
·
3d ago
Bearer Bearer
github.com
·
3d ago
Api Security Risks
cybelangel.com
·
4d ago
AI Security Study: Attacks on AI Infrastructure Rather Than the AI Model
B2B-Cyber-Security.De
·
4d ago
Bearer CLI: Free, source-available code security scanning tool (SAST)
Helpnetsecurity
·
4d ago
Startup Fortune
startupfortune.com
·
4d ago
AI Agents Breached Indian Companies Live Systems and Nobody Noticed
Philiphall
·
5d ago
Hackers Used AI-Written Code to Spy on Government Linux Servers for Months, Unit 42 Finds
Ibtimes.Sg
·
5d ago
India's cybersecurity agency says AI agents breached its computer systems
En.Yenisafak
·
5d ago
AI Agents Accessed Indian Organizations Without Authorization, CERT
Securityaffairs
·
6d ago
AI Agents Accessed Indian Organizations Without Authorization, CERT
Securityaffairs.Co
·
6d ago
How Abliterated Models Can Get You Pwned
projectdiscovery.io
·
6d ago
Hooking Candiru Another Mercenary Spyware Vendor Comes Into Focus
citizenlab.ca
·
6d ago
CERT-In: AI Agents Accessed Indian Firms’ Live Systems
Cyberkendra
·
6d ago
AI agents access confidential data, India's cybersecurity agency issues 'critical' alert
Newindianexpress
·
6d ago
PEERSTITCH malware: How Attackers Compromised 500 Firewalls Through FortiManager
Securityaffairs.Co
·
Oct 16
CERT
Thehackernews
·
Oct 16
October alert
www.cert.ssi.gouv.fr
·
Oct 16
Mandiant attributes the attacks
cloud.google.com
·
Oct 16
CVE-2026-102764: BeyondTrust Zero
Cyberkendra
·
Oct 16
Legal Aid Agency hackers made off with records dating back to 1978
Theregister
·
Oct 15
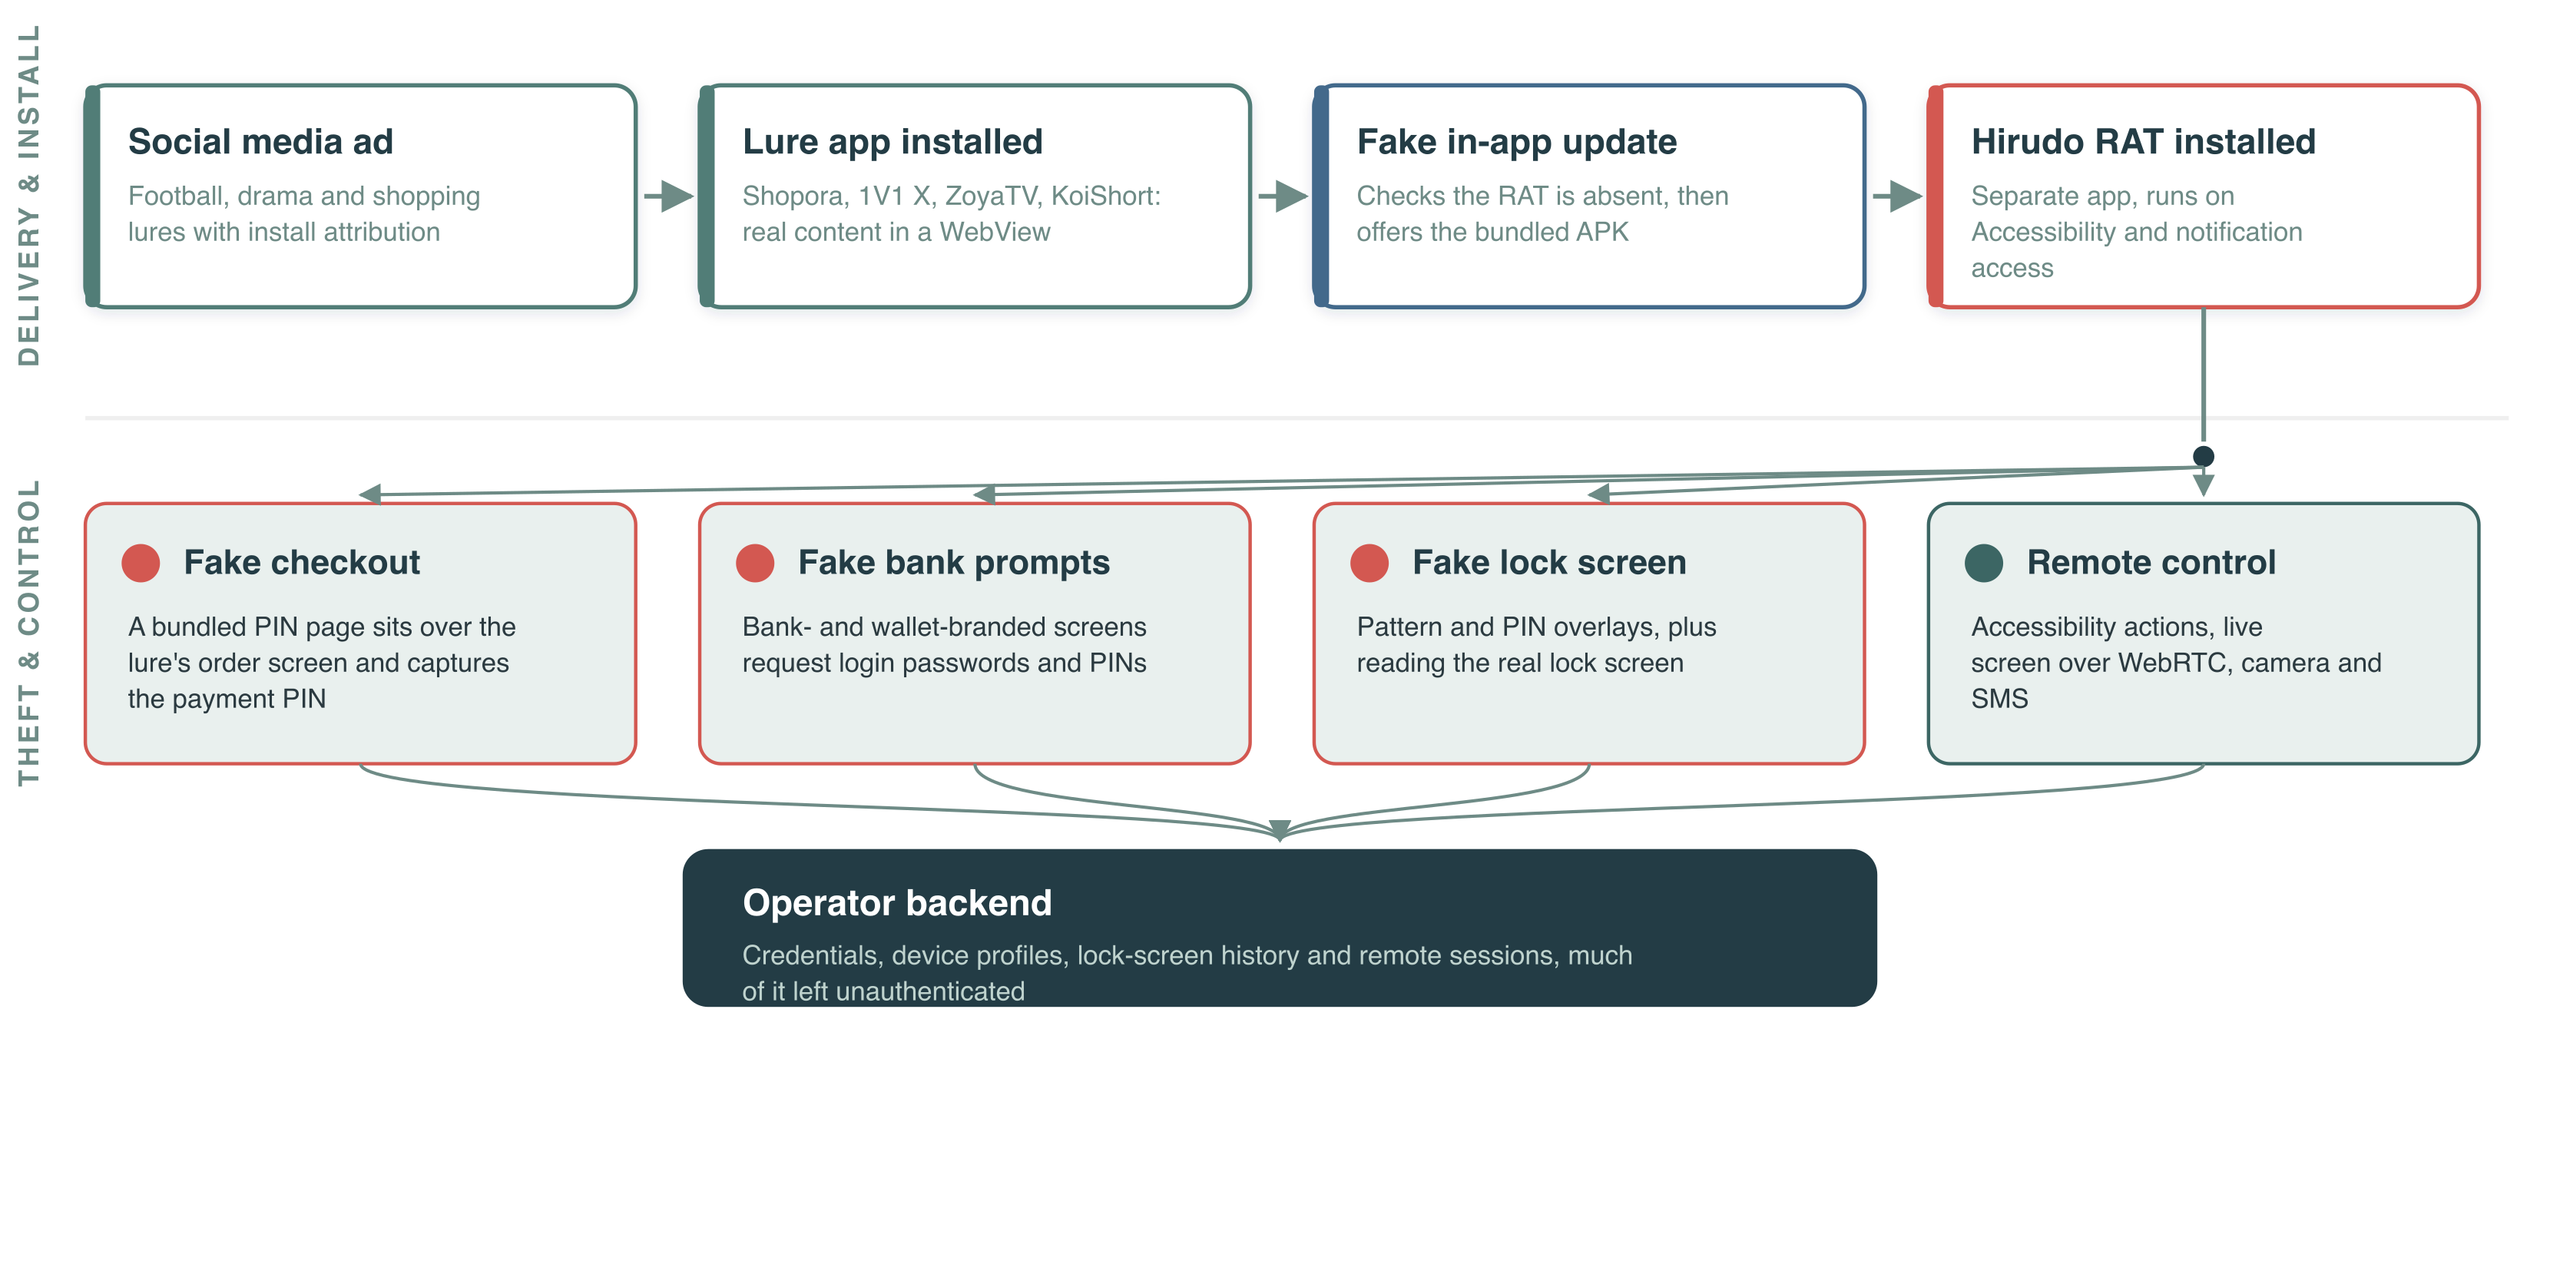
Hirudo Android Trojan Replaces Banking Apps to Steal Credentials
Securityaffairs.Co
·
Oct 15
JadePuffer
www.sysdig.com
·
Oct 14
Smart Devices Law
www.ncsc.gov.uk
·
Oct 14
Apple launches hub as Anthropic issues connected home AI risk warning
Insurancebusinessmag
·
Oct 13
MAL 2026 17330
osv.dev
·
Oct 13
LG smart TVs vulnerable: attackers can bypass webOS security and gain root
Cybernews
·
Oct 13
AI Agent Security: Best Practices for Safe Deployment
Blog.Gitguardian
·
Oct 13
Small AI Models Could Soon Self-Replicate on IoT Devices, Anthropic Warns
Securityweek
·
Oct 13
Anthropic study warns that small AI models could soon replicate across everyday devices
The-Decoder
·
Oct 13
Utility Cybersecurity
www.oracle.com
·
Oct 13
Lab Dookhtegan Cyber Attack On Iranian Oil Tankers Disrupts Operations
cydome.io
·
Oct 12
Cyber Essentials guide for small businesses
Devpartners
·
Oct 11
Tr Smtp Is The Key Bpfdoor Averat Hitting The Network Edge
www.rapid7.com
·
Oct 9
Research Finds 12 000 Live Api Keys And Passwords In Deepseek S Training Data
trufflesecurity.com
·
Oct 9
Agentcorruption Initial Imds Access
labs.zenity.io
·
Oct 8
Collaboration and Support Platforms are the New Attack Surface
Zscaler
·
Oct 8
Prev
1 / 10
Next
Related Entities
Sandworm
Energetic Bear
Berserk Bear
Static Tundra
Ghost Blizzard
Dragonfly
Crouching Yeti
Lazarus Group
APT28
ShinyHunters
CyberAv3ngers
Turla