 Blog.Gitguardian
Kubernetes Cluster Compromised via Leaked AWS Credentials
Article Content

- •Attackers exploited leaked AWS IAM credentials to compromise Kubernetes clusters.
- •Poisoned Docker images were deployed, allowing lateral movement and data theft.
- •Mitigations include using private registries and enforcing read-only credentials.
Recent incidents highlight a significant threat to Kubernetes clusters, where attackers exploited leaked AWS IAM credentials from developer workstations. This allowed them to deploy poisoned Docker images, facilitating lateral movement within the cloud environment. The attack chain aligns with known MITRE ATT&CK techniques, including credential theft and resource hijacking. In one case, attackers accessed sensitive registry credentials, which could lead to further breaches across multiple organizations. The Shai-Hulud supply chain attack exemplifies this risk, emphasizing the need for robust security measures. The current status indicates that while some attacks were detected in time, the potential for widespread damage remains high. Organizations are urged to implement private container registries and limit credential access to mitigate risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Shai-hulud and AWS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
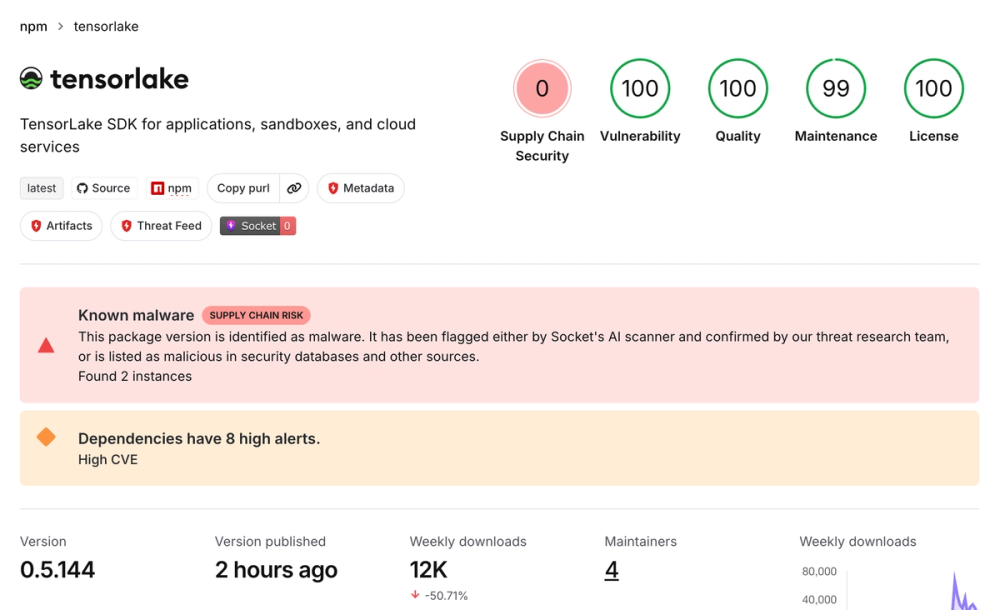 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…