 Back X
AGTP on X: "WatchTowr just flagged an unauthenticated RCE in Java, CVE-2026
WatchTowr just flagged an unauthenticated RCE in Java, CVE-2026-114938. Here's what you need to know.
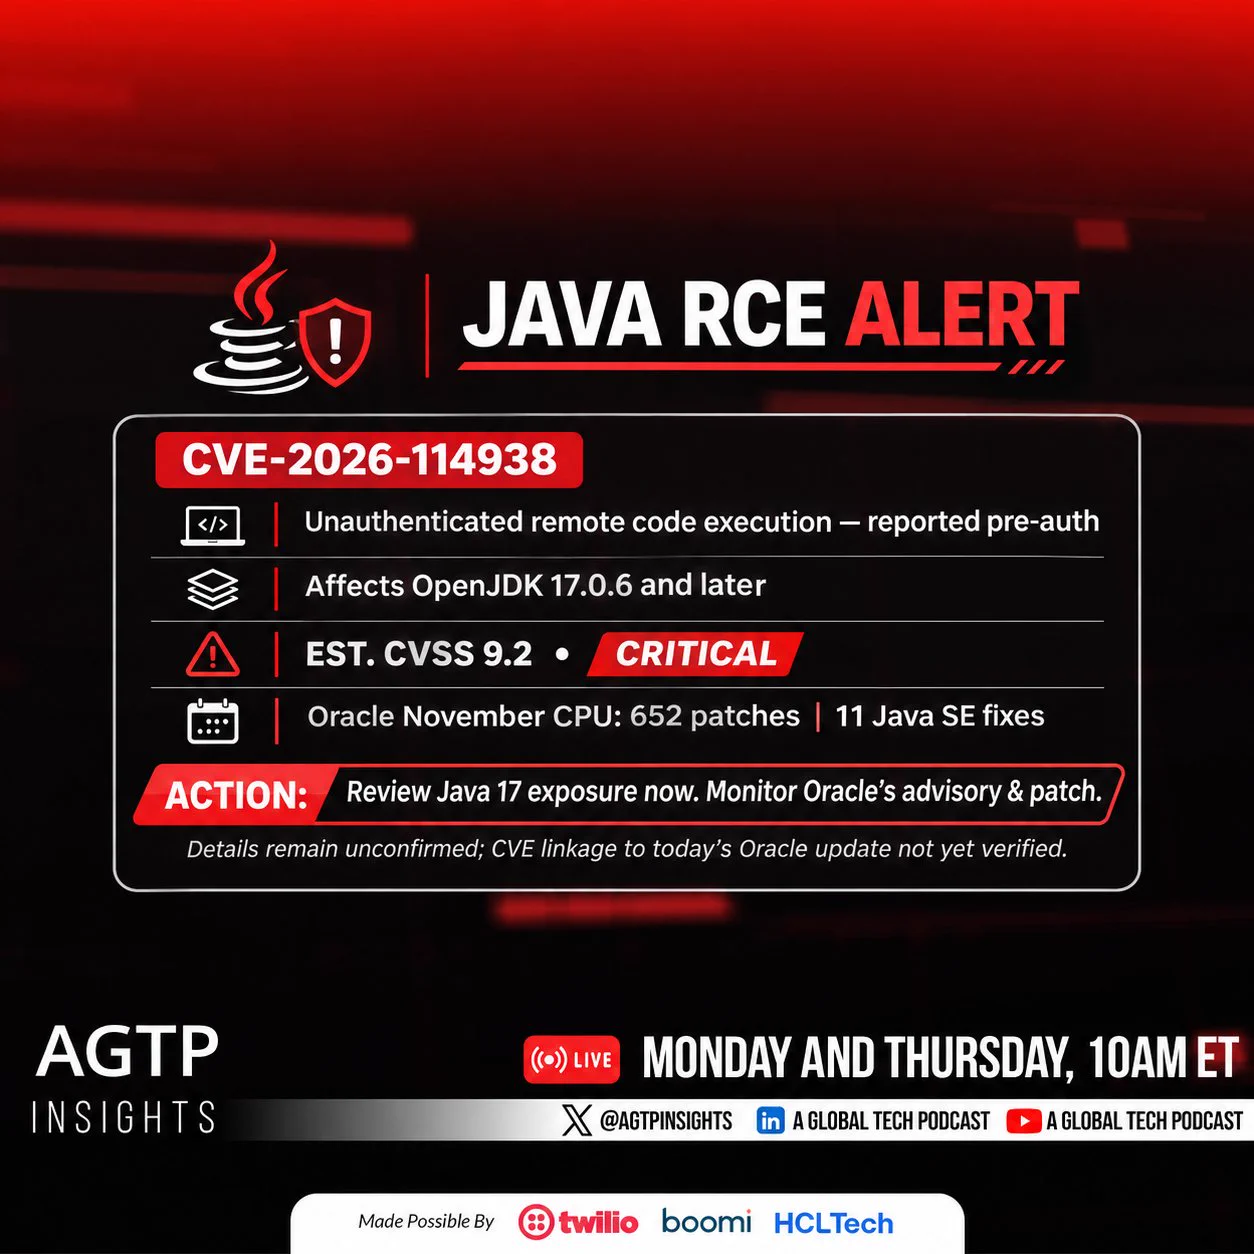
watchTowr Intel posted on November 17, 2026 that it is aware of public reports of an unauthenticated remote code execution flaw in Java. It affects OpenJDK 17.0.6 and later. watchTowr says details are still unconfirmed. Its advice is to review your Java environments now and monitor for vendor announcements.
The flaw is reported as pre-auth, so an attacker needs no login. Cyber Kendra and others rate it critical, with an estimated CVSS 4.0 score of 9.2. The fix is due in Oracle's November Java update. Some people are already calling it "java2shell".
Oracle's November Critical Security Patch Update goes live today, Tuesday. Oracle publishes these on the third Tuesday of the month. One report says the release carries 652 patches. It says the Java SE section has 11 new security fixes, all remotely exploitable without authentication. Oracle's advisory page for the update is at
. The CVE is not yet confirmed as one of those fixes.
South Korea is already acting. Cyber Kendra reports an advisory dated November 16 from the country's National Cyber Security Center that flagged the flaw. The Korea Times reports that the National Intelligence Service sent a security advisory to public institutions a Java vulnerability.
Other fixes in today's JDK releases are separate bugs, per researcher Kirill Firsov. They include a libpng use-after-free (CVE-2026-46675), an out-of-bounds read in variable-font handling (CVE-2026-50811), a CID font denial of service (CVE-2026-95512) and a zlib inflate infinite loop (CVE-2026-27171).
- Estimated CVSS 4.0 score: 9.2, critical
- 652 patches in Oracle's November update
- 11 new Java SE security fixes, all remotely exploitable without authentication
If you run Java 17, check your exposure now and watch for Oracle's advisory and patch.
watchTowr Intel is aware of public reports of an unauthenticated RCE in Java, CVE-2026-114938, affecting OpenJDK 17.0.6 and later. Details are still unconfirmed. Review your Java environments now and monitor for vendor announcements.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
