 Back Pokde
Bank Rakyat Under Suspected Cyberattack By Threat Actor "Marlanwg", Website Briefly Defaced
UPDATE 06/11 11:45PM : Bank Raykat says some of its services are currently unavailable at this time. Full statement (translated) as follows:
Dear Valued Customers, Please be informed that the corporate website of Bank Rakyat is currently unavailable. Customers are advised to use mobile applications or digital platforms such as the following: – iRakyat – BRICK – QR2E – i-bizRAKYAT We apologize for any inconvenience caused. Thank you for your patience.
Dear Valued Customers, Please be informed that the corporate website of Bank Rakyat is currently unavailable. Customers are advised to use mobile applications or digital platforms such as the following: – iRakyat – BRICK – QR2E – i-bizRAKYAT
We apologize for any inconvenience caused. Thank you for your patience.
Original article follows.
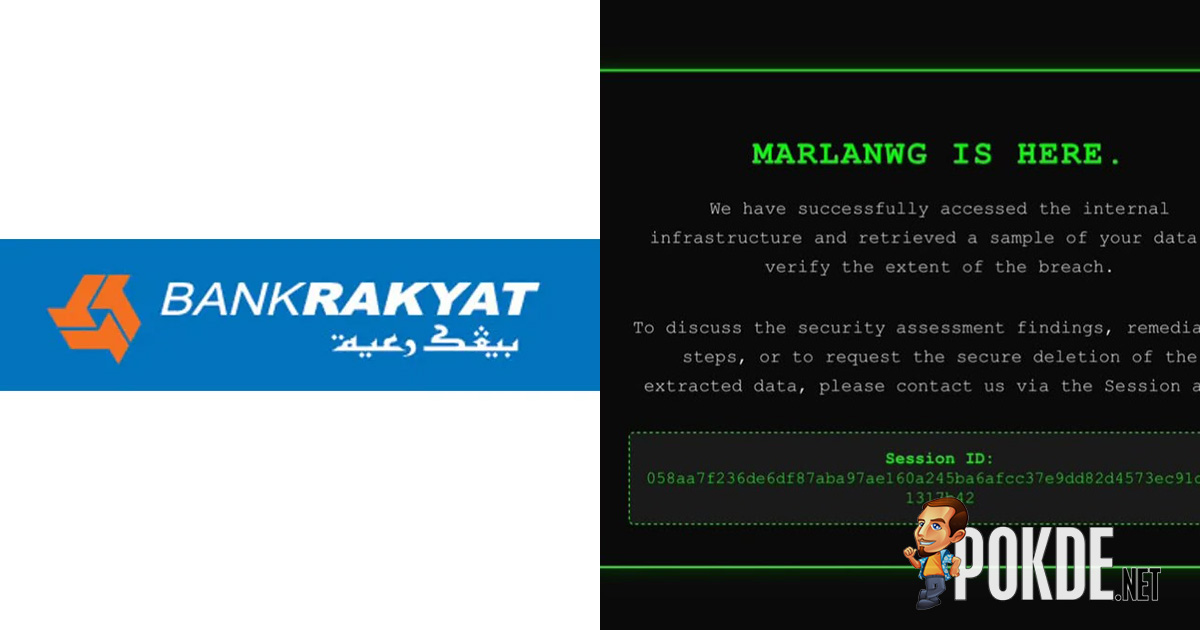
Bank Rakyat faces fresh cyber scrutiny after pages on its official web portal were briefly defaced by an external threat actor operating under the handle “Marlanwg”. The attacker left a prominent notice claiming to have conducted a “security assessment” and asserting unauthorized access to the bank’s internal network infrastructure.
Bank Rakyat Website Briefly Taken Over
The perpetrator left a public note stating: “Marlanwg is here. We have successfully accessed the internal infrastructure and retrieved a sample of your data to verify the extent of the breach” . Bank officials and security teams were instructed to a metadata-private encrypted messaging app, Session, to negotiate data deletion and remediation terms.
The alterations primarily affected public-facing sections of the bank’s portal, including informational pages detailing personal financing options – although the website has since reverted back to normal as of this writing, less than an hour since the defacement was first reported on social media.
The incident arrives on the heels of mounting compliance pressure – Bank Negara Malaysia (BNM) previously penalized Bank Rakyat with a RM1 million administrative monetary penalty under the Risk Management in Technology (RMiT) framework following a separate cybersecurity breach.
As of reporting, Bank Rakyat has yet to issue a formal public statement or announce explicit actions regarding the validity of the hacker’s internal access claims. Until a formal statement has been made, we advise customers of Bank Rakyat to avoid entering sensitive details to avoid potential phishing attacks.
Pokdepinion : It’s chaotic already. Let’s hope it doesn’t get any worse.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
