 Back Securityaffairs.Co
BeatBanker malware targets Android users with banking Trojan and crypto miner
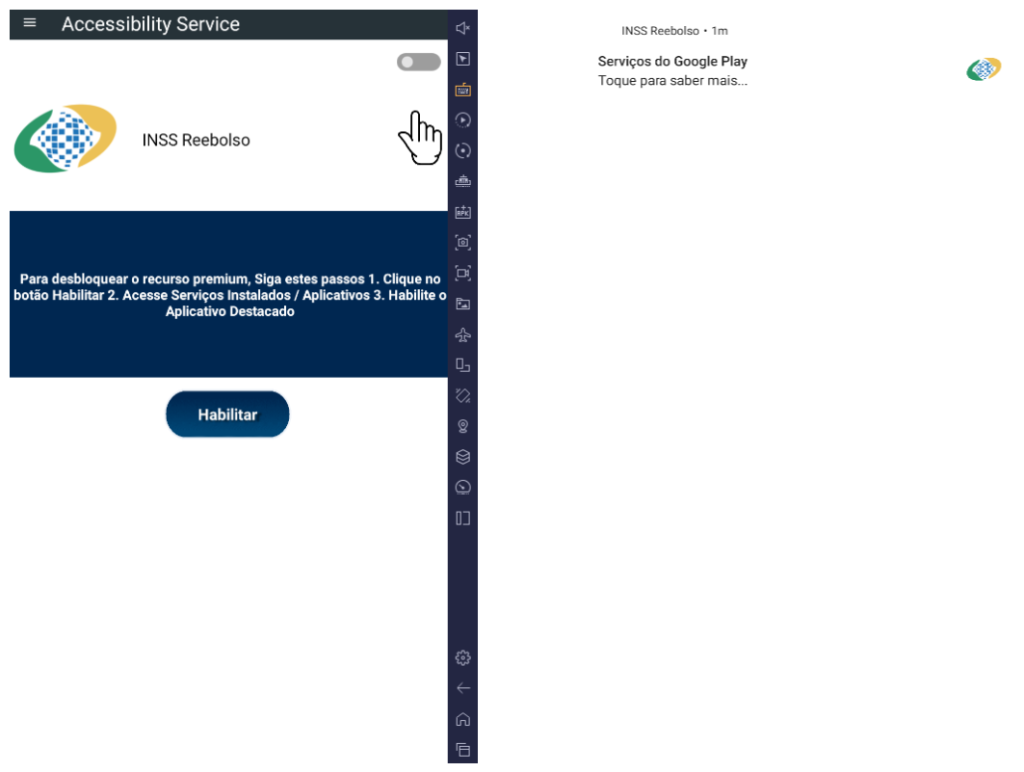
BeatBanker Android malware spreads through fake Starlink apps on websites imitating Google Play Store, hijacking devices, stealing credentials, and mining crypto. A new Android malware called BeatBanker spreads through fake Starlink apps distributed on websites posing as the Google Play Store. Once installed, it hijacks devices, steals login credentials, tampers with cryptocurrency transactions, and secretly […]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
