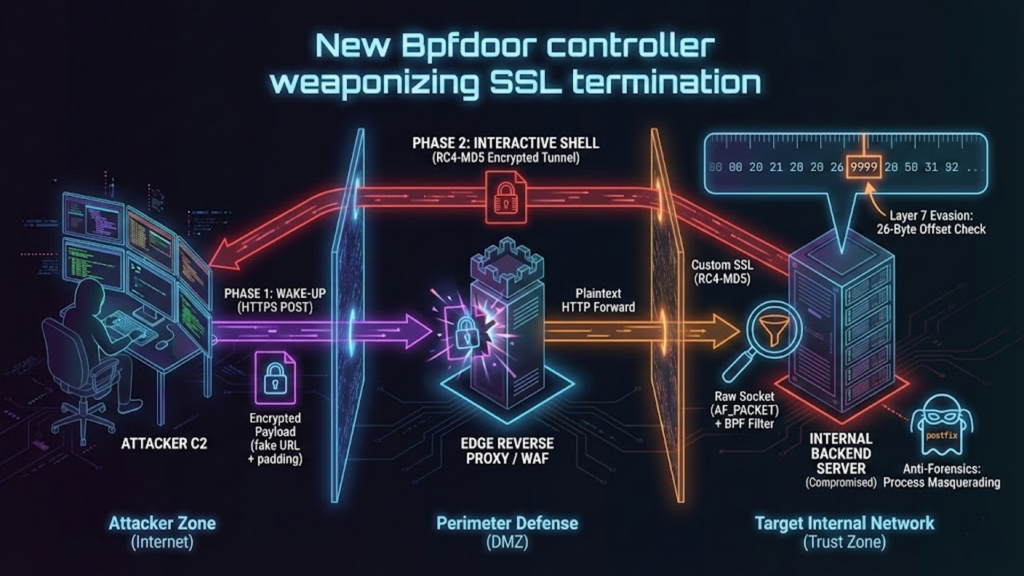
China-linked Red Menshen APT group used stealthy BPFDoor implants in telecom networks to spy on government targets. Rapid7 Labs uncovered a China-linked threat group known as Red Menshen has been running a long-term espionage campaign by infiltrating telecom networks, mainly in the Middle East and Asia. Active since at least 2021, the group uses highly […]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
