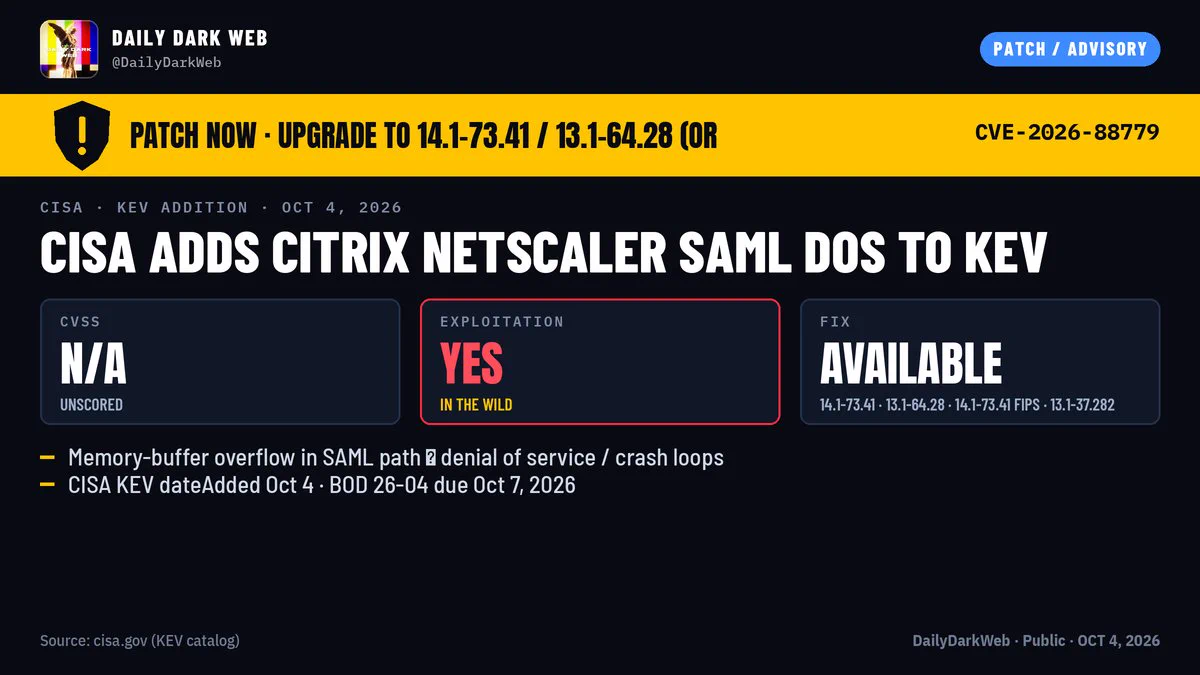
Dark Web Intelligence on X: "🚨 CISA FLAGS NEW CITRIX NETSCALER ZERO-DAY AS ACTIVELY EXPLOITED
Citrix has released emergency patches for a new vulnerability being exploited against NetScaler appliances:
The vulnerability is a memory overflow affecting:
The appliance must be configured as either:
against unmitigated NetScaler deployments.
Repeated exploitation can potentially keep the service unavailable.
CISA's vulnerability intelligence now classifies exploitation as:
and the flaw has been added to the Known Exploited Vulnerabilities catalog.
Some early reporting suggested this vulnerability could allow unauthenticated remote code execution.
Citrix's official assessment lists the impact as denial of service, and Norway's NSM has now explicitly corrected its earlier RCE warning while noting that researchers continue investigating the discrepancy.
Organizations that patched NetScaler recently should CHECK AGAIN.
This is a newly disclosed vulnerability requiring another update.
#Citrix #NetScaler #ZeroDay #CVE202688779 #CISA #KEV #ThreatIntel #DDW"
🚨 CISA FLAGS NEW CITRIX NETSCALER ZERO-DAY AS ACTIVELY EXPLOITED
Citrix has released emergency patches for a new vulnerability being exploited against NetScaler appliances:
The vulnerability is a memory overflow affecting:
The appliance must be configured as either:
against unmitigated NetScaler deployments.
Repeated exploitation can potentially keep the service unavailable.
CISA's vulnerability intelligence now classifies exploitation as:
and the flaw has been added to the Known Exploited Vulnerabilities catalog.
Some early reporting suggested this vulnerability could allow unauthenticated remote code execution.
Citrix's official assessment lists the impact as denial of service, and Norway's NSM has now explicitly corrected its earlier RCE warning while noting that researchers continue investigating the discrepancy.
Organizations that patched NetScaler recently should CHECK AGAIN.
This is a newly disclosed vulnerability requiring another update.
🚨 CISA FLAGS NEW CITRIX NETSCALER ZERO-DAY AS ACTIVELY EXPLOITED
Citrix has released emergency patches for a new vulnerability being exploited against NetScaler appliances:
The vulnerability is a memory overflow affecting:
The appliance must be configured as either:
against unmitigated NetScaler deployments.
Repeated exploitation can potentially keep the service unavailable.
CISA's vulnerability intelligence now classifies exploitation as:
and the flaw has been added to the Known Exploited Vulnerabilities catalog.
Some early reporting suggested this vulnerability could allow unauthenticated remote code execution.
Citrix's official assessment lists the impact as denial of service, and Norway's NSM has now explicitly corrected its earlier RCE warning while noting that researchers continue investigating the discrepancy.
Organizations that patched NetScaler recently should CHECK AGAIN.
This is a newly disclosed vulnerability requiring another update.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
