 Back Escudodigital
Data leak exposes 40000 US Homeland Security employees, ICE agents and covert operations
The leak of information of more than 40,000 employees and contractors of the United States Department of Homeland Security (DHS) has opened a new front of concern for the security of its operations. The data, published online by the collective Distributed Denial of Secrets ( DDoSecrets ), includes information of immigration and border agents, investigators, cybersecurity personnel, and officials with responsibilities in sensitive areas, such as surveillance and undercover operations.
The DHS has acknowledged that it is aware of a 'possible breach' and is working to address the incident and protect its employees. The department assures that it will provide more information when it has new data. For now, it has not made public all the details the extent of the intrusion or the method used to obtain the records.
More than 21,000 records linked to border agents
The database, dubbed Icepick by those who have disseminated it, contains names, professional phone numbers, email addresses, job positions, office locations, and membership in internal groups. According to the data examined by TechCrunch , more than 21,000 records correspond to employees of the Customs and Border Protection (CBP), while another 10,000 are related to the Immigration and Customs Enforcement (ICE) and its Homeland Security Investigations (HSI) unit.
The leak also includes nearly a thousand records linked to the Cybersecurity and Infrastructure Security Agency (CISA) , in addition to personnel from other department dependencies. Altogether, the volume is equivalent to approximately one-fifth of a workforce of 220,000 workers.
The risk goes beyond publishing names
The main concern from a security standpoint is that the data does not constitute merely an employee directory. Information positions, assignments, and internal groups can help reconstruct part of the DHS's organizational structure and identify which workers have access to certain applications or tools.
TechCrunch has found references to groups related to surveillance technologies and data analysis, as well as with facial recognition applications. Among the records are users associated with Penlink, a company that markets tools to collect and analyze information from phones, communications, and internet activity, and with Mobile Fortify, a facial recognition application used by immigration and border agents.
For an adversary, that combination of identities, functions, and permissions can be more useful than an isolated list of names : it facilitates selecting targets for impersonation campaigns, preparing phishing messages directed at specific employees, or trying to obtain additional information through social engineering.
Can it endanger undercover ICE agents?
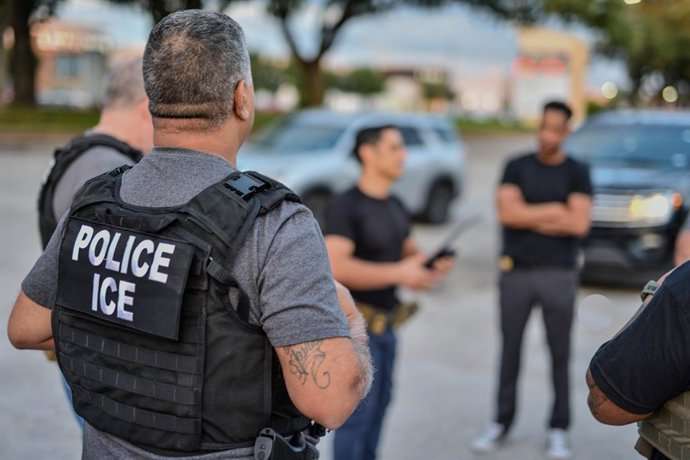
The leak also poses risks for agents involved in sensitive investigations . According to The Washington Post , the information allows identifying personnel linked to surveillance, forensic computing, and undercover operations tasks. The newspaper quotes John Sandweg, former acting director of ICE, who warned that the exposure of agents' identities could endanger both workers and their families and compromise investigations against criminal gangs and cartels.
The potential threat is not limited to a physical attack. With professional and organizational data, a third party can attempt to link identities with operations, destinations, colleagues, or technologies used. That information could serve to monitor certain agents, intimidate them, impersonate them, or try to identify their contacts and sources.
However, there is no public record that the leak has allowed identifying all the people working undercover, nor that it has already caused the failure of an operation or an attack against an agent. The risk derives from the exposed information and the uses that third parties can make of it, not from consequences that are substantiated so far.
The entry point remains unclear
The group claiming to have obtained the data says it accessed the information through the Okta single sign-on system used by the DHS. This type of platform allows employees to access different services and applications with the same digital identity.
However, this version has not been independently confirmed. Okta has stated that it has no evidence that its systems or data have been compromised. The published records appear to correspond to information extracted around mid-August.
The DDoSecrets collective has defended the dissemination as a tool to facilitate investigative journalism, public information requests, and parliamentary oversight. The group claiming to have obtained the data asserts that it intends to increase transparency the department's activities. These justifications do not eliminate, however, the risks that the publication may generate for employees who do not hold visible public positions and who participate in sensitive investigations.
The leak of information of more than 40,000 employees and contractors of the United States Department of Homeland Security (DHS) has opened a new front of concern for the security of its operations. The data, published online by the collective Distributed Denial of Secrets ( DDoSecrets ), includes information of immigration and border agents, investigators, cybersecurity personnel, and officials with responsibilities in sensitive areas, such as surveillance and undercover operations.
The DHS has acknowledged that it is aware of a 'possible breach' and is working to address the incident and protect its employees. The department assures that it will provide more information when it has new data. For now, it has not made public all the details the extent of the intrusion or the method used to obtain the records.
More than 21,000 records linked to border agents
The database, dubbed Icepick by those who have disseminated it, contains names, professional phone numbers, email addresses, job positions, office locations, and membership in internal groups. According to the data examined by TechCrunch , more than 21,000 records correspond to employees of the Customs and Border Protection (CBP), while another 10,000 are related to the Immigration and Customs Enforcement (ICE) and its Homeland Security Investigations (HSI) unit.
The leak also includes nearly a thousand records linked to the Cybersecurity and Infrastructure Security Agency (CISA) , in addition to personnel from other department dependencies. Altogether, the volume is equivalent to approximately one-fifth of a workforce of 220,000 workers.
The risk goes beyond publishing names
The main concern from a security standpoint is that the data does not constitute merely an employee directory. Information positions, assignments, and internal groups can help reconstruct part of the DHS's organizational structure and identify which workers have access to certain applications or tools.
TechCrunch has found references to groups related to surveillance technologies and data analysis, as well as with facial recognition applications. Among the records are users associated with Penlink, a company that markets tools to collect and analyze information from phones, communications, and internet activity, and with Mobile Fortify, a facial recognition application used by immigration and border agents.
For an adversary, that combination of identities, functions, and permissions can be more useful than an isolated list of names : it facilitates selecting targets for impersonation campaigns, preparing phishing messages directed at specific employees, or trying to obtain additional information through social engineering.
Can it endanger undercover ICE agents?
The leak also poses risks for agents involved in sensitive investigations . According to The Washington Post , the information allows identifying personnel linked to surveillance, forensic computing, and undercover operations tasks. The newspaper quotes John Sandweg, former acting director of ICE, who warned that the exposure of agents' identities could endanger both workers and their families and compromise investigations against criminal gangs and cartels.
The potential threat is not limited to a physical attack. With professional and organizational data, a third party can attempt to link identities with operations, destinations, colleagues, or technologies used. That information could serve to monitor certain agents, intimidate them, impersonate them, or try to identify their contacts and sources.
However, there is no public record that the leak has allowed identifying all the people working undercover, nor that it has already caused the failure of an operation or an attack against an agent. The risk derives from the exposed information and the uses that third parties can make of it, not from consequences that are substantiated so far.
The entry point remains unclear
The group claiming to have obtained the data says it accessed the information through the Okta single sign-on system used by the DHS. This type of platform allows employees to access different services and applications with the same digital identity.
However, this version has not been independently confirmed. Okta has stated that it has no evidence that its systems or data have been compromised. The published records appear to correspond to information extracted around mid-August.
The DDoSecrets collective has defended the dissemination as a tool to facilitate investigative journalism, public information requests, and parliamentary oversight. The group claiming to have obtained the data asserts that it intends to increase transparency the department's activities. These justifications do not eliminate, however, the risks that the publication may generate for employees who do not hold visible public positions and who participate in sensitive investigations.
Become a premium member for free!
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
