 Back Finance.Biggo
DOJ: North Korean Hackers Stole $400 Million in Crypto via Deepfake Video Calls
The U.S. Department of Justice said Thursday that North Korean hackers have stolen more than $400 million in cryptocurrency over the past 18 months by turning video conference calls into a trap, using secretly recorded footage and AI-generated deepfakes to win the confidence of crypto workers before delivering malware.
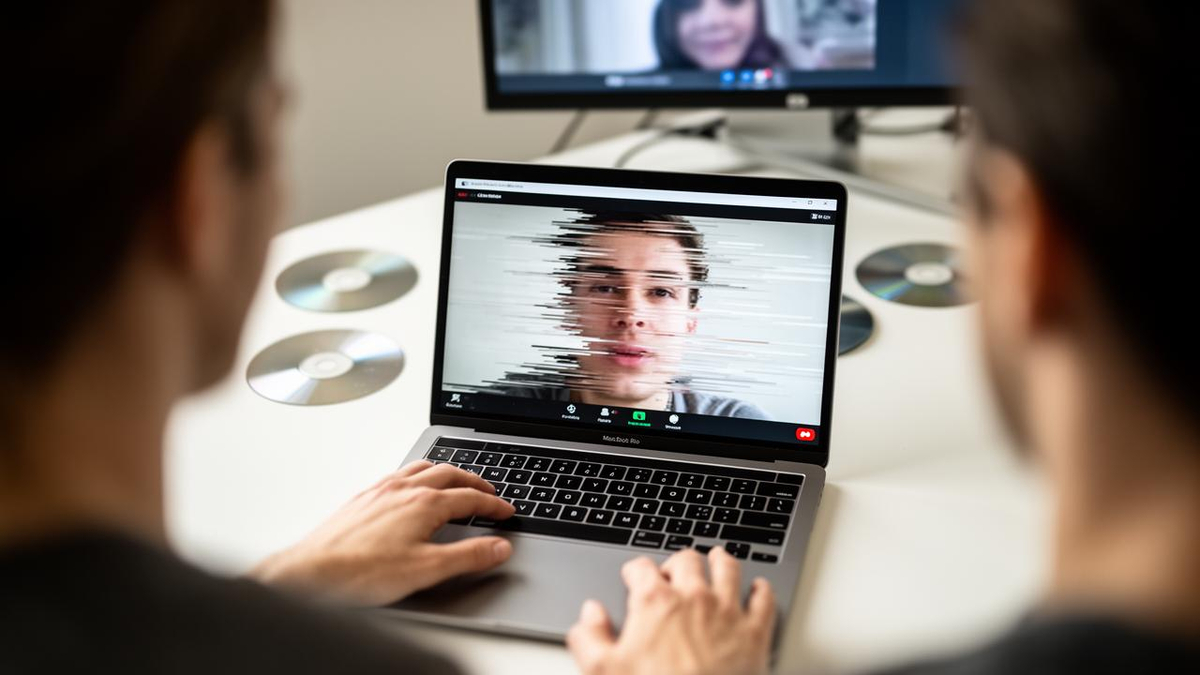
The FBI has named the social-engineering operation "FaceStealer." According to the department, the hackers open meetings using accounts hijacked from earlier victims, then play prerecorded webcam video of trusted contacts so that a familiar face appears to be on the other end of the line. The group also produces deepfake videos of well-known figures in the crypto industry to make the deception more convincing.
Once a target is at ease, the attackers stage a fake technical problem -- for instance, claiming they cannot hear the participant -- and offer a link to "fix" it. The link installs malware instead, giving the hackers a way to drain crypto wallets or exploit the victim's access to internal systems. Some intrusions went undiscovered for more than a year before the funds were moved, the department said.
Under a federal warrant, the FBI seized more than 900 webcam recordings of FaceStealer victims, an indication of how far the campaign reached.
The Justice Department linked the operation to North Korean groups tracked as Sapphire Sleet, BlueNoroff and APT38, among others. Officials warned that these teams have increasingly set their sights on open-source software developers, a shift that could open the door to supply-chain attacks across the crypto sector, in which compromised code libraries or dependencies are used to reach a wider set of victims.
The FaceStealer announcement came alongside an update on the record hack of Binance, one of the world's largest cryptocurrency exchanges. The department said it has obtained court authorization to seize or restrain more than $1.2 billion of the roughly $6.4 billion taken from the exchange on Oct. 29, part of a total of more than $2.7 billion in assets frozen so far.
Note: Figures as announced by the U.S. Department of Justice.
The FBI attributed the Binance theft to a North Korean-linked group known as TraderTraitor. Officials said the regime has moved the proceeds at speed, creating a new wallet roughly every 25 seconds to stay ahead of investigators.
North Korea has consistently rejected allegations of involvement and dismissed the FBI's attribution as a political provocation. Kim Yo Jong, the sister of North Korean leader Kim Jong Un, said in a statement carried by the state-run Korean Central News Agency: "It is a grave political provocation against the DPRK that the U.S. misleads the international public opinion as if all the cyber crimes in different parts of the world are our deeds."
The enforcement actions follow a series of U.S. sanctions aimed at North Korean IT workers accused of laundering cryptocurrency, and they underscore how central digital-asset theft has become to Pyongyang's finances. Researchers have documented a long list of methods the regime's hackers use to break into crypto firms.
For crypto companies and investors, the disclosures point to a threat that is hard to screen for: the attack does not rely on a software flaw but on a convincing human conversation. Firms that hire remote developers, conduct deal talks over video or rely on open-source components face the sharpest exposure, and the targeting of open-source maintainers raises the prospect that a single compromised project could ripple through many downstream platforms. Officials said efforts to trace and recover the remaining Binance funds are continuing.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
