 Back Businessupturn
From cargo delays to energy disruption: cyberattacks expose a weak link in US port security
US ports and shipping companies are facing a growing wave of cyber threats, with hackers targeting digital systems that coordinate cargo handling, vessel movements and commercial operations. The attacks and attempted intrusions, reported across major maritime hubs, are raising concerns that a successful breach could interrupt critical trade routes, delay shipments and affect energy exports.
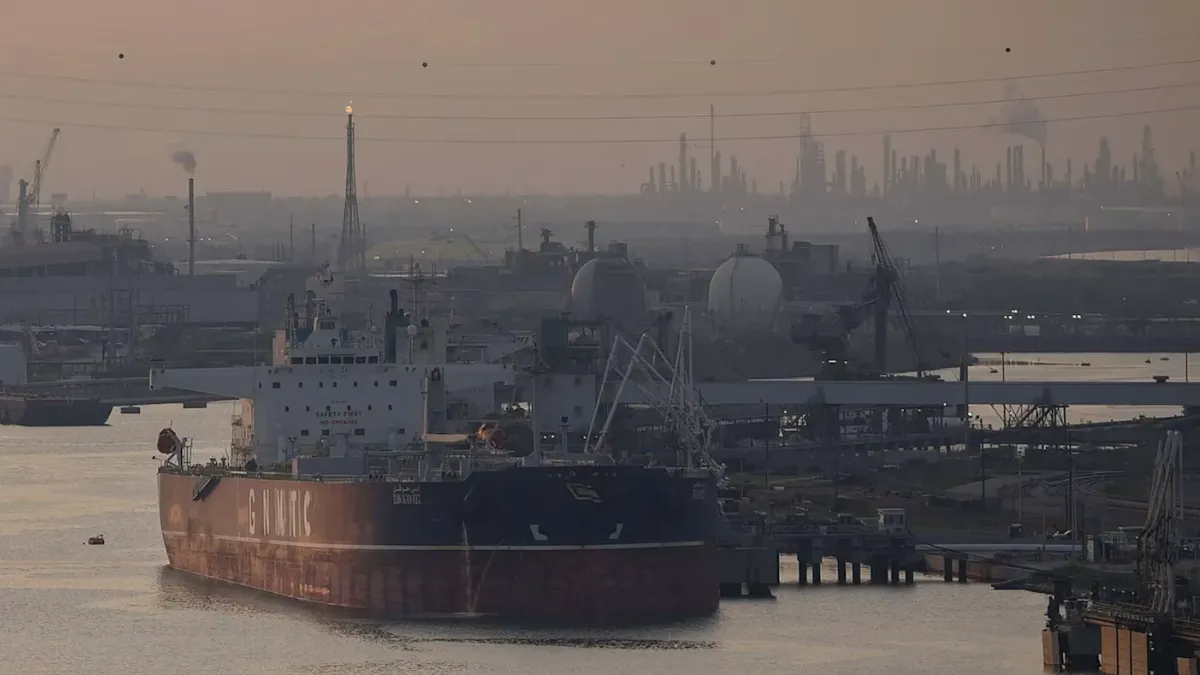
The Port of Corpus Christi in Texas, the country's leading crude oil export hub, has reported hundreds or even thousands of attempted cyber intrusions daily, according to a Financial Times report published on Sunday. Other incidents have affected port gate operations and shipping companies, illustrating how cyber risks can spread beyond data theft into the physical movement of goods.
The scale of the threat is reflected in figures from the US Coast Guard . Its 2025 Cyber Trends and Insights in the Marine Environment report recorded 42 reported cyber incidents across the maritime transportation system, up 17% from 36 in 2024. Phishing was used for reconnaissance or initial access in 43% of reported cases, compared with 25% a year earlier.
The Port of Los Angeles also faced a significant volume of attempted attacks. Its executive director, Gene Seroka, told Bloomberg that the port blocked more than 120 million cyberattack attempts in August. The attempts included network exploitation, credential theft and malware activity, according to the report. The figure represents blocked attempts, not confirmed successful breaches.
The risks extend to shipping companies. The Coast Guard's April 2026 maritime cyber alert warned that the INC Ransom group had demonstrated the ability to target maritime transportation networks through phishing and unpatched internet-facing systems. The agency said the group used data theft and encryption to pressure victims into paying ransoms.
The vulnerability is particularly serious because modern ports rely on connected terminal operating systems to manage cargo schedules, equipment, documentation and communications . The Coast Guard has warned that disruption to these systems can slow cargo operations and create wider transport bottlenecks.
Washington has begun strengthening safeguards. Coast Guard cybersecurity regulations that took effect on July 16, 2025, require covered vessels and facilities to maintain cybersecurity plans, designate cybersecurity officers and report relevant incidents. The first annual cybersecurity assessments and plan submissions are due by July 16, 2027.
The immediate challenge is ensuring that ports can continue operating even when digital systems are compromised. As US authorities and operators expand monitoring, reporting and security requirements, the test will be whether those measures can prevent attempted intrusions from becoming disruptions to cargo flows, shipping schedules and energy supply chains.
