 Back Gbhackers
Hackers Exploit ChatGPT and Claude Website Typos to Deliver Malware and Hijack Browsers
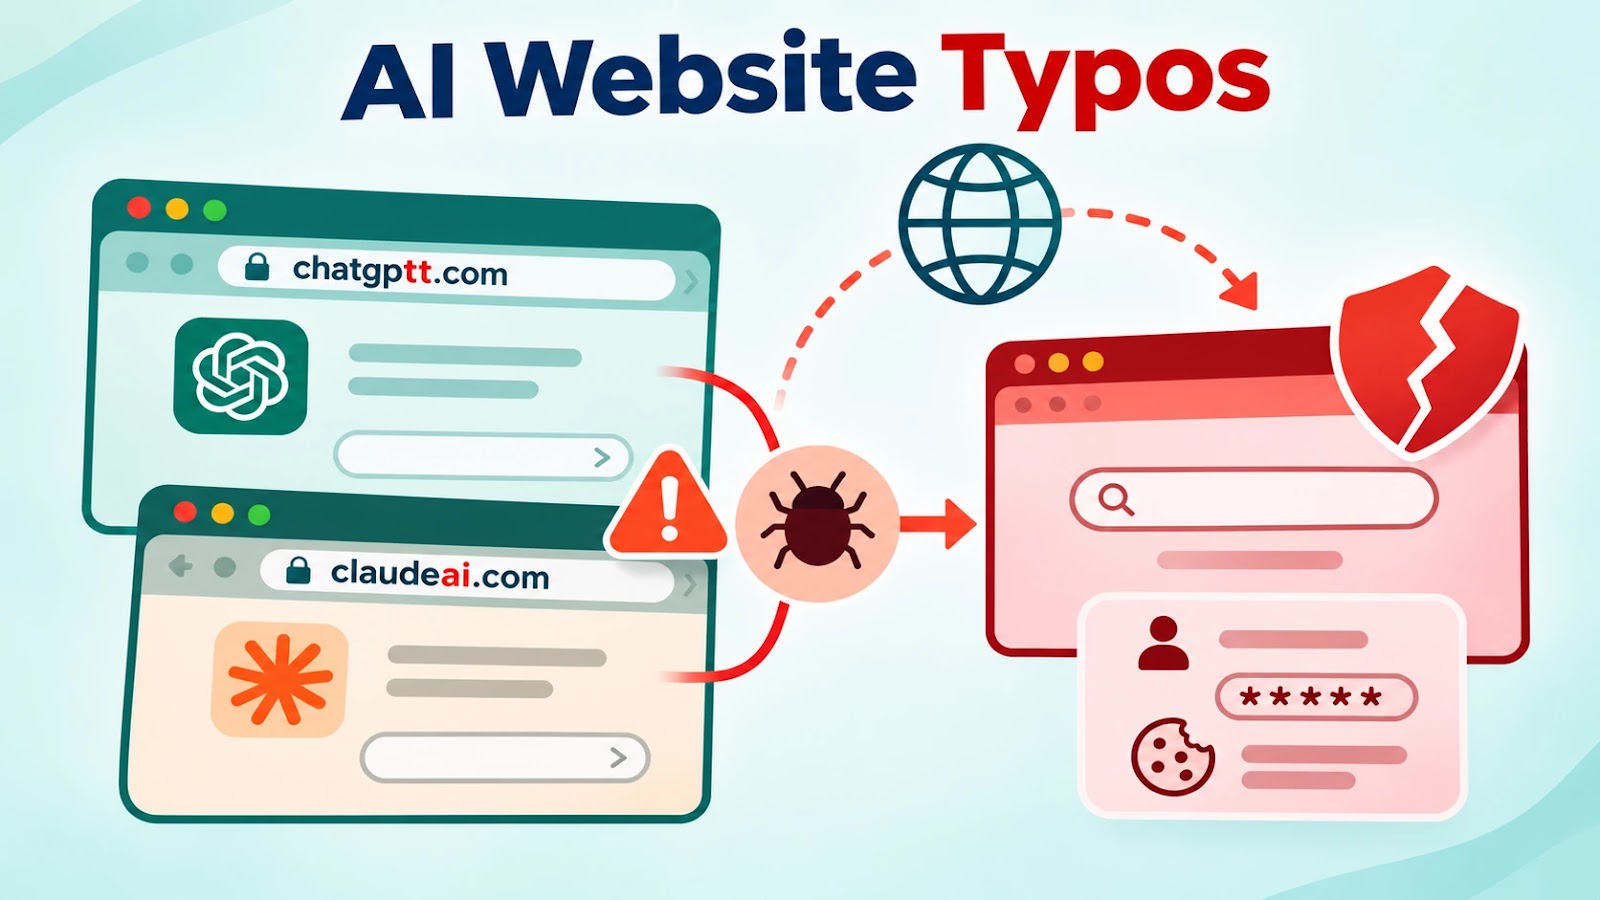
Oleg Zaytsev traced 186 lookalike domains across 27 AI brands, including Claude, ChatGPT, DeepSeek, Perplexity, Midjourney, ElevenLabs and Cursor.
He named the delivery pattern TypoPrompting. Ordinary typing errors led visitors to ClickFix lures , browser-hijacking malware and -hijacking extensions.
ChatGPT drew the most lookalikes with 25, followed by Claude with 18 and DeepSeek with 16. The slips are mundane: an adjacent-key hit in clsude[.]ai, swapped letters in cluade[.]ai, and a dropped letter in caude[.]ai.
A parked page passes the visitor to a traffic distribution system. That system chooses a destination based on location, operating system and browser, so one visitor sees a parked page and another gets an attack.
The technique is not new. Infoblox documented the same plumbing in December 2025. It found that visitors to parked domains were sent to scams or malware roughly 90 percent of the time, and that cloaking shows scanners a harmless page.
The cloude[.]ai typo redirects through securetrackingnode[.]com and biomimicrydevtech[.]buzz. It then reaches blockchainfuturedev[.]buzz, which fingerprints the browser and makes it solve an MD5 proof-of-work challenge.
Only selected visitors get a fake Cloudflare verification page in one of six languages. The page copies a command to the clipboard and tells the victim to paste it into the Windows Run dialog.
Island Researchers said that , the command uses curl.exe to download W901.ps1 from 3112851459, which is 185.138.88[.]3 written as a decimal number. It then runs the script in a hidden PowerShell window with an execution-policy bypass.
The decimal form leaves no dotted IP address for a pattern-based filter to match.
AI Website Typos Exploited
The same gate serves 211 entry domains, with 550 matching scan records from April 2025 to November 2026. Some imitate Scotiabank, Charles Schwab, Verizon and Microsoft Azure.
macOS visitors get a fake Terminal update that pipes curl output into zsh.
Eight typos of Claude, DeepSeek, Copilot, ElevenLabs and Voice AI led through deezyj[.]com to fake “Security Check” pages.
These pages delivered Net Guard, a Wi-Fi and DNS scanner. Its MSIX package matches the hash of the Microsoft Store listing and carries Microsoft’s signature. Inside is a Tauri application built on buntai-sdk.
The code can change the default engine while the user is idle. It can also run remote JavaScript through DevTools Runtime.evaluate and install extensions.
These features are enabled by default. Privacy Keeper and MyFlixly Browser the same code, and Island classifies all three packages as browser hijackers.
A Perplexity typo, preplexity[.]ai, led to quickflashtool[.]com and a Chrome extension access that sets find.flashysearches[.]com as the provider.
The extension requests no permissions and runs no JavaScript. It is one of 30 from a shared kit. Thirteen have been removed, and the 17 still listed showed 972,000 users on November 3.
Some typos deliver payloads directly. In October and November 2026, chatlgpt[.]com offered Installer_ChatGPT.zip, which 9 of 16 MetaDefender engines flagged.
In 2023, midj0urney[.]org served Aurora stealer through the Invalid Printer loader. In early 2025, deepsek[.]icu served an Android package.
Island recommends managed bookmarks for sanctioned AI tools and monitoring for lookalikes of those tools.
It also advises correlating browsing with Run-dialog activity and flagging hidden PowerShell, bypass flags and decimal IPs.
Defenders should judge MSIX files by package family, publisher and hash, because a Store signature does not describe browser behavior.
They should also enforce central and extension policy, and hunt the full chain from entry domain to endpoint change.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC .
Artificial Intelligence
Cyber security Course
Cyber Security Resources
Cybersecurity
Information Gathering
Information Security Risks
Hackers Manipulate NVIDIA GPU Monitoring to Conceal Cryptocurrency Mining on Compromised Linux Servers
FBI Disrupts North Korean FaceStealer Attacks Linked to $400 Million in Crypto Theft
Hackers Hijack Microsoft SQL Servers Using T-SQL Commands to Install Gh0st RAT and Crypto Miners
Hackers Disguise XLoader Malware as Purchase Order Confirmations to Infect Windows Computers
Hackers Exploit Check Point PHP2Shell Flaws to Gain Root Access and Deploy Wiper Malware
OpenAI Launches Advanced AI Cybersecurity Tools for Automated Penetration Testing and Vulnerability Research
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
