 Back Gbhackers
Hackers Implant Stealthy BPFdoor Backdoors in Telecom Networks for Persistent Access
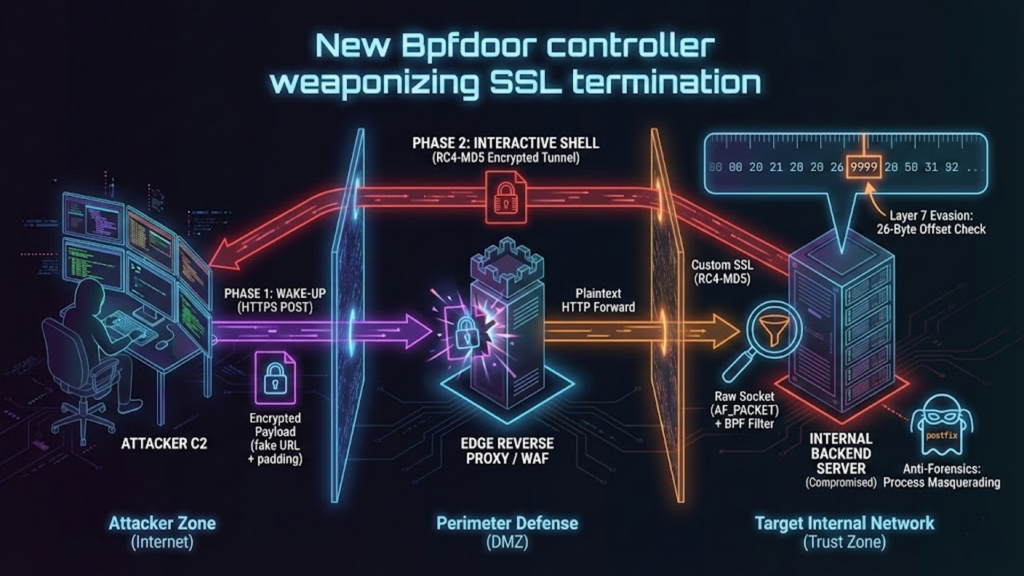
A China-nexus threat actor known as Red Menshen is planting stealthy backdoors deep inside global telecommunications networks. According to a recent investigation by Rapid7 Labs, this long-term espionage campaign utilises a highly evasive Linux kernel malware called BPFdoor. Instead of launching noisy, disruptive attacks, these hackers are building dormant sleeper cells in the telecom backbone. […]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
