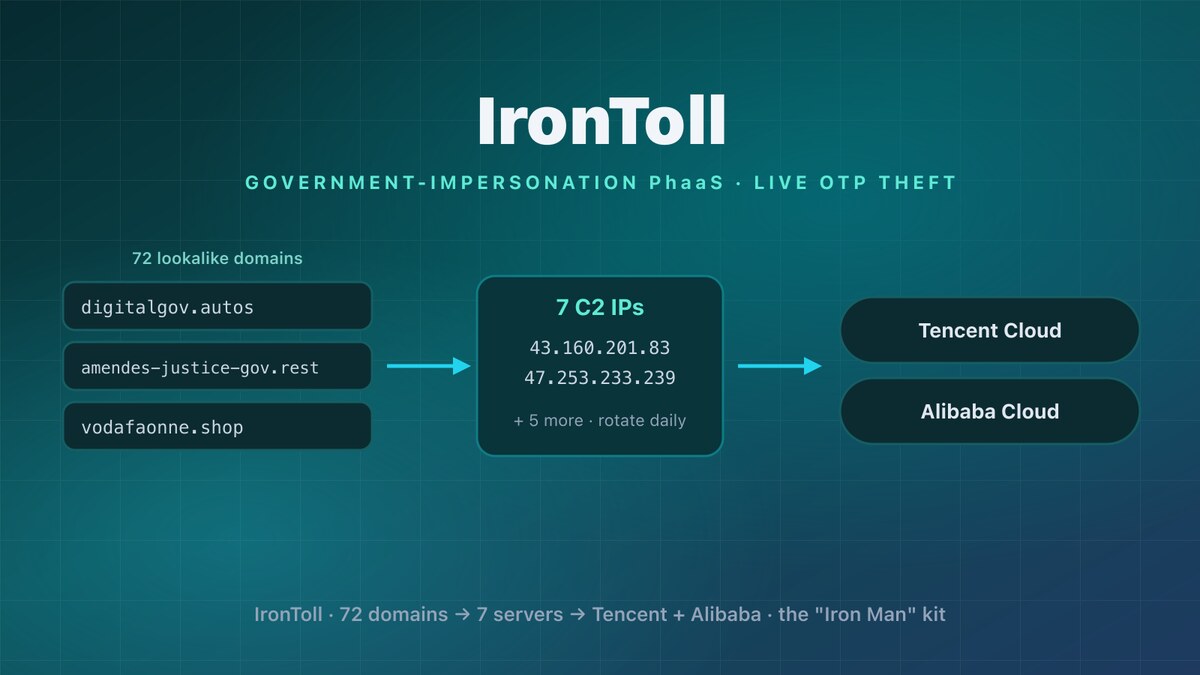
TL;DR — Starting from one live phishing URL, PhishEye threat research mapped IronToll , a phishing-as-a-service (PhaaS) campaign of 90+ domains across 10+ countries and 15+ brands . It impersonates national e-government portals, tax authorities, traffic and parking fines, telecom operators, and parcel couriers to steal credentials, card data, and one-time passwords (OTPs) in real time . Every domain traces back to a small cluster of 7 Tencent/Alibaba C2 IPs and the commercial Chinese phishing kit that brands itself "Iron Man System" (钢铁侠) . This post documents the full IOC set and the passive-DNS hunting method that unravelled it.
TL;DR — Starting from one live phishing URL, PhishEye threat research mapped IronToll , a phishing-as-a-service (PhaaS) campaign of 90+ domains across 10+ countries and 15+ brands . It impersonates national e-government portals, tax authorities, traffic and parking fines, telecom operators, and parcel couriers to steal credentials, card data, and one-time passwords (OTPs) in real time . Every domain traces back to a small cluster of 7 Tencent/Alibaba C2 IPs and the commercial Chinese phishing kit that brands itself "Iron Man System" (钢铁侠) . This post documents the full IOC set and the passive-DNS hunting method that unravelled it.
this research. The findings below come from first-hand threat hunting by the PhishEye anti-phishing team: we started from one live URL and independently verified the campaign's live domains and command-and-control (C2) IPs by DNS resolution and passive-DNS pivoting on 4 July 2026 . Kit-level details we did not observe directly are attributed to their original sources. See Methodology & verification and Related research & references .
this research. The findings below come from first-hand threat hunting by the PhishEye anti-phishing team: we started from one live URL and independently verified the campaign's live domains and command-and-control (C2) IPs by DNS resolution and passive-DNS pivoting on 4 July 2026 . Kit-level details we did not observe directly are attributed to their original sources. See Methodology & verification and Related research & references .
IronToll is the name PhishEye assigns to a sprawling phishing-as-a-service (PhaaS) operation that weaponises a commercial Chinese phishing kit — self-branded "Iron Man System" — to run government and brand impersonation at industrial scale. The campaign's common denominator is an urgent payment demand : an unpaid traffic fine, a parking penalty, a tax bill, a customs charge, or a parcel "redelivery fee." Victims are funnelled to a pixel-perfect clone of a real government or brand portal, where a live operator intercepts credentials, card details, and OTPs as they are typed — defeating SMS two-factor authentication in real time.
We first encountered IronToll through a single live URL, ekosova.gov-eg.my.id/eg , a fake "Digital Egypt" traffic-fine page. Public research by security researcher secfathy0x1 had already dissected the Egyptian cluster and the underlying "Iron Man System" kit. Pivoting on its infrastructure, we found the Egypt operation was one country in a much larger machine .
The lure: fake fines, taxes, and delivery fees
IronToll's psychology is consistent everywhere: a small, time-pressured payment you don't want to ignore. Across the clusters we mapped, the impersonated services include (each brand below is inferred from domain naming and lure context, not confirmed against a captured page):
National e-government portals — Egypt ("Digital Egypt"), Serbia ("eUprava"), and generic at-govt gateways.
Tax authorities — Spain's Agencia Tributaria.
Traffic, parking, and road-police fines — Morocco/France justice-fine portals, UK parking operators APCOA and Q-Park , and generic "road police / transport authority" fine pages.
Telecom operators — Vodafone, Australia's Telstra, Botswana's Orange.
Parcel couriers ("redelivery fee" scams) — DHL, DPD, Evri, GLS, and Chronopost.
Law enforcement — Ukraine's National Police (NPU).
Each lure is localised (language, currency, logo, even the cited legal statute, since the Egyptian pages quote Traffic Law №66 of 1973 ), which is exactly what a rented PhaaS kit makes cheap to do.
Where IronToll fits: the Chinese PhaaS family tree
"Iron Man System" is not a wholly new phenomenon; it is one branch of the Chinese-language, live-interception phishing-as-a-service ecosystem that multiple vendors have tracked for over a year. It is best understood as a sibling of the "Mouse System" / "Magic Mouse" (Haozi) kit family and part of the loosely federated Smishing Triad ecosystem alongside Darcula, Lighthouse, Panda Shop, Phoenix, YYlaiyu, and Xiū gǒu (Xinxin Group) .
The overlap with published research is concrete, not theoretical:
The APCOA / Q-Park parking-fine cluster we mapped ( apcoatfine.cfd , q-parkfine.cfd , …) is the same activity D3Lab attributes to the "Mouse System" kit in its June 2026 analysis of APCOA Flow smishing ( D3Lab ).
The Serbian euprava-gov.* e-government cluster matches Group-IB's "Fake Traffic Fines" Balkans campaign, which it links to Darcula and Phoenix ( Group-IB ).
The real-time OTP interception design is the defining shift Google's Threat Intelligence Group and others describe across this whole ecosystem — away from static credential harvesting toward live tokenization that neutralises SMS MFA ( Google Threat Intelligence Group ).
We use IronToll as a campaign tracker for the specific infrastructure and brand set documented here; it should be read as a slice of the broader Mouse/Haozi/Smishing-Triad PhaaS market , not a claim of a brand-new toolkit. The Related research section maps the connective tissue.
From one domain to a campaign: the hunt
The breakthrough was not the domain name — it was the shared hosting infrastructure . Because IronToll pins its sites to a handful of Chinese-cloud IPs, any domain that resolves there is part of the campaign, regardless of brand or top-level domain. Our loop:
Resolve the seed domain → it pointed to 47.253.233.239 (Alibaba Cloud), one of the IPs named in the original research.
Passive DNS on that IP (AlienVault OTX) → dozens of sibling domains and new C2 IPs.
Resolve the new domains → they revealed more IPs across the same Tencent/Alibaba cluster (the seed sat on Alibaba; most sibling C2 resolved into Tencent space).
Repeat until the set converges.
We combined this with two supporting techniques:
Pattern × TLD brute-force: generate {brand-prefix}.{disposable-tld} combinations for observed prefixes ( digitalgov , vodafaonne , at-govt , …), resolve them, and keep only those landing on a known C2 IP. This catches day-0 domains before any scanner indexes them .
Newly-registered-domain (NRD) grep: scan daily NRD feeds for campaign tokens, then confirm by resolution. This surfaced fresh registrations like malowzx.sbs and the at-govt cluster.
Certificate Transparency (crt.sh) would normally be the ideal SSL-based early-warning signal — IronToll domains always obtain a Let's Encrypt certificate — but crt.sh's backend was unavailable during our research, underscoring why defenders should not rely on a single source.
Command-and-control infrastructure
As of our 4 July 2026 snapshot , every confirmed IronToll site resolved directly to Chinese cloud providers (Tencent/Alibaba), with no Cloudflare proxy in front . That keeps the origin network visible, so host-level abuse reports can target it directly, unlike Cloudflare-fronted kits where the origin is hidden. We confirmed seven live C2 IPs:
Registrars: predominantly NameSilo (nameservers ns[1-3].dnsowl.com ) with some NameMart ( domainnamens.com ). Domains are privacy-protected, DNSSEC-unsigned, have no MX records, and are registered in same-day batches — a classic disposable-infrastructure signature.
The "Iron Man System" phishing kit fingerprint
The following kit-level indicators are drawn from the original secfathy0x1 research and are content-level tells that identify any IronToll deployment, brand-agnostically:
Self-brand: "Iron Man System" (钢铁侠) v6.0.0; favicon iron-man.png ; a serverConfig.json whose title field reads Iron Man System .
Frontend: Vue 3 + Element-Plus single-page app; assets /assets/index-39cef7f8.js and /assets/index-f18ae053.css ; landing-page ETag 33746b336ed5dd450a5542c5d7ce4e55 .
Backend headers: server: GoFrame HTTP Server and via: 1.1 Caddy ; Let's Encrypt TLS with an atypical issuer CN ( YE1 ), which is not a standard Let's Encrypt intermediate and should be confirmed against a captured certificate.
Live interception: captured card/OTP data is relayed to operators in real time over an AES-encrypted WebSocket , which is how the kit defeats SMS OTP before the victim finishes typing.
Cloaking: mobile-only rendering, country gating, and IP-intelligence filtering (via ipregistry ) return HTTP 404 to datacenter/VPN and desktop visitors — which is why sandboxes often see nothing.
URL paths: country-coded lure paths ( /eg , /ma ), obfuscated per-deployment admin panels ( /{random}/admin/ ), and a template artifact /we003_si_etc_gov/ that appears to derive from a cloned Slovenian gov.si template (inferred from the path, not confirmed).
Indicators of Compromise (IOCs)
Copy-paste block for detection engineering. Live status verified 2026-07-04; the campaign rotates domains every 1–2 days, so treat the IP set and kit fingerprints as the durable indicators .
Copy-paste block for detection engineering. Live status verified 2026-07-04; the campaign rotates domains every 1–2 days, so treat the IP set and kit fingerprints as the durable indicators .
Command-and-control IPs — the durable indicator; block these first:
Representative live domains (73 shown, grouped by lure) — the disposable, rotating layer:
Kit tells: favicon iron-man.png · ETag 33746b336ed5dd450a5542c5d7ce4e55 · JS index-39cef7f8.js · headers GoFrame + Caddy .
Disposable TLDs seen across these IOCs: .autos .bar .biz .boats .bond .buzz .casa .cfd .courses .cyou .fit .forum .fun .hair .help .homes .icu .lat .life .my.id .pics .reisen .rest .sbs .shop .skin .work .xyz .
How defenders can hunt IronToll themselves
Pivot on the C2 IPs, not the brand. Query passive DNS (OTX, VirusTotal, SecurityTrails) for every hostname seen on the seven IPs above; re-resolve results to discover new sibling IPs.
Watch Certificate Transparency for the disposable-TLD + brand-token combinations, and for Let's Encrypt certs on those IPs.
Alert on the kit fingerprint — the ETag, favicon hash, or GoFrame + Caddy header combo will flag new deployments regardless of the domain name.
Mine daily NRD feeds for campaign tokens ( digitalgov , amendes , vodafaon , at-govt , apcoa , finess… ) and confirm by resolution.
Automate the loop. Manual hunting converges quickly; a scheduled job that re-runs passive-DNS + brute-force + NRD/CT checks catches the rotation on day one.
Because the confirmed IronToll origins resolved directly to Tencent and Alibaba, with no Cloudflare proxy masking them, abuse reports can target the real hosting network directly (though these providers' international abuse desks are not always fast):
Hosting abuse: report the offending IP directly to Tencent Cloud ( 43.x ) and Alibaba Cloud ( 47.x ) abuse desks; the responsible network's abuse is discoverable via IP-RDAP.
Registrar abuse: the majority sit at NameSilo , whose phishing-report process is well-defined and automatable.
Registry escalation: the .my.id domains fall to the Indonesian registry (PANDI).
Reporting to both the host and the registrar in parallel gives the fastest result.
Methodology & verification
Transparency how we reached these conclusions:
What we verified ourselves (4 July 2026): every C2 IP and every "live" domain in this post was confirmed by direct DNS A -record resolution , and the domain set was expanded by passive-DNS pivoting (AlienVault OTX) on the C2 IPs plus pattern × TLD resolution filtered to those IPs. Hosting attribution (Tencent AS132203 / Alibaba AS45102) is from the resolved IPs' network ownership.
What we attribute to prior research: the kit-internal details — the "Iron Man System" self-branding, favicon, ETag, JavaScript asset hashes, GoFrame / Caddy stack, WebSocket interception design, and cloaking logic — are drawn from secfathy0x1's original analysis . We did not re-execute the live kit, because it harvests real victim data.
Limitations: domains rotate every 1–2 days, so "live" reflects a point-in-time snapshot; treat the IPs and kit fingerprints as the durable indicators . Brand attributions (e.g. "Telstra", "APCOA") are inferred from domain naming and lure context and should be confirmed against a captured page before enforcement.
Ethics & responsible handling: we did not interact with victim-facing forms or submit data. Abuse reports go to the hosting providers and registrars named above. Nothing in this post enables the operation; it enables its detection and takedown.
IronToll sits within a well-documented ecosystem. These vendor and independent analyses cover the same kit family, tactics, or overlapping infrastructure:
Directly overlapping kit / brands
D3Lab — APCOA Flow smishing → "Mouse System" kit (matches our APCOA/Q-Park cluster):
Group-IB — Phishing in the Balkans: Fake Traffic Fines (Serbia e-gov = our euprava-gov cluster; links Darcula + Phoenix):
secfathy0x1 — Inside a Live Digital Egypt Traffic-Fine Phishing Campaign (the seed research on "Iron Man System"):
Chinese live-interception PhaaS ecosystem
Group-IB — Phoenix Rising: the PhaaS kit behind global smishing :
SpyCloud — Analyzing the YYlaiyu PhaaS Panel :
Google Threat Intelligence Group (GTIG) — The Evolution of Chinese-Language Phishing Services :
Palo Alto Networks Unit 42 — The Smishing Deluge: China-Based Campaign :
Resecurity — Panda Shop Chinese Carding Syndicate :
Infosecurity Magazine — Chinese Threat Actors Shift to Live Credential Interception :
Krebs on Security — Chinese Innovations Spawn Wave of Toll Phishing via SMS : · Smishing Triad Pivots to Banks :
Microsoft — Egypt-based cybercriminal supplier's websites seized (the separate ONNX phishing-kit takedown; adjacent context, not the Iron Man / Mouse / Haozi family):
Live-interception / AiTM kit context
Microsoft — Inside Tycoon2FA :
Sekoia — Global analysis of Adversary-in-the-Middle phishing threats :
What is the "Iron Man System" phishing kit? A commercial, licensed Chinese phishing-as-a-service kit (self-branded "Iron Man System" / 钢铁侠) that provides live credential and OTP interception, mobile cloaking, and per-deployment operator dashboards. IronToll is a campaign that uses this kit.
Is IronToll only targeting Egypt? No. Egypt ("Digital Egypt") is one cluster. We confirmed impersonation of services in Morocco, France, Serbia, Ukraine, Spain, Australia, Botswana, Thailand, Austria, Turkey, and the UK, plus global courier and telecom brands.
How does it bypass two-factor authentication? It relays the victim's session to a human operator in real time over an encrypted WebSocket. When the victim enters an SMS OTP, the operator immediately replays it on the real service — so static 2FA offers little protection. Phishing-resistant methods (passkeys/FIDO2) do.
Why didn't my sandbox see the phishing page? The kit is mobile-only and country-gated, and uses IP-intelligence cloaking to serve HTTP 404 to datacenter, VPN, and desktop visitors. Analyse it from a mobile-emulated, in-region client, or rely on the stored artifacts in services like urlscan.io.
What are the most durable indicators to block? The seven C2 IPs and the kit fingerprints (ETag 33746b336ed5dd450a5542c5d7ce4e55 , favicon iron-man.png , GoFrame + Caddy headers). Individual domains rotate every 1–2 days.
PhishEye Threat Research is the anti-phishing and digital-risk-protection team behind PhishEye, a platform for typosquat/impersonation monitoring and automated takedown. Our analysts run daily threat-hunting across passive DNS, Certificate Transparency, and newly-registered-domain feeds, and operate the abuse-reporting pipeline that files takedowns with hosts and registrars. This report reflects hands-on investigation of live IronToll infrastructure, not a literature review.
Have a correction, an additional IOC, or want a domain investigated? the team at [email protected] . We update this page as the campaign rotates.
Naming note: we track this campaign as IronToll — a slice of the broader Mouse System / Haozi / Smishing-Triad Chinese PhaaS ecosystem, not a claim of a new toolkit. Working alternatives considered: IronGov, GhostFine, IronHerald. "IronToll" captures the core — an urgent, fraudulent payment demand (a "toll") delivered by the "Iron Man System" kit.
Research credit: initial Egyptian-cluster and "Iron Man System" kit analysis by secfathy0x1 ; overlapping kit/brand attribution by D3Lab and Group-IB . Infrastructure expansion, multi-country mapping, and live IOC verification by PhishEye Threat Research.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
