(The Center Square) - U.S. officials disrupted a plot by Chinese hackers to infiltrate online systems at several high level executive agencies.
The U.S Justice Department found a state- group associated with the People's Republic of China was responsible for targeting sensitive networks and critical infrastructure at NASA, the U.S. Department of Health and Human Services, the National Institutes of Health, Departement of Energy, Department of Justice, the Federal Reserve and the U.S. Senate.
“State- malicious hackers preying on America’s critical infrastructure will be stopped and prosecuted. We are here to ensure security for the American people and will use every tool we have to keep that promise,” said Attorney General Todd Blanche.
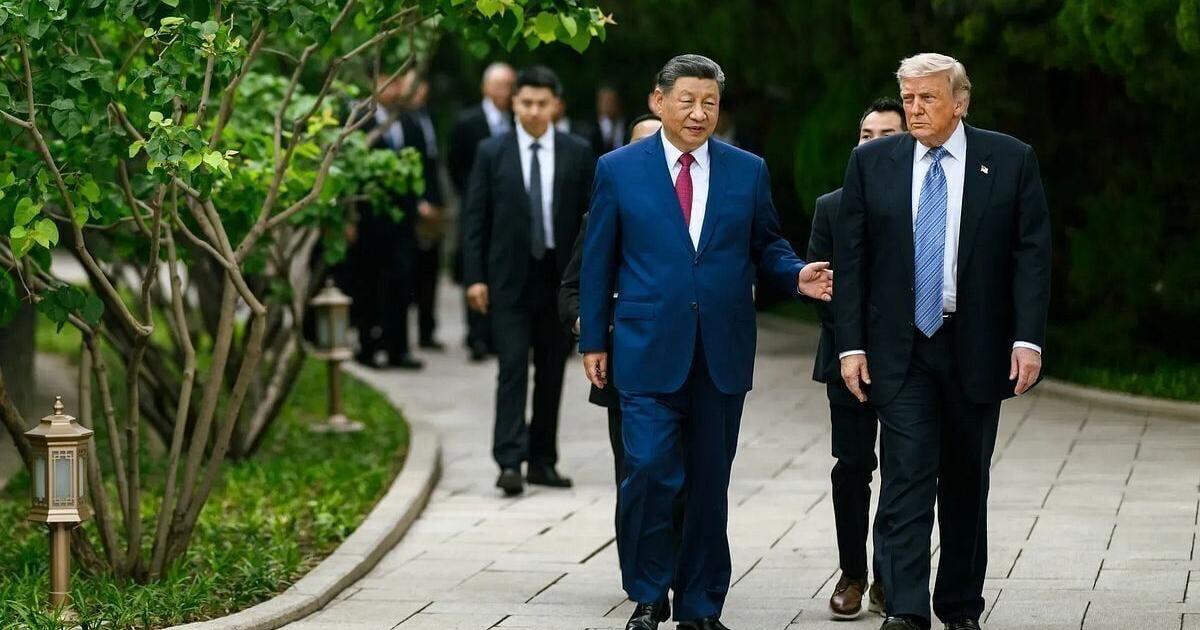
The Justice Department did not detail the extent of damage or security infiltration at the agencies. The announcement comes as Chinese President Xi Jinping is set to visit President Donald Trump in the Washington, D.C. in September.
The state- group behind the hacking incident, known as "QTFY," was employed by Nanjing Xinjiuwei Network Technology Company, a China-based company. According to court documents, QTFY offers hacking services to paying customers, including China's Ministry of State Security and People's Liberation Army
The hacking platforms, known as "QScan" and "QRouter," were used to target infrastructure throughout the various agencies. QScan will scan and automatically infect thousands of "internet-of-things" devices worldwide, which are then added to the QTRouter network, according to court documents.
QTRouter then works to conceal the identity of China-linked computers to hide the hacking activity. In some cases, QTRouter makes it appear as if hacking activity is local to a targeted agency's network.
“Through complex investigations, aggressive technical operations, and strong partnerships, FBI San Diego will continue to identify, disrupt, and impose costs on our cyber adversaries," said Mark Remily, special agent in charge of the FBI San Diego field office.
The hacking incident follows several others associated with China over the last few years. In 2025, the FBI removed surveillance malware from more than 4,000 U.S. computers after it had been infected by China-linked hacker group Mustang Panda.
In 2023 and 2024, the FBI disrupted two botnets consisting of hundreds of thousands of devices linked to China- hacking groups.
"We are committed to dismantling the tools behind these state- crimes and protecting the American people from malicious cyber activity," Remily said.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
