 Back Mt.Co.Kr
Mirae Asset Securities also breached… Possibility of sanctions against CEO over data ... - 머니투데이
As Mirae Asset Securities, the top player in the financial investment industry, suffered a breach incident resulting in the leakage of account numbers for approximately 3,800 customers, attention is focused on the level of sanctions from financial regulators. This is because the amendment to the Financial Company Governance Act has established a legal basis to hold CEOs accountable for security breach incidents. The key factors are expected to be how severe the consequences of the incident were and whether the CEO fulfilled their duty of care sufficiently to prevent it.
According to financial regulators and the financial investment industry on the 8th, regulators have begun on-site inspections of securities firms where breach incidents occurred, including Daishin Securities and Mirae Asset Management. It is also known that the Financial Supervisory Service will conduct an on-site inspection of Mirae Asset Securities, which announced the account number leak incident for approximately 3,800 customers on the 6th, starting from the 9th. When a breach incident occurs, the IT Inspection Bureau of the Financial Supervisory Service and the respective company's responsible inspection bureau jointly conduct on-site inspections; if there are indications of regulatory violations, the process is converted into a formal examination to continue additional investigations.
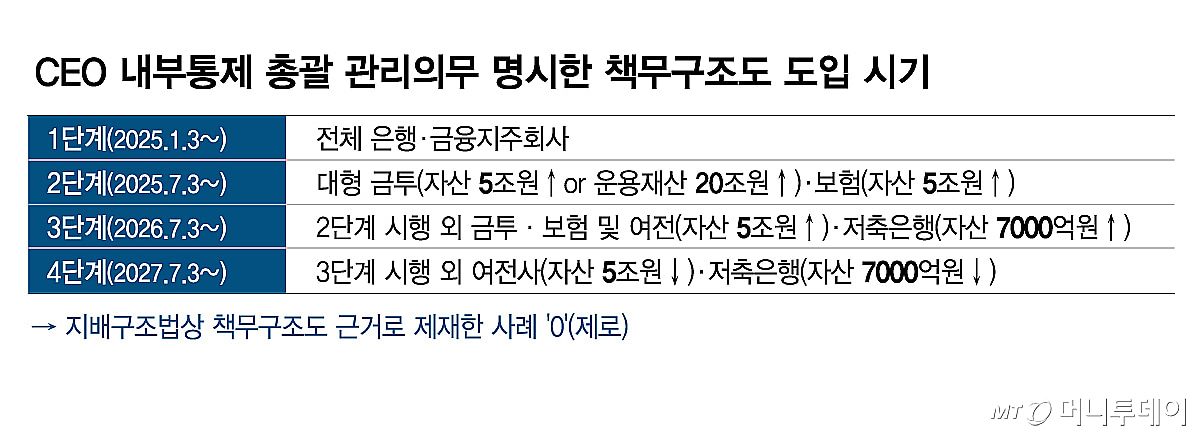
In the case of this hacking breach incident, it is predicted that CEO liability may be pursued, unlike typical MTS (Mobile Trading System) computer system failure incidents. Large securities firms with assets of 5 trillion won (assets under management of 20 trillion won) or more have been implementing the accountability structure diagram, which includes the CEO's overall management obligation for internal controls, since July last year.
In particular, breach incidents at securities firms such as Daishin Securities, Hanyang Securities, and Mirae Asset Securities occurred with intervals of at least several weeks after the Shinhan Bank breach incident was confirmed on September 30. During this period, financial regulators and the Financial Security Institute repeatedly requested securities firms to check for security vulnerabilities and update patches, leading to analysis that the responsibility of securities firms where incidents surfaced late is not light.
If financial regulators apply the Financial Company Governance Act in handling this breach incident, the level of CEO liability is expected to hinge on "severity of outcome" and "adequacy of duty of care" regarding whether sanctions will be imposed.
When introducing the accountability structure diagram, financial regulators presented a total of eight detailed judgment criteria, reflecting opinions from financial companies that "sanction standards are unclear." When judging the degree and results of illegal acts, they comprehensively consider factors such as △failure to fulfill management obligations, △raising issues regarding the possibility of illegal acts occurring, △occurrence of large-scale customer damage, and △damage to trust and order in the financial market, to determine whether the case is severe, ordinary, or minor.
How much due care the CEO exercised to prevent the breach incident is also an important consideration in the sanction process. Financial regulators stated that they would judge CEO liability based on criteria such as △whether executives could have predicted the results of illegal acts (incidents) (predictability) and △whether measures were taken to prevent them (result avoidance). Since the breach incidents at securities firms occurred after incidents at banks and savings banks, there is a possibility that strict standards will be applied in the predictability aspect.
Lotte Card, which experienced a breach incident involving the leakage of information for 2.97 million people on the 29th last year, before the introduction of the accountability structure diagram, had its CEO disciplined. At the time, financial regulators imposed a four-and-a-half-month business suspension and a 5 billion won surcharge on Lotte Card, and issued a "reprimand warning" to the CEO. The legal basis for sanctions at the time was the Credit Information Act, and there are points distinguishing it from this breach incident, such as the number of data leaks being 2.97 million cases.
Meanwhile, financial regulators have announced plans to strengthen IT security-related governance and introduce punitive surcharges. Financial regulators plan to prepare and implement a security internal control guideline in the first quarter of year. Additionally, they are pushing for amendments to the Electronic Financial Transactions Act (EFTA) that would impose punitive surcharges of up to 3% of total revenue when a breach incident occurs and strengthen CEO liability.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
