 Back Gbhackers
OPTIMJACK Attack Injects Malicious JavaScript Into CNN, Zoom and Other Major Websites to Steal Data
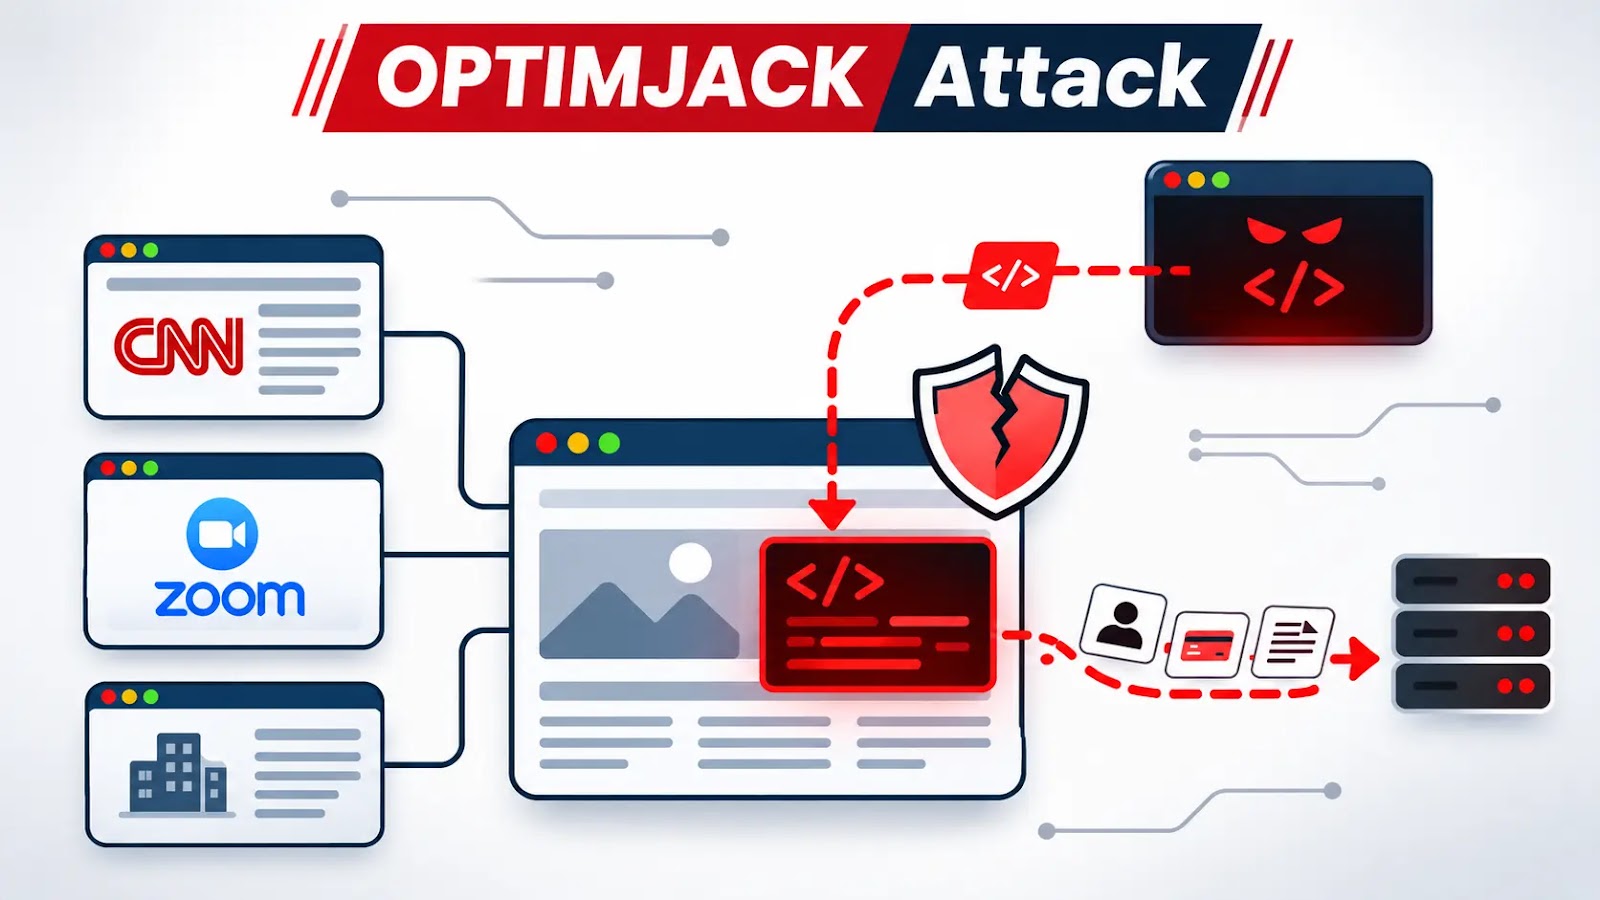
OPTIMJACK, a malicious JavaScript delivery campaign observed on CNN, Zoom, and other prominent websites through a third-party script layer.
Detected on November 16, the activity reportedly involved code designed to replace cryptocurrency wallet addresses , collect payment details, and selectively deliver additional content to iPhone and iPad browser profiles.
Successful financial theft and device exploitation remain unconfirmed.
The investigation began when Cynet endpoint detection and response alerts flagged browser connections to 1688360[.]cc.
CyOps analysts correlated those alerts with browsing activity, inspected associated resources and traced the loader to JavaScript served from cdn.optimizely[.]com.
Researchers assessed this third-party script layer as the likely injection point, without establishing how the insertion occurred.
Browser captures showed a resource loaded on edition.cnn[.]com appending 1688360[.]cc/track.js to the page.
On Zoom, investigators identified the same insertion code within an Optimizely-hosted script loaded alongside Zoom resources. They also captured the code while browsing Optimizely’s own website.
The investigation additionally listed Salesforce, Fox News and Fox Sports, but the report lacked request-and-response captures needed to verify those observations.
Their evidence status therefore differs from the captured CNN, Zoom and Optimizely cases. Delivery through these pages does not establish that the organizations’ internal systems were compromised.
Potential entry paths include compromised account access, tag configuration or an integration, but none has been confirmed.
Cynet explicitly cautioned against interpreting the findings as proof that Optimizely itself was breached.
Cynet Researchers documented , 1688360[.]cc/script.js and 1688360[.]cc/track.js. Available evidence does not establish whether these resources returned identical payloads or represented different revisions.
Analyst review described wallet-replacement functionality intended to substitute cryptocurrency addresses in page content or clipboard interactions.
Payment-form collection logic reportedly sought card details for transmission to an external destination. Neither capability, by itself, demonstrates a completed fraudulent transfer or successful collection from a visitor.
Other reported functions included collecting accessible cookies and page data, alongside using html2canvas to render page content.
These capabilities remain constrained by browser security boundaries: the evidence does not establish access to HttpOnly cookies, unrelated origins, other tabs or unrestricted desktop screenshots.
Using a Safari-like iPhone profile and device emulation, researchers retrieved boot.js from infrastructure including 5vobauua3ojpklx[.]icu and, during later retrievals, eil786npto9u5bq[.]icu.
The loader reportedly checked iOS versions and selected subsequent content through an iframe, including JIUJIU888/weifile.html.
This supports conditional payload delivery, not successful compromise of a physical Apple device.
No affected iOS version range, exploit CVE or threat-actor attribution has been established. Root cause and the campaign’s full impact remain under investigation.
Organizations should review third-party scripts and tag configurations, then hunt historical DNS, proxy and browser telemetry for the reported indicators.
Responders should distinguish blocked connections from delivered responses, executed JavaScript and confirmed outbound data transfers.
Preserving timestamps, headers, response bodies, initiator chains and sample hashes will help reconstruct exposure.
Validated malicious destinations should be blocked through available DNS, web gateway and endpoint controls, with enforcement tested.
Broad blocking of legitimate websites, Optimizely’s CDN or shared delivery addresses risks collateral disruption.
A later 30-minute recheck did not reproduce the scripts on tested sites, but that observation does not establish universal removal.
Assessments should prioritize demonstrated execution and visitor-data exposure rather than equating every alert with infection or confirmed compromise of the underlying website or service provider.
Indicators of compromise
Note: IP addresses and domains are intentionally defanged (e.g., [.] ) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC .
Artificial Intelligence
Cyber security Course
Cyber Security Resources
Cybersecurity
Information Gathering
Information Security Risks
Hackers Deploy PerfectPioneer RAT and KUKURAT Backdoor to Steal Sensitive Government Data
McDonald’s iOS App Flooded With Suspicious Push Notifications in Possible Cyberattack
Microsoft Warns Hackers Are Exploiting Microsoft 365 Outages to Launch Credential Phishing Attacks
GitLab Patches 37 Security Vulnerabilities Affecting CI/CD Pipelines, GitLab Pages, and MCP Server
Hacker Behind Massive GTA 6 Leak Pleads Guilty to Breaching Rockstar Games
Mozilla Releases Firefox 160 Security Update Fixing 99 Vulnerabilities, Including Sandbox Escape Flaws
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
