 Back Securityaffairs.Co
Phishing campaign exploits OAuth redirection to bypass defenses
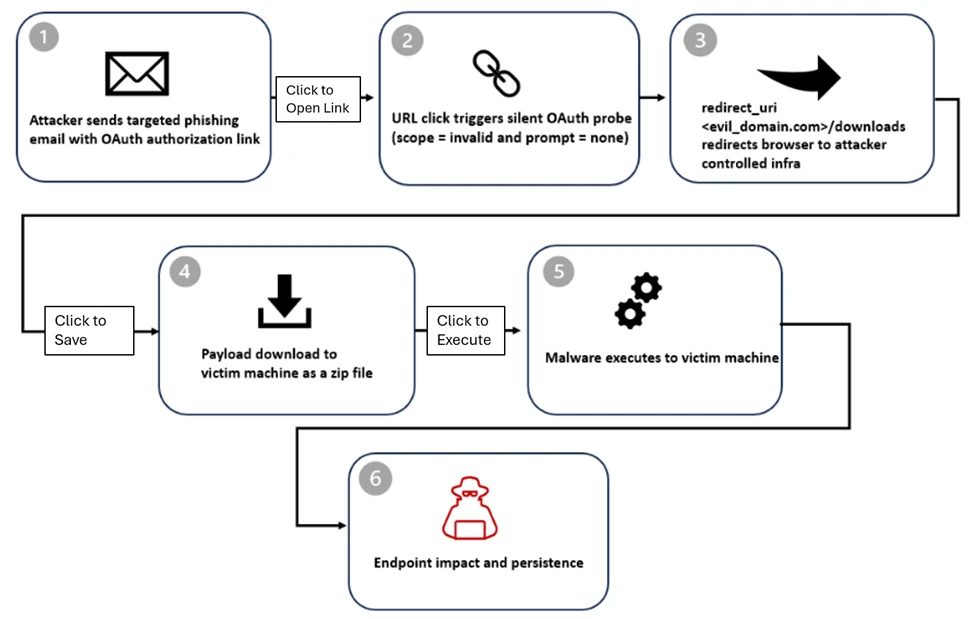
Microsoft researchers warn that threat actors abuse OAuth redirects to target government users and deliver malware. Microsoft has warned of phishing campaigns targeting government and public-sector organizations by abusing OAuth URL redirection. Instead of stealing credentials or exploiting software flaws, attackers leverage OAuth’s legitimate by-design behavior to bypass email and browser defenses. The tactic redirects […]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
