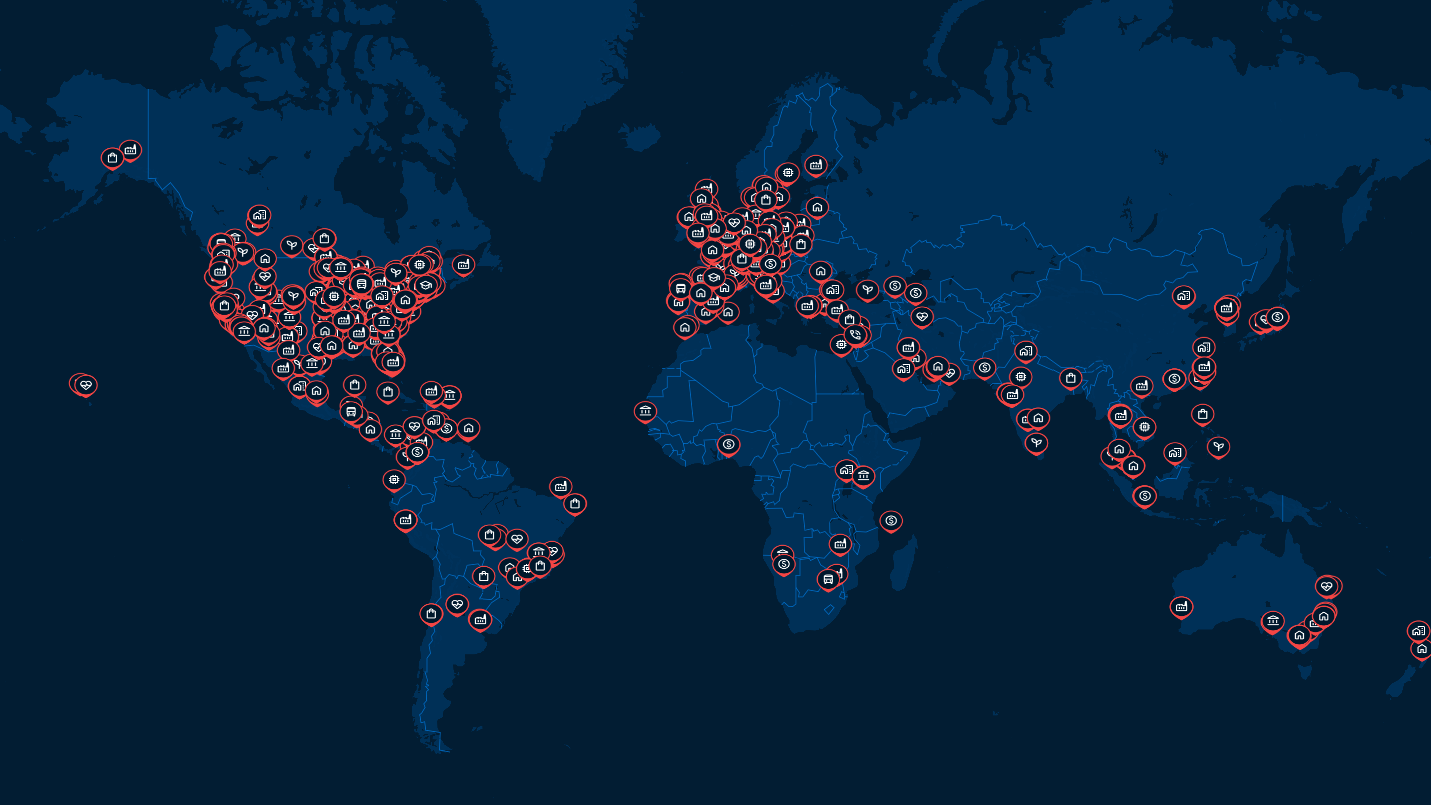
Ransomware activity in Q1 2026 reached 2,108 attack claims by 75 groups across 89 countries, a 7.9% increase over Q4. The quarter also saw Iranian destructive operations, North Korean tooling inside RaaS platforms, and Chinese state-affiliated ransomware campaigns converge with the cybercriminal ecosystem.
Handala, an Iranian group tied to the Ministry of Intelligence and Security (MOIS), turned Stryker's own device management platform into a weapon and wiped approximately 200,000 devices. This is the same group that conducted destructive ransomware and wiping attacks against Albania in 2022.
Separately, North Korean tooling surfaced inside Medusa campaigns, and a Chinese state-affiliated group was attributed to Warlock ransomware operations after exploiting SmarterMail zero-days, confirming Halcyon's earlier assessment of state-tied origins.
The Gentlemen broke into Leaders after splitting from Qilin's affiliate program, the fastest quarterly growth of any tracked group. Qilin retained the top position with accelerating volume across all three months. DragonForce completed its move to Leaders with a cartel model that lets affiliates operate under their own brand. Law firms entered the top five targeted industries, driven by concentrated INC Ransom campaigns.
Threat Actor Evolution
Most Attacked Countries
The UK absorbed more claimed attacks than Germany for the first time this quarter, moving to third.
Italy faced a heavier concentration of activity, and Thailand was drawn into the top ten by sustained TheGentlemen targeting across Southeast Asia. India also saw increased pressure at eighth.
The key trends highlight where threat actors arefocusing their innovation and which defenses organizationsshould prioritize.
North Korea, China, and Iran leveraged ransomware in specific operations across the quarter. Operators carrying exclusive North Korean state-developed implants appeared inside Medusa ransomware campaigns.
Separately, a Chinese state-affiliated group exploited SmarterMail zero-days to stage Warlock ransomware, confirming Halcyon's earlier assessment of state-tied origins.
On Iran, one government-tied group conducted a ransomware attack against a non-hospital healthcare facility in late February, and an Iranian state-tied group calling itself Handala conducted destructive wiper attacks against Middle East and US targets.
The quarter's top three groups, Qilin, Akira, and Play, all use encryption as their primary pressure tool.
Data-theft-only extortion proved unsustainable as payment rates for exfiltration-only incidents collapsed, pushing cybercriminals back toward encryption and confirming what Q4's declining returns had signaled.
Law firms entered the top five industries. INC Ransom posted 10 law firms in a single 48-hour window in early March, strongly suggesting compromise of a shared legal-technology vendor.
The campaign has continued, with INC claiming 30+ law firms since the start of the year. Breached firms expose not only their own data but privileged client communications, merger details, and litigation strategy.
The fastest observed breakout time was 27 seconds from initial access to lateral movement. Average breakout was just under 30 minutes.
The fastest quartile of intrusions reached data exfiltration within 72 minutes, four times faster than a year ago. At these speeds, a human analyst responding to an alert is already behind.
Activity increased from January through February. A Medusa attack on a Level I trauma center forced closure of 35 clinics for nine days. A data-theft group exposed HIV and substance-use treatment records for approximately 200,000 individuals.
A national oil pipeline operator in Romania and a water management authority (10 of 11 river basin organizations) were compromised. A U.S. water treatment facility was forced to manual operations for 16 hours.
A California municipality declared a state of emergency. Medusa demanded $800,000 from a county government affecting approximately 600,000 residents.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
